

这是什么?
 0 是一个用于安全研究的开源、自我演进、多模型 AI 框架,能够发现、验证并修复漏洞,由瑞士应用 AI 与网络安全研究实验室构建。
这是独立工具,还是需要托管版 0.security 服务?它是一个自包含的开源框架,可以使用你自己的模型访问权限在本地或 CI/CD 中通过 CLI 运行;托管的 0.security 服务是单独的、可选的付费层,提供额外的模型路由和工具。
它是一个自包含的开源框架,可以使用你自己的模型访问权限在本地或 CI/CD 中通过 CLI 运行;托管的 0.security 服务是单独的、可选的付费层,提供额外的模型路由和工具。怎么让它跑起来?把提供的安装提示词复制到你的编程智能体中以安装框架并阅读文档,或者进行快速安装,并在终端中配置好你自己的模型访问权限。
把提供的安装提示词复制到你的编程智能体中以安装框架并阅读文档,或者进行快速安装,并在终端中配置好你自己的模型访问权限。我需要自己的 LLM API 访问权限吗?需要,你要自带模型访问权限并自行配置连接;这个开源框架不附带内置模型。
需要,你要自带模型访问权限并自行配置连接;这个开源框架不附带内置模型。目前的发现结果有多可靠?这是一个研究预览版,覆盖范围和验证深度因工作流而异,你应当在采用之前检查证据并审查生成的修复。
这是一个研究预览版,覆盖范围和验证深度因工作流而异,你应当在采用之前检查证据并审查生成的修复。我可以把它指向任何我想测的目标吗?不行,你只能测试你拥有的或明确获权评估的系统。
不行,你只能测试你拥有的或明确获权评估的系统。托管的 0.security 服务是做什么的?它在开源框架之上增加了优化的模型路由、对非公开前沿网络模型的访问、专门构建的攻击运行时,以及经过筛选的攻击性工具链。
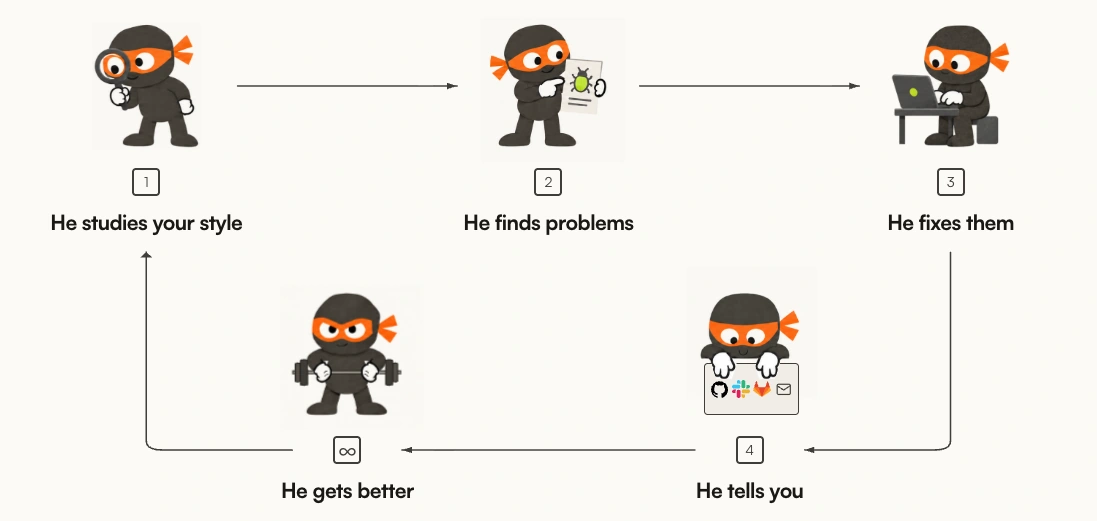
它在开源框架之上增加了优化的模型路由、对非公开前沿网络模型的访问、专门构建的攻击运行时,以及经过筛选的攻击性工具链。对这个框架来说,自我改进是什么意思?该框架会对自己的智能体和工具提出修改建议,根据基准进行评估,并保留表现更好的版本供以后的运行使用。
该框架会对自己的智能体和工具提出修改建议,根据基准进行评估,并保留表现更好的版本供以后的运行使用。为什么它被称为多人进攻性安全操作系统?它把聚焦的调查任务分派给多个拥有全新上下文和有限预算的子智能体,然后把它们的发现汇总到一个工作流中。
它把聚焦的调查任务分派给多个拥有全新上下文和有限预算的子智能体,然后把它们的发现汇总到一个工作流中。它输出什么格式?发现和验证结果可以导出为 JSON、Markdown 或 SARIF 报告。
发现和验证结果可以导出为 JSON、Markdown 或 SARIF 报告。What are similar projects?mantis, AI-Infra-Guard, strix, codex-security, shannon, cynative, Anthropic-Cybersecurity-Skills, Ai-jailbreak
mantis, AI-Infra-Guard, strix, codex-security, shannon, cynative, Anthropic-Cybersecurity-Skills, Ai-jailbreakWhich topics is it in?sast, cve, owasp, application-security, prompt-injection, fuzzing, llm-security, devsecops, security-research, binary-analysis, vulnerability-scanner, ai-security
sast, cve, owasp, application-security, prompt-injection, fuzzing, llm-security, devsecops, security-research, binary-analysis, vulnerability-scanner, ai-security