[!NOTE]
Shannon 3.0 is live: deeper security code analysis, more thoroughly vetted findings, a rebuilt CLI, native CI/CD, professional PDF reports, and SARIF.
Shannon is an autonomous, AI pentester for web applications and APIs.
It analyzes your source code, identifies attack paths, and executes real exploits to prove vulnerabilities before they reach production. No exploit, no report.
This repository is Shannon Open Source: the full agent, run locally from your command line.
Launch Shannon
npx @keygraph/shannon@latest
The interactive launcher will guide you through setup and your first pentest.
[!TIP]
AI agents and LLMs: start with llms.txt for a concise map of this repository, or use llms-full.txt for the README and docs combined into one file.
Shannon is an autonomous AI pentester developed by Keygraph. It performs security testing of web applications and their underlying APIs by combining source-code analysis with live exploitation.
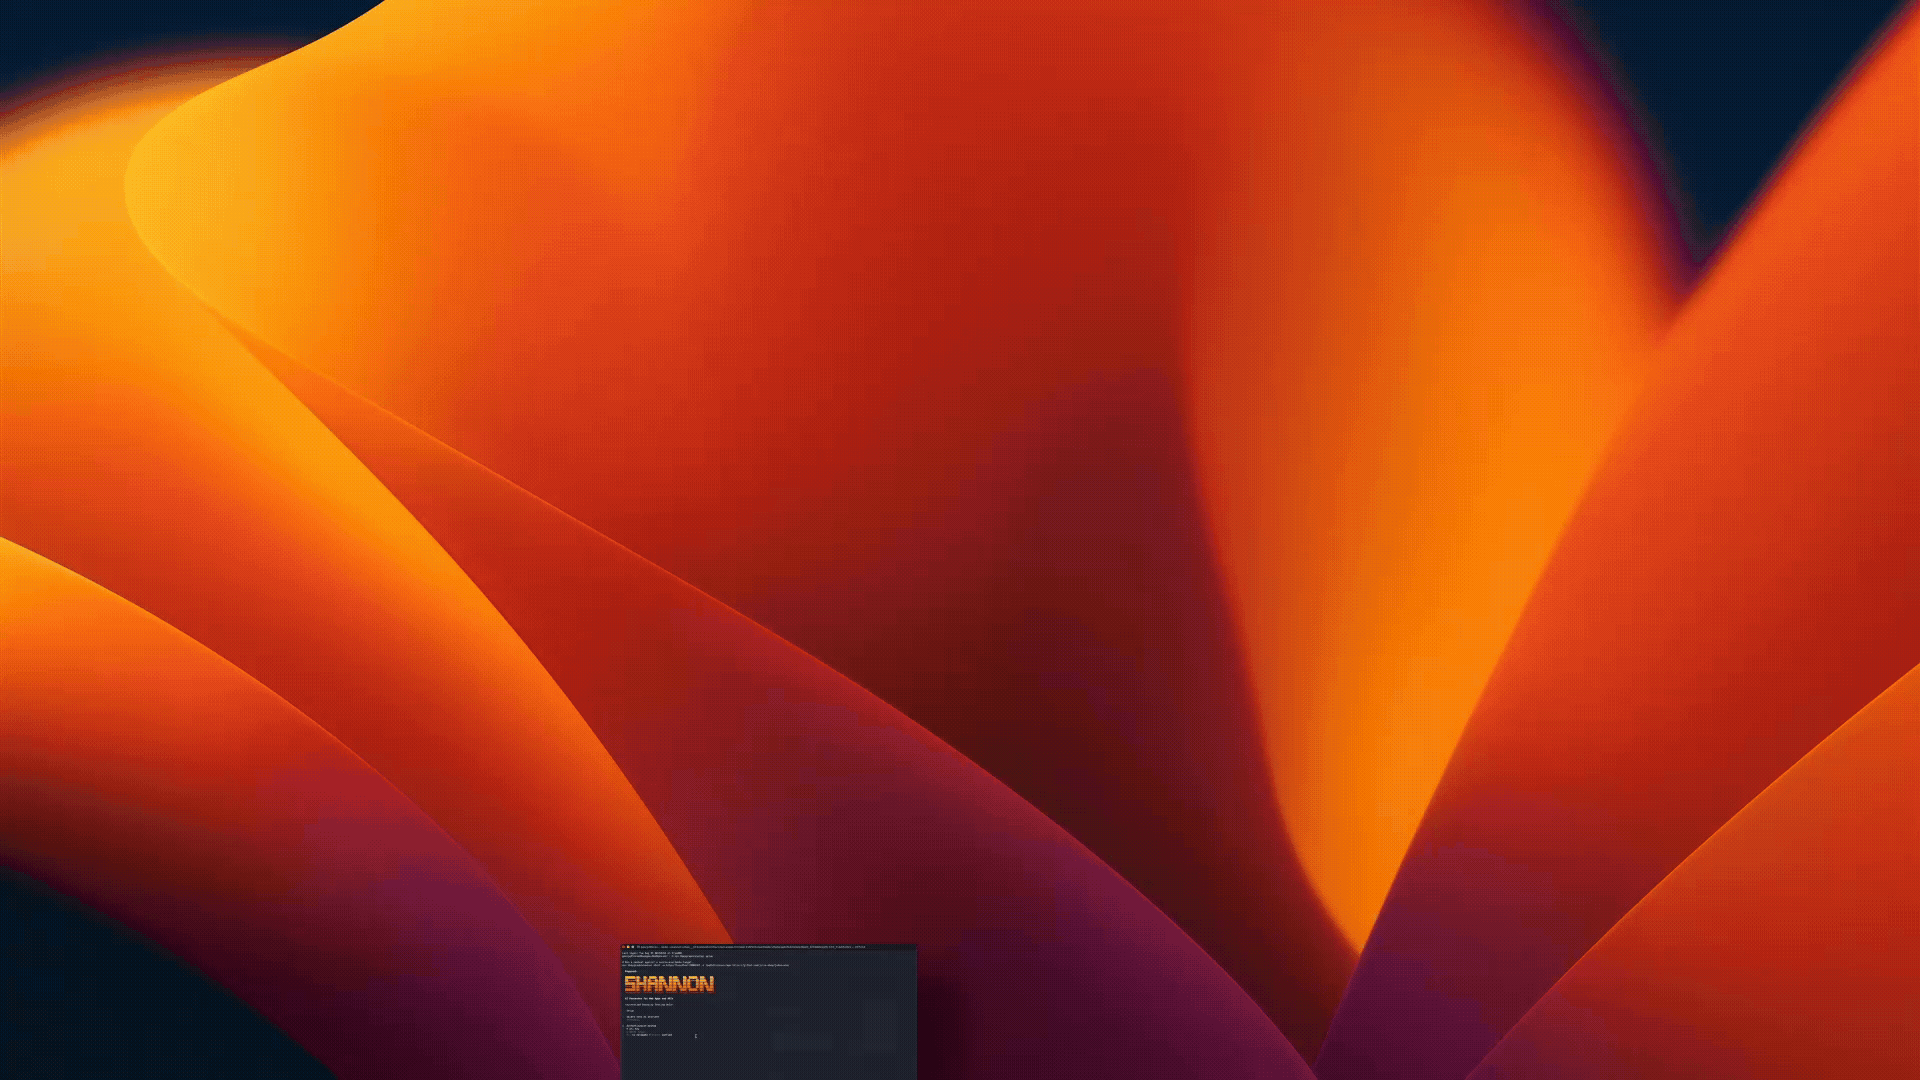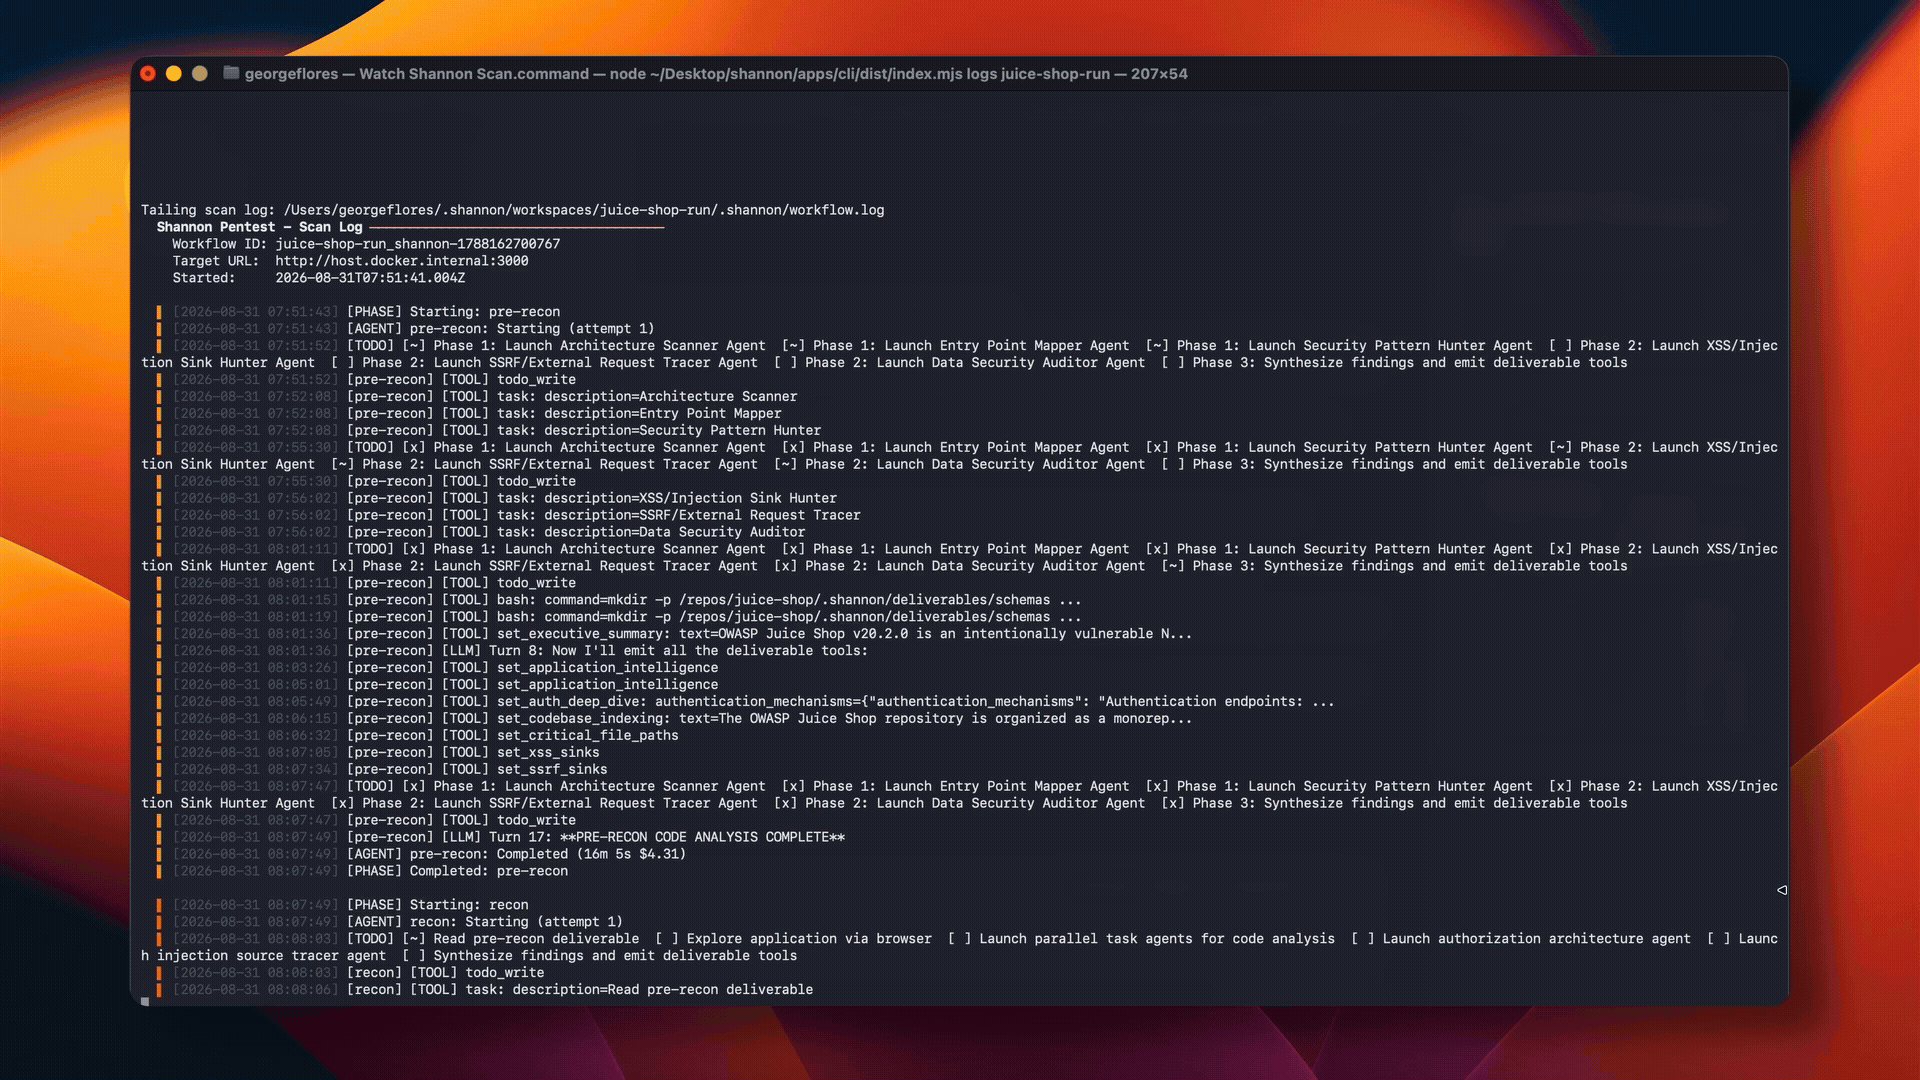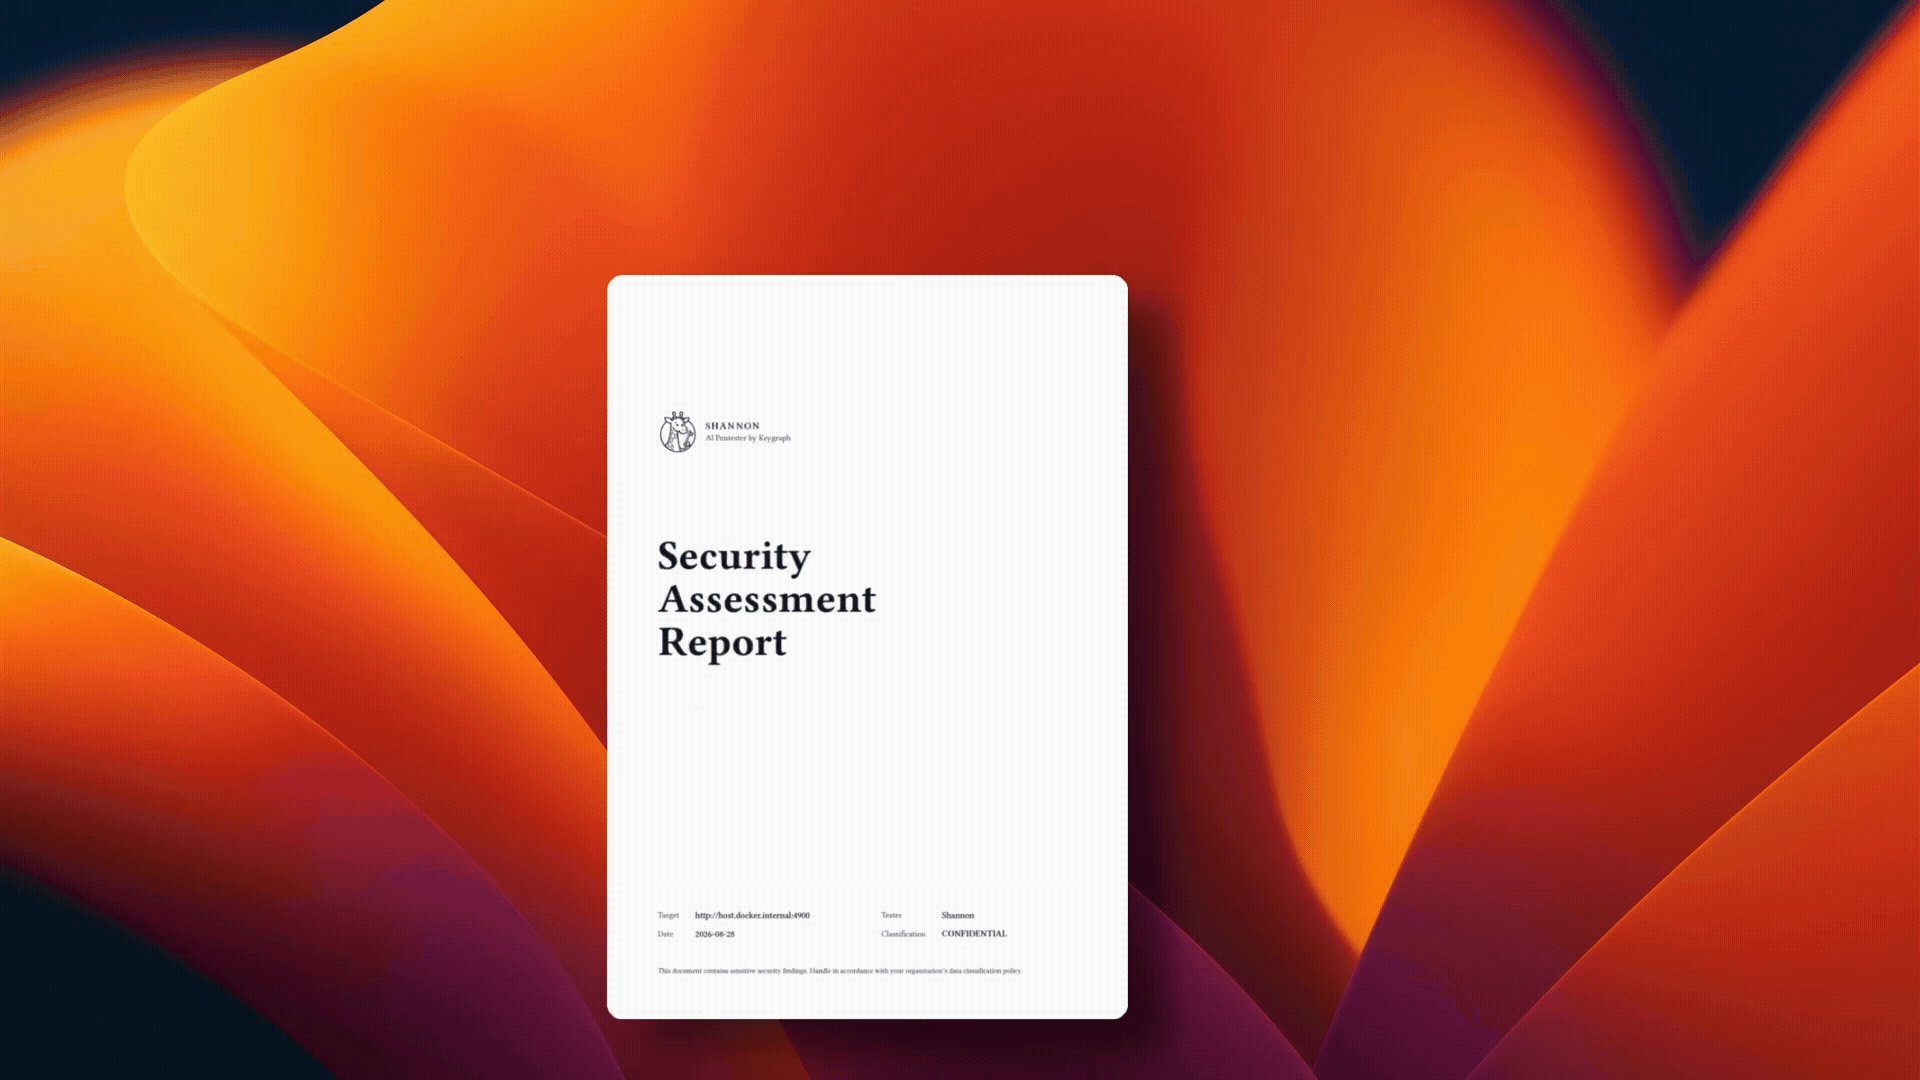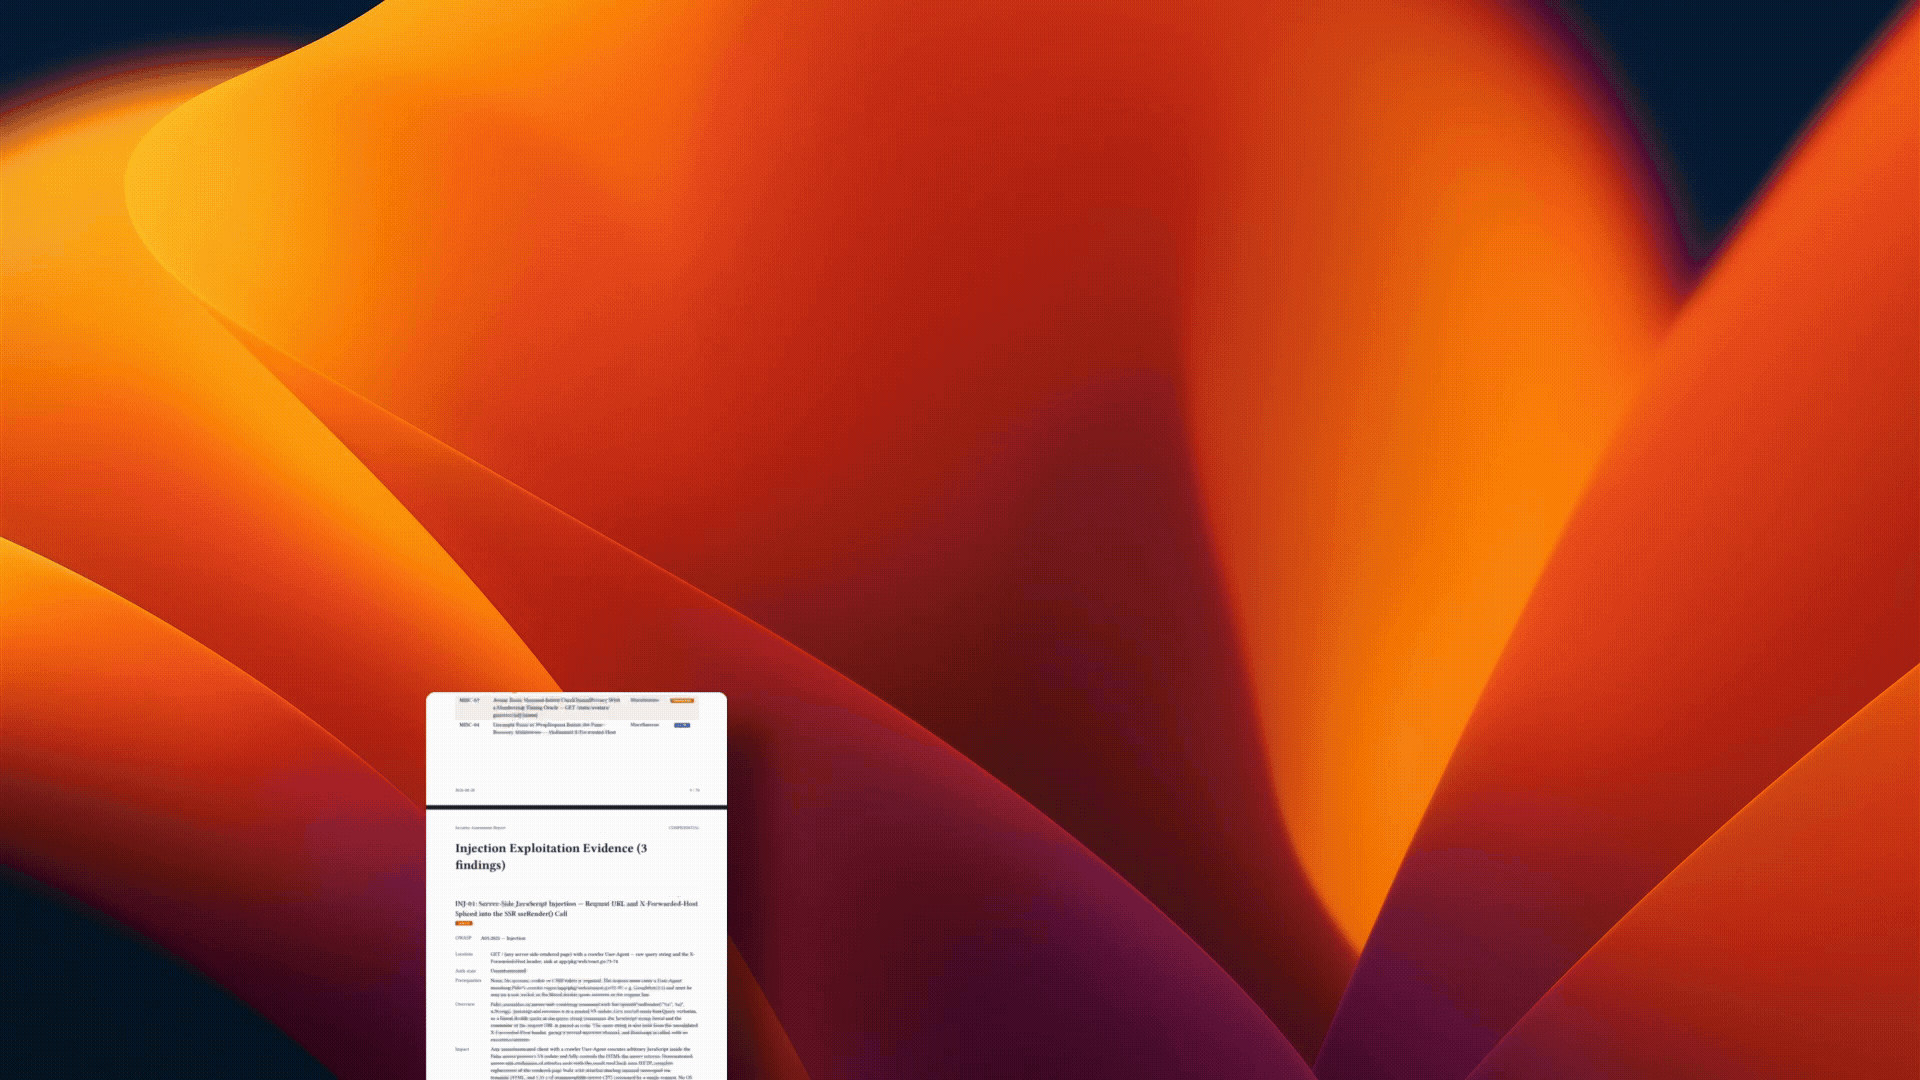
Shannon analyzes your web application's source code to identify potential attack vectors, then uses browser automation and command-line tools to execute real exploits against the running application and its APIs. Only vulnerabilities with a working proof-of-concept are included in the final report.
Shannon is the agent. This repository is Shannon Open Source, the standalone pentester you run yourself. The same Shannon also powers the Keygraph platform, Keygraph's commercial pentesting product. See Editions for how the two compare.
Why Shannon Exists
Thanks to tools like Claude Code and Cursor, your team ships code non-stop. But your penetration test? That happens once a year. This creates a massive security gap. For the other 364 days, you could be unknowingly shipping vulnerabilities to production.
Shannon closes that gap by providing on-demand, automated penetration testing that can run against every build or release.
Why "Shannon"?
It's named after Claude Shannon, the father of information theory. At its core, pentesting is an information problem: every probe reduces uncertainty about a system's state. The best tools maximize the signal gained from every request, turning those bits of knowledge into an exploit path.
Also, we wanted you to be able to say, "Hey Claude, run Shannon" to find all the security flaws in your vibe-coded app.
Not a replacement for human pentesters
Shannon is built to work alongside expert pentesters and red teamers, not replace them. Great pentesters understand the business, chain attacks in ways nobody anticipated, and bring years of judgment that current models can't match.
Shannon solves a different problem: there is far more software to test than security teams have time to cover. Critical systems get periodic expert assessments, while the long tail of internal apps, APIs, and fast-moving services rarely gets tested at all.
Shannon shifts pentesting left into the software development lifecycle (SDLC). Use it to run exploitation-backed tests against staging environments and releases at the cadence they actually ship, and save expert human time for the risks that need someone who knows the organization.
Shannon in Action
These reports are from Shannon Open Source scans of Photoview 2.4.0, one of the applications in Doyensec's comparison of Aikido and XBOW. We ran Shannon against the same application version and evaluated its results separately. Read the Doyensec study and our Shannon follow-up comparison for the methodology, limitations, costs, and results.
Node.js 18+: required for the recommended npx workflow.
AI provider credentials: Shannon runs on Anthropic, OpenAI, xAI, AWS Bedrock, and any other provider in the harness catalogue — each of which you can point at a proxy or LLM gateway through a custom base URL, and a model the catalogue does not yet carry can be described with a custom model configuration. You bring your own key, and Keygraph never proxies your model traffic. Shannon is provider-agnostic. See AI providers for suggested model IDs.
Cyber safeguards cleared with your provider: Anthropic and OpenAI apply real-time safeguards to cyber-security workloads, which can interrupt a scan mid-run. Complete their guidance for legitimate security testers before your first run - see AI providers.
Run Shannon
[!WARNING]
Shannon actively executes exploits. Run it only against applications and environments you own or have explicit written authorization to test. Do not run Shannon against production systems.
# Configure credentials with the interactive wizard.
npx @keygraph/shannon@latest setup

# Run a pentest against a source-available target.
npx @keygraph/shannon@latest start \
  -u https://your-app.com \
  -r /path/to/your/repo
Shannon pulls the worker image from Docker Hub, starts the required local infrastructure, mounts the target repository read-only inside an ephemeral worker container, and writes results to a local workspace.
For source builds, authenticated scans, provider-specific setup, and platform notes, see Documentation.
[!TIP]
Prefer to use a subscription instead of API credits?
OpenAI Codex: The latest version of Shannon supports ChatGPT Plus and Pro subscriptions. Follow the OpenAI Codex subscription setup guide to get started.
xAI (Grok): The latest version of Shannon supports xAI subscriptions. Follow the xAI subscription setup guide to get started.
Claude Code: The latest version of Shannon does not support Claude Code subscriptions. Follow the Claude Code subscription setup guide to use version 1.9.0, which is the final release built on the Claude Agent SDK.
Key Capabilities
No exploit, no report: Reports only vulnerabilities confirmed with a reproducible proof of concept, reducing speculative scanner noise.
Advanced code analysis: Maps architecture, trust boundaries, interfaces, data flows, and critical assets before sending credible attack paths to live pentesting agents.
Autonomous execution: Runs reconnaissance, analysis, exploitation, and reporting from a single command.
Live terminal experience: Simplifies scan setup and shows agent progress and results without exposing orchestration logs.
Authenticated testing: Supports credentials, login flows, TOTP, email authentication, focus areas, and rules of engagement through configuration.
OWASP-focused coverage: Tests for exploitable injection, XSS, SSRF, broken authentication, and broken authorization.
Resumable workspaces: Resumes interrupted scans without repeating completed work.
Native CI/CD integrations: Runs through the official GitHub Action or GitLab CI/CD component, preserves artifacts, publishes findings, and gates releases on proven vulnerabilities.
Multi-format reports: Produces evidence-rich PDF and Markdown reports plus JSON and SARIF 2.1.0. SARIF is enabled by default for exploit-mode scans.
Provider agnostic and BYOK: Supports Anthropic, OpenAI, xAI, AWS Bedrock, compatible APIs and LLM gateways, and local models served through Ollama, vLLM, or LM Studio.
Private by design: Runs in your infrastructure, stores results locally, and sends model requests directly to your chosen endpoint. A local endpoint keeps data inside your environment.
CI/CD Integrations
Shannon can run continuously against deployed staging and development environments through official integrations for GitHub Actions and GitLab CI/CD.
Both integrations:
analyze the checked-out source repository while attacking a running target;
preserve PDF, Markdown, and SARIF reports as pipeline artifacts;
preserve scan and agent logs for debugging, including incomplete runs;
support pull-request, release, and scheduled pentests;
distinguish an incomplete assessment from a completed scan with no findings; and
optionally fail the pipeline when Shannon exploits a vulnerability at or above a configured severity threshold.
A code-analysis hypothesis does not fail the pipeline. Severity gates count only findings with status: exploited.
The Action defaults repo to the checked-out GitHub workspace. It uploads one artifact containing the security assessment reports and SARIF, plus a separate run artifact containing scan and agent logs. Enabling upload-sarif publishes supported findings to GitHub code scanning.
Requirements:
a private repository;
a runner with Docker and Docker Compose v2;
access to the running staging or development target; and
a model-provider credential stored as a GitHub Actions secret.
Shannon Open Source is a complete autonomous pentester, especially well suited to individual developers and small teams running focused security tests locally or in CI/CD.
Keygraph Enterprise Platform is for organizations that need a shared platform for continuous agentic pentesting/AppSec across many teams, repositories, and environments. It centralizes deeper analysis, vulnerability management, remediation, verification, governance, and reporting so teams do not have to assemble and maintain those workflows themselves.
Recon and vulnerability analysis explores the running application, ties runtime behavior back to the source, and runs specialized agents across Injection, XSS, SSRF, Authentication, and Authorization.
Agentic security code analysis maps the application's architecture, trust boundaries, exposed interfaces, dependencies, data flows, and high-risk assets, then opens targeted investigations against them.
Finding reconciliation merges both streams of candidates, deduplicates the overlap, and groups what remains into an exploitation queue.
Exploitation agents attempt real proof-of-concept attacks against the running application.
Validation throws out every candidate Shannon can't demonstrate.
Reporting produces PDF and Markdown reports with the evidence attached, plus structured JSON and SARIF for downstream systems.
Only live-validated vulnerabilities become Shannon pentest findings or count toward CI/CD severity gates.
Each scan runs in an ephemeral Docker container with an isolated workspace and per-invocation orchestration.
Shannon is not a passive scanner. Its exploitation agents can create users, submit forms, mutate application state, trigger outbound requests, and otherwise affect the target system. Use sandboxed, staging, or local development environments with disposable data.
You are responsible for using Shannon legally and ethically. Do not point Shannon at systems, repositories, or applications you do not own or do not have explicit authorization to test.
Important limitations:
Shannon Open Source is tuned for fast, code-informed pentesting in everyday development and CI/CD. Exhaustive agentic SAST, broader scanner coverage, centralized governance, and full-lifecycle vulnerability management are delivered through the Keygraph Enterprise Platform.
Findings still require human review. LLM-generated reports can contain weakly supported or incorrect details.
Anthropic, OpenAI, xAI, and AWS Bedrock are built-in providers, and any other provider in the harness catalogue works too — each reachable through a custom base URL that points it at a proxy or LLM gateway. Model capability varies, and a model that does n
shannon (KeygraphHQ/shannon)
Choose a tag and it will appear here. With no tags selected, all catalog projects are shown.
Searching Database…
Choose a tag and it will appear here. With no tags selected, all catalog projects are shown.

 Shannon 是一个自主运行的 AI 渗透测试工具,它会分析你 Web 应用的源代码,梳理攻击向量,然后对运行中的应用实际执行漏洞利用,在问题进入生产环境之前证明其确实存在——“没有利用证明,就没有报告”。