

What is this?
 Sn1per is an offensive-security platform that bundles reconnaissance, vulnerability scanning, exploitation and reporting into one workspace, orchestrating 600+ exploits and 90+ third-party tools for pentesters and attack-surface-management teams.
Is this a CLI toolkit or a hosted web platform?The free edition is a Linux bash-based CLI installed to /usr/share/sniper that orchestrates dozens of external security tools; the paid Professional and Enterprise editions add an actual web UI on top of the same scan engine.
The free edition is a Linux bash-based CLI installed to /usr/share/sniper that orchestrates dozens of external security tools; the paid Professional and Enterprise editions add an actual web UI on top of the same scan engine.How do I get it running?On Kali, Ubuntu, Debian or Parrot, run sudo bash install.sh (add force to skip the confirmation prompt). There's also an official Docker image on Docker Hub and an AWS Marketplace EC2 AMI with Sn1per preinstalled.
On Kali, Ubuntu, Debian or Parrot, run sudo bash install.sh (add force to skip the confirmation prompt). There's also an official Docker image on Docker Hub and an AWS Marketplace EC2 AMI with Sn1per preinstalled.Do I need accounts for the integrations like Nessus or Burp Suite?Sn1per itself just needs root on a supported Linux distro, but several of its 90+ featured integrations (Nessus, Burp Suite Pro, OWASP ZAP, Shodan, Censys) are separate third-party tools or services with their own licenses that Sn1per drives, not ships.
Sn1per itself just needs root on a supported Linux distro, but several of its 90+ featured integrations (Nessus, Burp Suite Pro, OWASP ZAP, Shodan, Censys) are separate third-party tools or services with their own licenses that Sn1per drives, not ships.Does the free Community Edition give me the full platform?The Community Edition in this repo is source-available under a custom EULA and has the core scan engine but no Web UI; Professional ($984/year) caps you to 5 workspaces and 30 assets per workspace, with only Enterprise lifting those quotas.
The Community Edition in this repo is source-available under a custom EULA and has the core scan engine but no Web UI; Professional ($984/year) caps you to 5 workspaces and 30 assets per workspace, with only Enterprise lifting those quotas.Does any scan data leave my own servers?Sn1per is designed to run fully on-prem, including air-gapped setups where nothing is sent to the vendor.
Sn1per is designed to run fully on-prem, including air-gapped setups where nothing is sent to the vendor.What scan modes does Sn1per offer?It has over a dozen modes such as normal, stealth (low-noise), flyover (fast multi-host scanning), airstrike, nuke (full audit), discover (walks a CIDR), webscan (Burp + Arachni) and vulnscan (OpenVAS), plus mass variants that read a target list from a file.
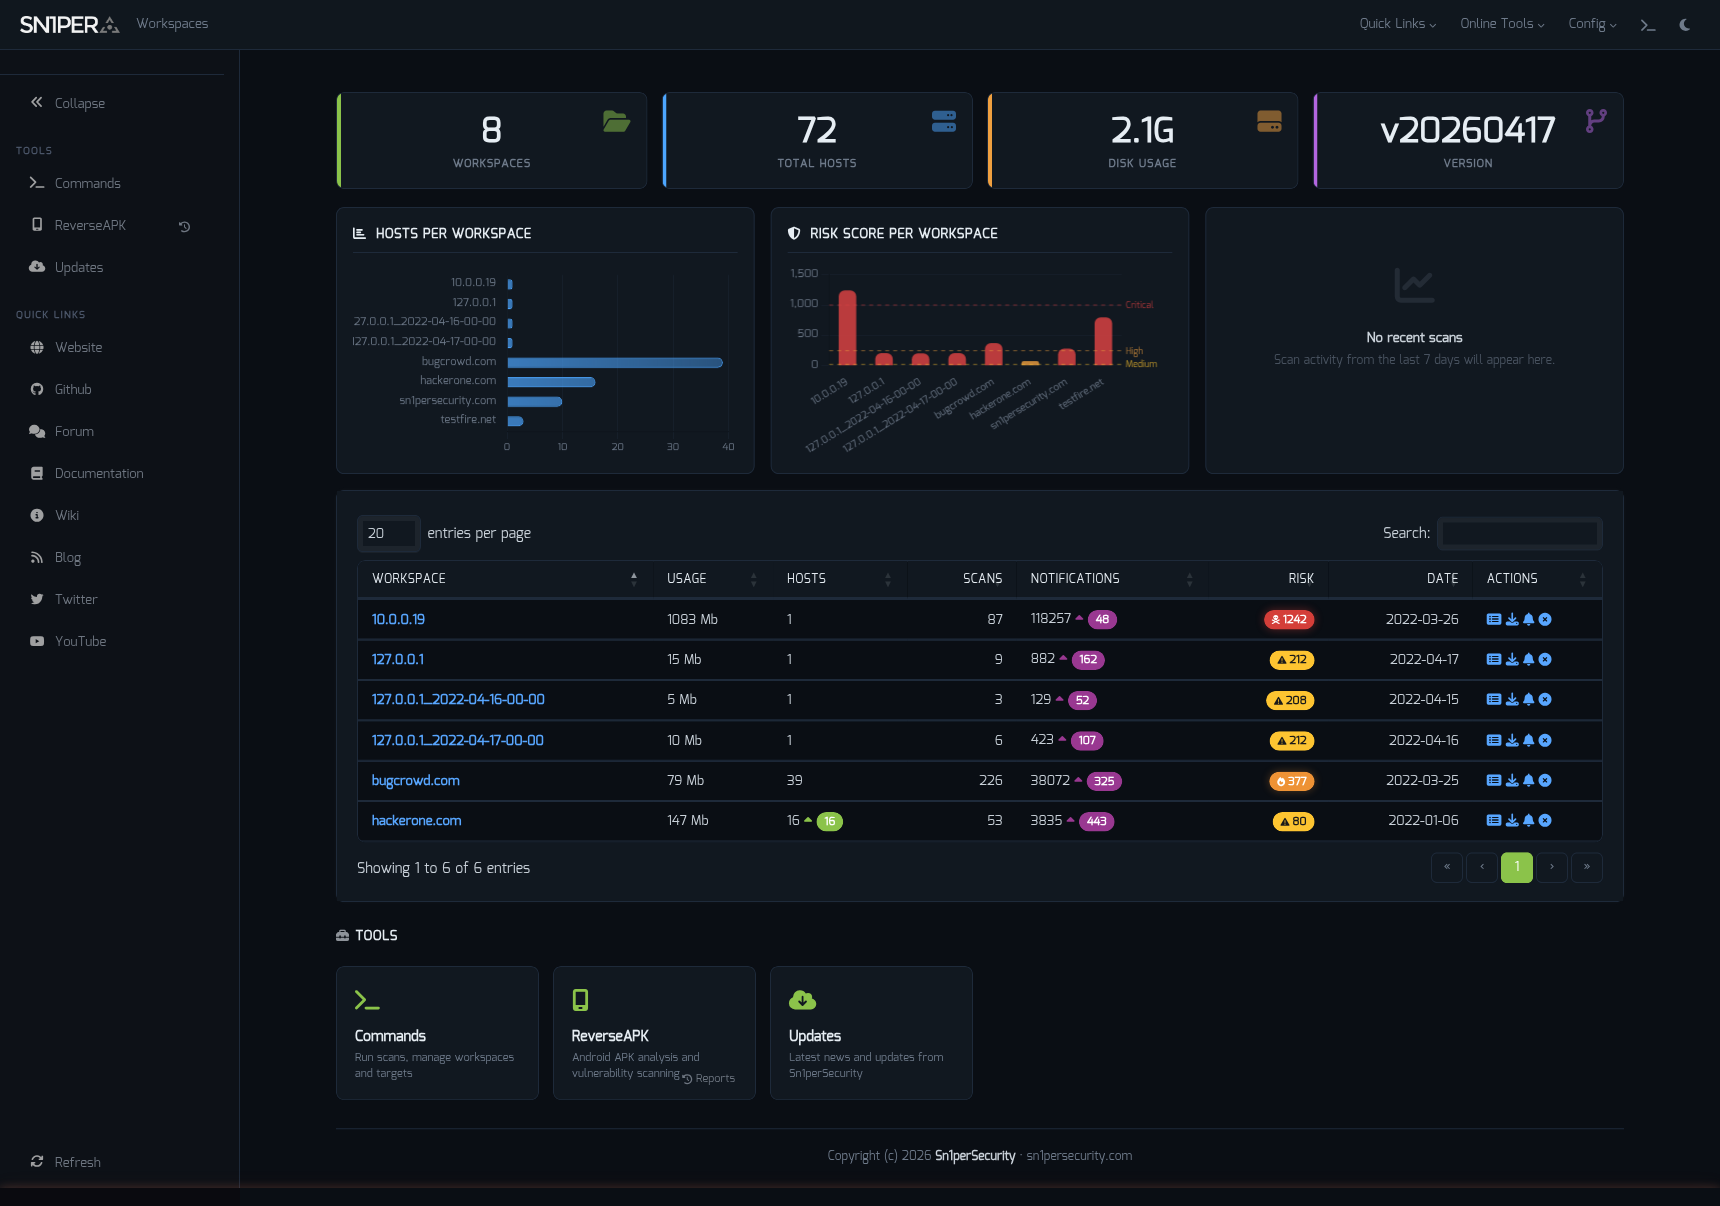
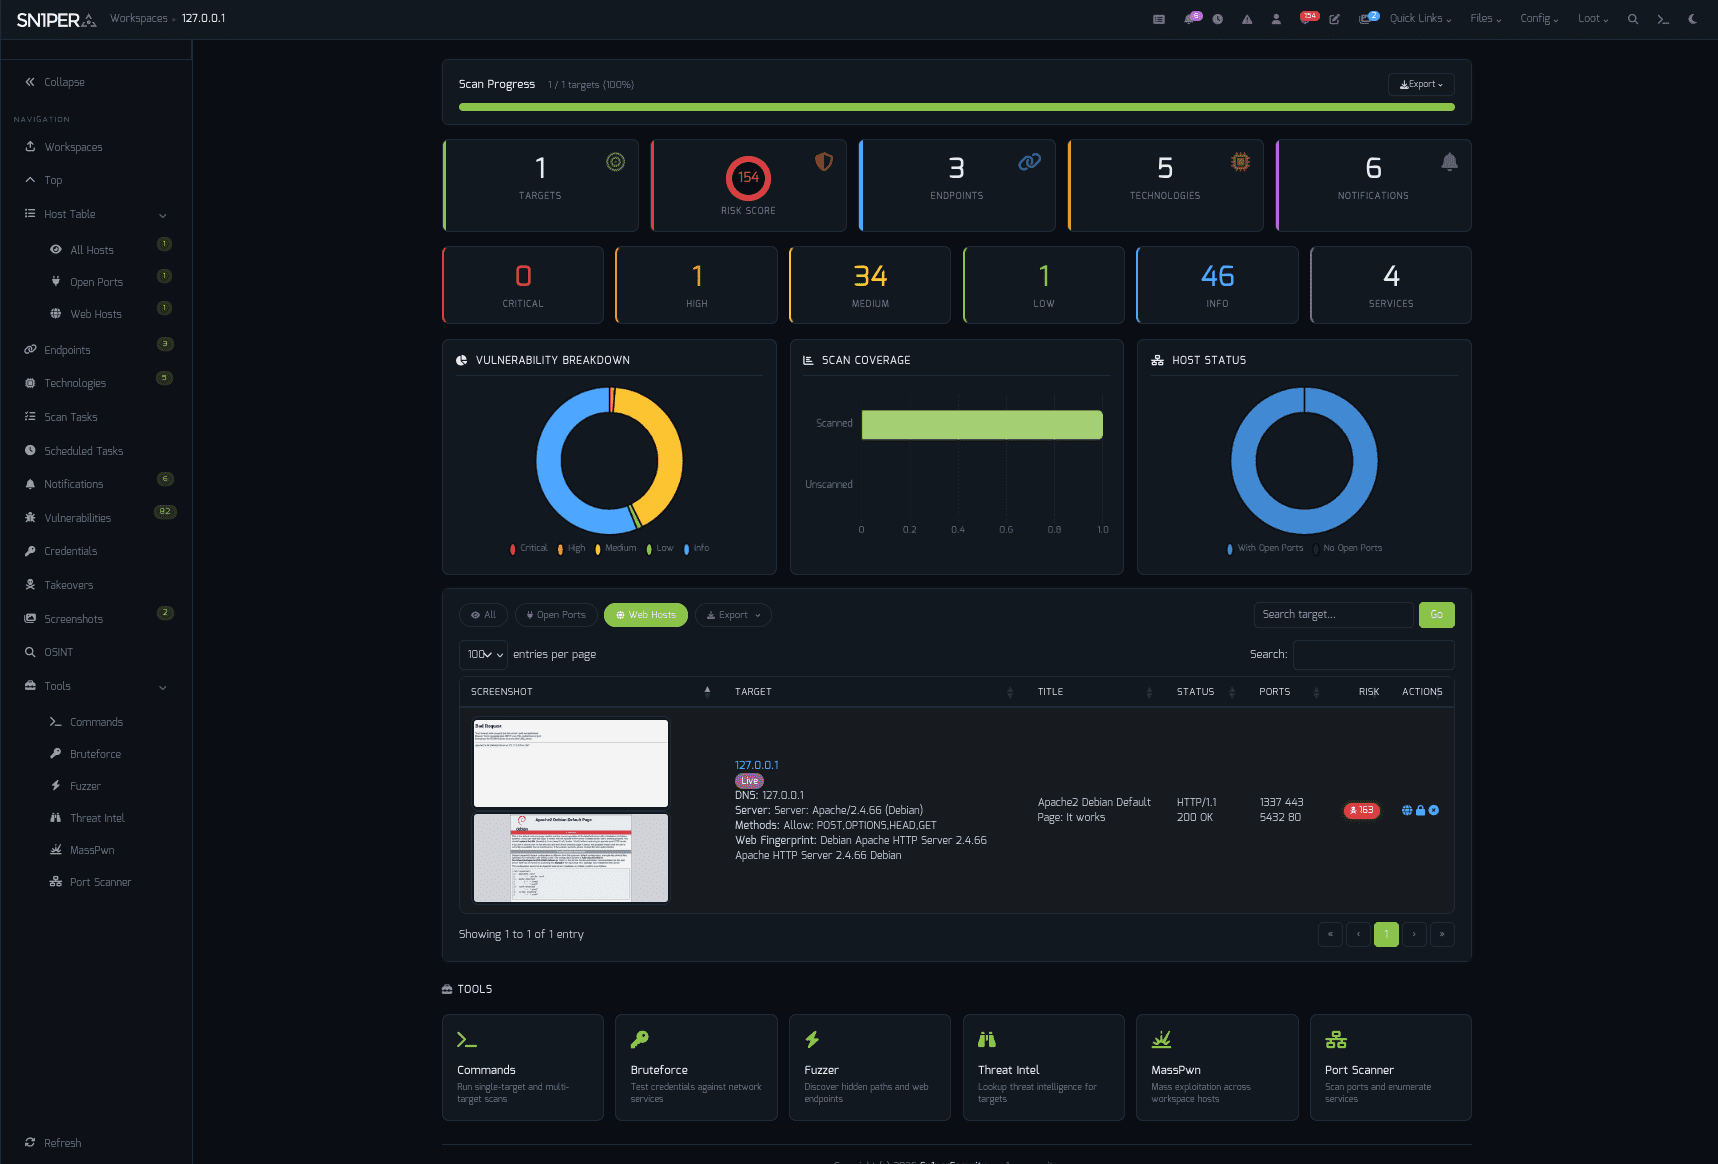
It has over a dozen modes such as normal, stealth (low-noise), flyover (fast multi-host scanning), airstrike, nuke (full audit), discover (walks a CIDR), webscan (Burp + Arachni) and vulnscan (OpenVAS), plus mass variants that read a target list from a file.What changed in the 2026 release?Sn1per Professional 2026 added Docker-first deployment, a Bootstrap 5/Tabler UI, a Workspace Navigator, CSV/Excel/PDF reports, a JSON API v1.0 for CI/SOAR/SIEM pipelines, and new modules for ReverseAPK, MassPwn, Threat Intel, Nessus and Burp.
Sn1per Professional 2026 added Docker-first deployment, a Bootstrap 5/Tabler UI, a Workspace Navigator, CSV/Excel/PDF reports, a JSON API v1.0 for CI/SOAR/SIEM pipelines, and new modules for ReverseAPK, MassPwn, Threat Intel, Nessus and Burp.What third-party tools does it tie together?It natively integrates vulnerability scanners (Nessus, OpenVAS, GVM, Nuclei), web testers (Burp Suite Pro, OWASP ZAP, WPScan), exploitation via Metasploit, recon sources like Shodan, Censys, Hunter.io and VirusTotal, plus Slack and GitHub API notifications.
It natively integrates vulnerability scanners (Nessus, OpenVAS, GVM, Nuclei), web testers (Burp Suite Pro, OWASP ZAP, WPScan), exploitation via Metasploit, recon sources like Shodan, Censys, Hunter.io and VirusTotal, plus Slack and GitHub API notifications.Why did the authors build Sn1per instead of using separate scanners?The team, pentesters since 2015, wanted to stop stitching together a dozen separate recon/scan/exploit/report tools and instead ship one workflow with active exploit verification to cut out false positives.
The team, pentesters since 2015, wanted to stop stitching together a dozen separate recon/scan/exploit/report tools and instead ship one workflow with active exploit verification to cut out false positives.What are similar projects?bbot, Claude-Red, awesome-hacker-search-engines, spiderfoot, wifit3, redamon, OneForAll, hexstrike-ai
bbot, Claude-Red, awesome-hacker-search-engines, spiderfoot, wifit3, redamon, OneForAll, hexstrike-aiWhich topics is it in?osint-framework, pentest-tool, pentesting-tools, osint-tool, hacking-tools, recon, bugbounty, owasp, malware, reconnaissance, vulnerability-scanner, network-security
osint-framework, pentest-tool, pentesting-tools, osint-tool, hacking-tools, recon, bugbounty, owasp, malware, reconnaissance, vulnerability-scanner, network-security