


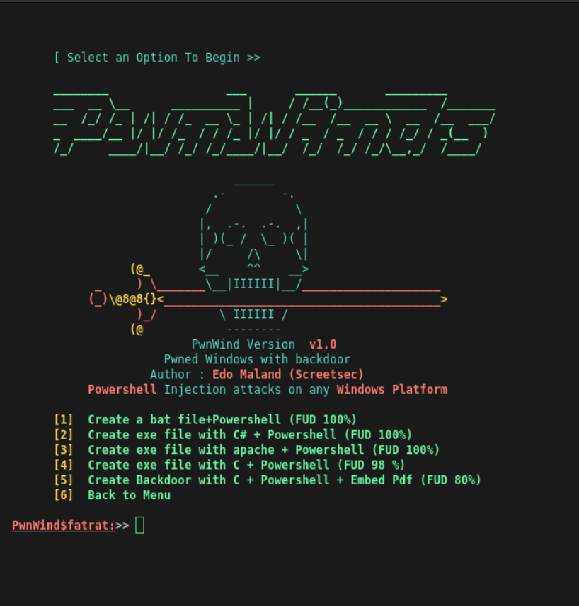
这是干什么的?
 TheFatRat 是一款漏洞利用工具,能把知名 payload 编译成恶意软件——一种简单的方法,可以生成能躲过大多数杀毒软件的后门。
它实际生成什么?后门文件——即匹配目标操作系统、格式各不相同的 payload——外加一个本地或远程监听器,用来接收传来的连接。
后门文件——即匹配目标操作系统、格式各不相同的 payload——外加一个本地或远程监听器,用来接收传来的连接。我怎么把它跑起来?克隆仓库并运行 setup.sh;如果安装失败,可以运行自带的 chktools 脚本,它会检查各组件版本是否正确并给出修复建议。
克隆仓库并运行 setup.sh;如果安装失败,可以运行自带的 chktools 脚本,它会检查各组件版本是否正确并给出修复建议。我需要装 Metasploit 吗?需要——TheFatRat 完全自动化调用 MSFvenom 和 Metasploit,所以一套能正常运行的 Metasploit 环境(通常装在 Kali Linux 上)是它背后的引擎。
需要——TheFatRat 完全自动化调用 MSFvenom 和 Metasploit,所以一套能正常运行的 Metasploit 环境(通常装在 Kali Linux 上)是它背后的引擎。我真的可以用它吗?仅限教学用途:未经事先双方同意就攻击目标是违法的,开发者对任何滥用行为或造成的损害概不负责。
仅限教学用途:未经事先双方同意就攻击目标是违法的,开发者对任何滥用行为或造成的损害概不负责。它生成的恶意软件能在哪些系统上运行?编译出的恶意软件可以在 Linux、Windows、Mac 和 Android 上运行,后门会按目标系统的类别分别生成。
编译出的恶意软件可以在 Linux、Windows、Mac 和 Android 上运行,后门会按目标系统的类别分别生成。它能把 payload 藏进真实的文件或应用里吗?可以——项目的演示视频包括把木马嵌入 Debian 软件包、把 payload 注入原版 Android APK,以及把 payload 与 JPG 图片捆绑。
可以——项目的演示视频包括把木马嵌入 Debian 软件包、把 payload 注入原版 Android APK,以及把 payload 与 JPG 图片捆绑。它自带哪些投递辅助功能?它会自动创建用于 USB/CDROM 攻击的 AutoRun 文件,检测你的外部 IP 和网卡地址,还附带一个用于增大文件体积的 file pumper。
它会自动创建用于 USB/CDROM 攻击的 AutoRun 文件,检测你的外部 IP 和网卡地址,还附带一个用于增大文件体积的 file pumper。README 里提到了哪些同类工具?Veil Framework、Shellter、TrustedSec 的 Unicorn、MSFvenom Payload Creator(MSFPC)、Venom 和 Phantom-Evasion 被列为类似的后门生成与杀软绕过工具。
Veil Framework、Shellter、TrustedSec 的 Unicorn、MSFvenom Payload Creator(MSFPC)、Venom 和 Phantom-Evasion 被列为类似的后门生成与杀软绕过工具。What are similar projects?Claude-Red, nishang, Decepticon, Red-Teaming-Toolkit, mimikatz, PowerSploit, Awesome-Hacking-Resources, zphisher
Claude-Red, nishang, Decepticon, Red-Teaming-Toolkit, mimikatz, PowerSploit, Awesome-Hacking-Resources, zphisherWhich topics is it in?post-exploitation, kali-linux, remote, malware, bypass, remote-access, trojan, exploit, hacking-tool, offensive-security, pentesting, penetration-testing
post-exploitation, kali-linux, remote, malware, bypass, remote-access, trojan, exploit, hacking-tool, offensive-security, pentesting, penetration-testing