
big-list-of-naughty-strings README

The project's README from github.com/minimaxir/big-list-of-naughty-strings. As one markdown file: README.md.

Big List of Naughty Strings

The Big List of Naughty Strings is an evolving list of strings which have a high probability of causing issues when used as user-input data. This is intended for use in helping both automated and manual QA testing; useful for whenever your QA engineer walks into a bar.

Why Test Naughty Strings?

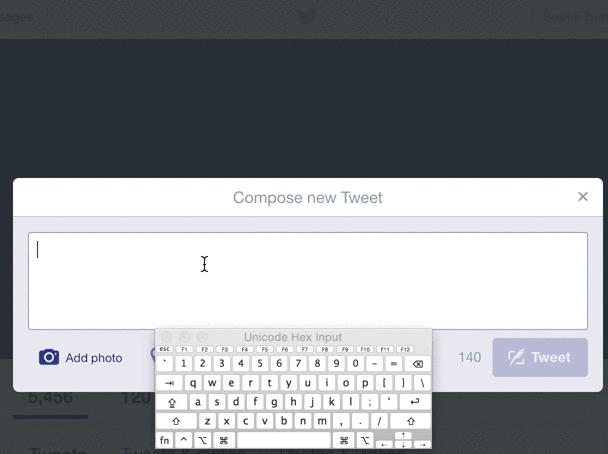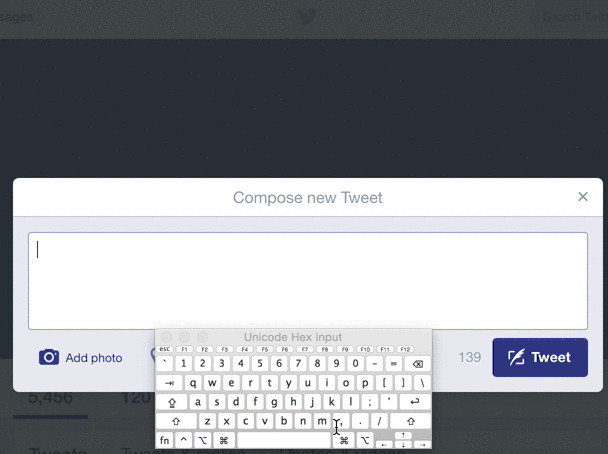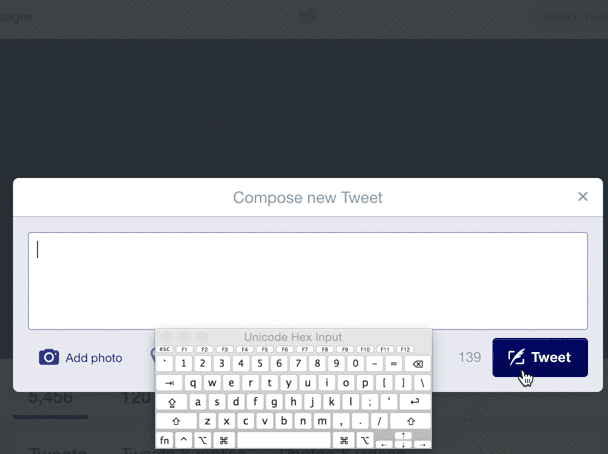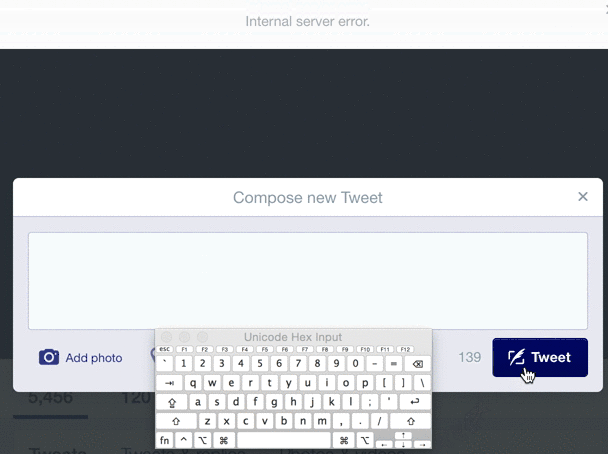
Even multi-billion dollar companies with huge amounts of automated testing can't find every bad input. For example, look at what happens when you try to Tweet a zero-width space (U+200B) on Twitter:

Although this is not a malicious error, and typical users aren't Tweeting weird unicode, an "internal server error" for unexpected input is never a positive experience for the user, and may in fact be a symptom of deeper string-validation issues. The Big List of Naughty Strings is intended to help reveal such issues.

Usage

blns.txt consists of newline-delimited strings and comments which are preceded with #. The comments divide the strings into sections for easy manual reading and copy/pasting into input forms. For those who want to access the strings programmatically, a blns.json file is provided containing an array with all the comments stripped out (the scripts folder contains a Python script used to generate the blns.json).

Contributions

Feel free to send a pull request to add more strings, or additional sections. However, please do not send pull requests with very-long strings (255+ characters), as that makes the list much more difficult to view.

Likewise, please do not send pull requests which compromise manual usability of the file. This includes the EICAR test string, which can cause the file to be flagged by antivirus scanners, and files which alter the encoding of blns.txt. Also, do not send a null character (U+0000) string, as it changes the file format on GitHub to binary and renders it unreadable in pull requests. Finally, when adding or removing a string please update all files when you perform a pull request.

Disclaimer

The Big List of Naughty Strings is intended to be used for software you own and manage. Some of the Naughty Strings can indicate security vulnerabilities, and as a result using such strings with third-party software may be a crime. The maintainer is not responsible for any negative actions that result from the use of the list.

Additionally, the Big List of Naughty Strings is not a fully-comprehensive substitute for formal security/penetration testing for your service.

Library / Packages

Various implementations of the Big List of Naughty Strings have made it to various package managers. Those are maintained by outside parties, but can be found here:

Library Link
Node https://www.npmjs.com/package/blns
Node https://www.npmjs.com/package/big-list-of-naughty-strings
.NET https://github.com/SimonCropp/NaughtyStrings
PHP https://github.com/mattsparks/blns-php
C++ https://github.com/eliabieri/blnscpp

Please open a PR to list others.

Maintainer/Creator

Max Woolf (@minimaxir)

Social Media Discussions

License

MIT

big-list-of-naughty-strings (minimaxir/big-list-of-naughty-strings)

Searching Database…

这是什么?这是一组精心整理的字符串,用作用户输入时很可能导致软件出错,旨在帮助对输入验证进行 QA 测试。
这是测试工具,还是只是普通的数据文件?它只是数据,不是工具:包含带注释和分节、便于人工阅读的 blns.txt,以及为程序调用而精简的 blns.json 数组。
我到底该怎么在测试中使用这些字符串?将 blns.txt 中的字符串复制粘贴到输入表单中进行手动 QA,或将 blns.json 加载到自动化测试套件中,作为输入数据使用。
对于能往这个列表里添加什么内容,有什么规定吗?贡献者应避免添加超长字符串(255 个字符及以上)、EICAR 杀毒软件测试字符串以及空字符(null),因为这些会影响手动阅读,或在 GitHub 上损坏文件。
这个列表是给谁用的?面向需要对应用程序进行输入验证、编码处理和 Unicode 边界情况压力测试的 QA 工程师和开发人员。
有没有适用于其他编程语言的包?有的,社区维护的实现可用于 Node、.NET、PHP 和 C++ 的包管理器,README 中有相关链接。
在实践中,使用 Naughty Strings 进行测试为什么重要?即使是大公司也会漏掉边界情况。README 中提到,有人在 Twitter 上发布了一个零宽空格(U+200B),结果导致内部服务器错误,这说明意外输入会如何破坏真实系统。
这个列表还在更新吗?仍在更新。它被描述为一个持续演进的列表,维护者 Max Woolf 接受添加新字符串或新分节的拉取请求。
Creator
minimaxir
Size
0.3 MB
Stars
47.7K
Updated
CommitApr 17
Age
11y
Commits · 90 Days