Что это такое?
 Это подобранная коллекция строк, которые с высокой вероятностью ломают программное обеспечение при использовании в качестве пользовательского ввода. Она помогает QA-тестированию проверки ввода.
Это инструмент для тестирования или просто файл с данными?Это просто данные, а не инструмент: удобочитаемый файл blns.txt с комментариями и разделами, а также упрощённый массив в blns.json для программного использования.
Это просто данные, а не инструмент: удобочитаемый файл blns.txt с комментариями и разделами, а также упрощённый массив в blns.json для программного использования.Как мне на самом деле использовать эти строки в своих тестах?Копируйте строки из blns.txt и вставляйте их в формы ввода для ручного QA или загружайте blns.json в свой автоматизированный набор тестов, чтобы подавать строки как входные данные.
Копируйте строки из blns.txt и вставляйте их в формы ввода для ручного QA или загружайте blns.json в свой автоматизированный набор тестов, чтобы подавать строки как входные данные.Есть ли правила, что можно добавлять в список?Участников просят не добавлять очень длинные строки (255+ символов), тестовую строку антивируса EICAR и нулевые символы, так как они мешают ручному чтению или портят файл на GitHub.
Участников просят не добавлять очень длинные строки (255+ символов), тестовую строку антивируса EICAR и нулевые символы, так как они мешают ручному чтению или портят файл на GitHub.Для кого предназначен этот список?Для QA-инженеров и разработчиков, которым нужно проверять на прочность валидацию ввода, обработку кодировок и граничные случаи unicode в своих приложениях.
Для QA-инженеров и разработчиков, которым нужно проверять на прочность валидацию ввода, обработку кодировок и граничные случаи unicode в своих приложениях.Есть ли пакеты для других языков программирования?Да, существуют реализации, поддерживаемые сообществом, для менеджеров пакетов Node, .NET, PHP и C++. Ссылки на них приведены в README.
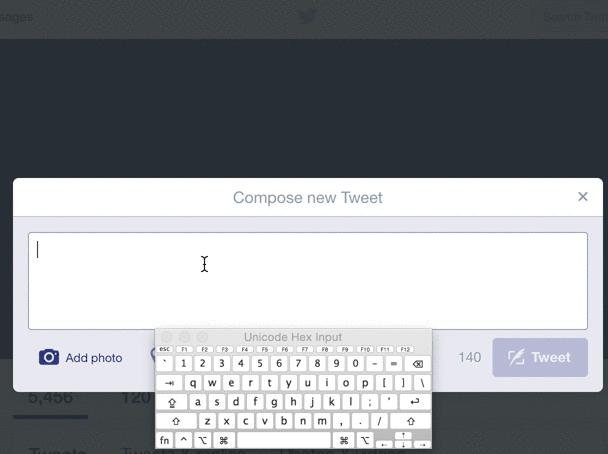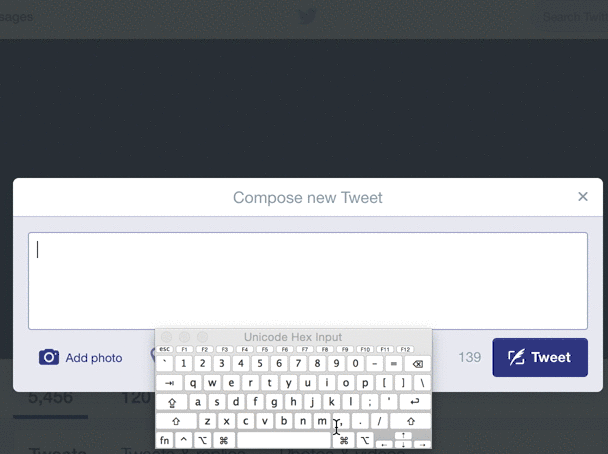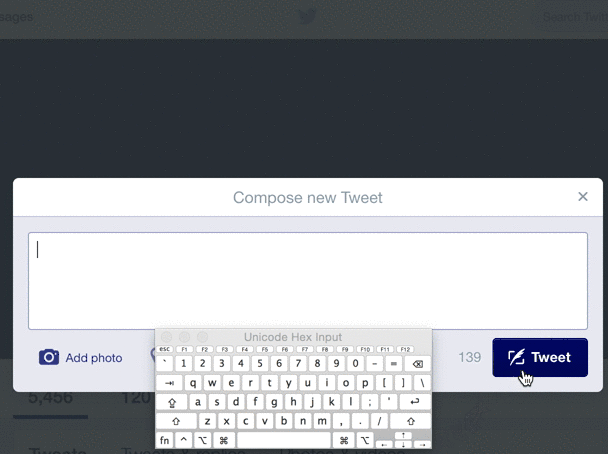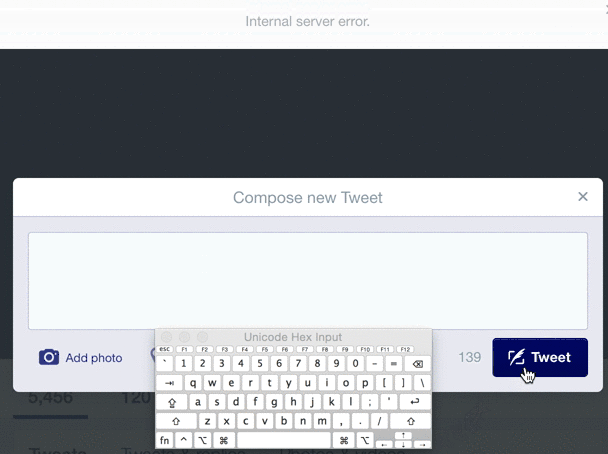
Да, существуют реализации, поддерживаемые сообществом, для менеджеров пакетов Node, .NET, PHP и C++. Ссылки на них приведены в README.Зачем на практике тестировать с помощью «коварных» строк?Даже крупные компании упускают граничные случаи. В README приведён пример: твит с пробелом нулевой ширины (U+200B) в Twitter вызвал внутреннюю ошибку сервера. Это показывает, как неожиданный ввод ломает реальные системы.
Даже крупные компании упускают граничные случаи. В README приведён пример: твит с пробелом нулевой ширины (U+200B) в Twitter вызвал внутреннюю ошибку сервера. Это показывает, как неожиданный ввод ломает реальные системы.Список всё ещё обновляется?Да, его описывают как развивающийся список, а сопровождающий Max Woolf принимает пул-реквесты с новыми строками или разделами.
Да, его описывают как развивающийся список, а сопровождающий Max Woolf принимает пул-реквесты с новыми строками или разделами.What are similar projects?awesome-security, awesome-web-security, SecLists, Resources-for-Beginner-Bug-Bounty-Hunters, faker, os-taxonomy, faker, CheatSheetSeries
awesome-security, awesome-web-security, SecLists, Resources-for-Beginner-Bug-Bounty-Hunters, faker, os-taxonomy, faker, CheatSheetSeriesWhich topics is it in?unicode, qa, fuzzing, web-security, validation, data, dataset, cybersecurity, json, reference, testing, list
unicode, qa, fuzzing, web-security, validation, data, dataset, cybersecurity, json, reference, testing, list