What is this?
 It is a curated collection of strings with a high probability of breaking software when used as user input, meant to help QA testing of input validation.
Is this a testing tool or just a plain data file?It is just data, not a tool: a human-readable blns.txt with comments and sections, plus a stripped-down blns.json array for programmatic use.
It is just data, not a tool: a human-readable blns.txt with comments and sections, plus a stripped-down blns.json array for programmatic use.How do I actually use these strings in my tests?Copy/paste strings from blns.txt into input forms for manual QA, or load blns.json into your automated test suite to feed as inputs.
Copy/paste strings from blns.txt into input forms for manual QA, or load blns.json into your automated test suite to feed as inputs.Are there any rules about what can be added to the list?Contributors are asked to avoid very-long strings (255+ characters), the EICAR antivirus test string, and null characters, since these break manual readability or corrupt the file on GitHub.
Contributors are asked to avoid very-long strings (255+ characters), the EICAR antivirus test string, and null characters, since these break manual readability or corrupt the file on GitHub.Who is this list meant for?QA engineers and developers who need to stress-test input validation, encoding handling, and unicode edge cases in their applications.
QA engineers and developers who need to stress-test input validation, encoding handling, and unicode edge cases in their applications.Are there packages for other programming languages?Yes, community-maintained implementations exist for Node, .NET, PHP, and C++ package managers, linked from the README.
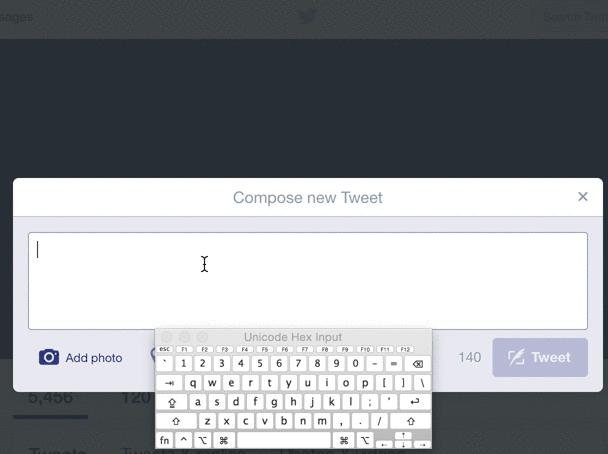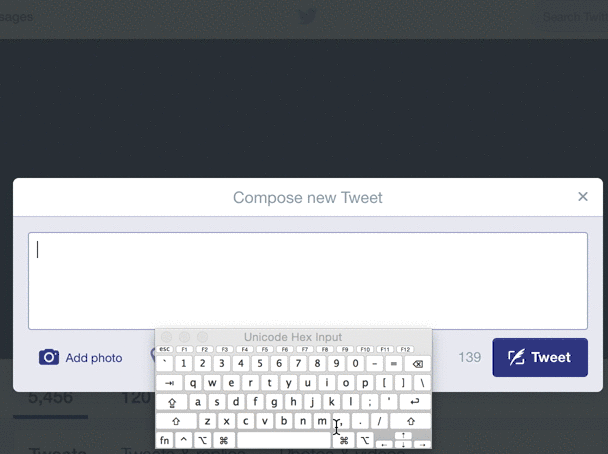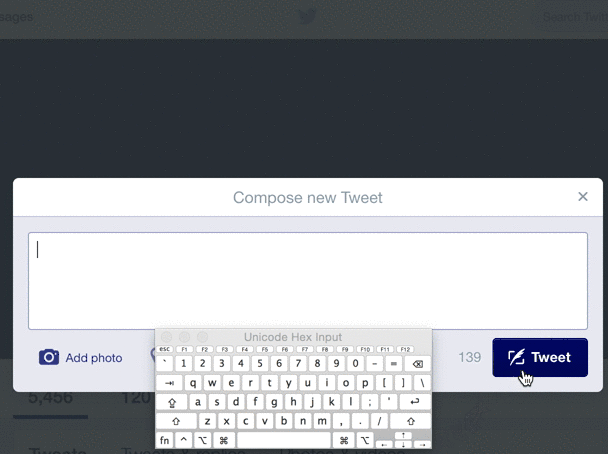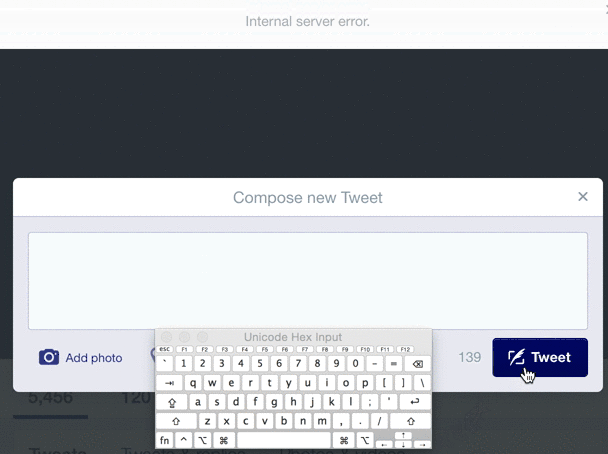
Yes, community-maintained implementations exist for Node, .NET, PHP, and C++ package managers, linked from the README.Why does testing with naughty strings matter in practice?Even large companies miss edge cases; the README cites tweeting a zero-width space (U+200B) on Twitter causing an internal server error, showing how unexpected input breaks real systems.
Even large companies miss edge cases; the README cites tweeting a zero-width space (U+200B) on Twitter causing an internal server error, showing how unexpected input breaks real systems.Is the list still being updated?Yes, it is described as an evolving list, and the maintainer (Max Woolf) accepts pull requests adding new strings or sections.
Yes, it is described as an evolving list, and the maintainer (Max Woolf) accepts pull requests adding new strings or sections.What are similar projects?awesome-security, awesome-web-security, SecLists, Resources-for-Beginner-Bug-Bounty-Hunters, faker, os-taxonomy, faker, CheatSheetSeries
awesome-security, awesome-web-security, SecLists, Resources-for-Beginner-Bug-Bounty-Hunters, faker, os-taxonomy, faker, CheatSheetSeriesWhich topics is it in?unicode, qa, fuzzing, web-security, validation, data, dataset, cybersecurity, json, reference, testing, list
unicode, qa, fuzzing, web-security, validation, data, dataset, cybersecurity, json, reference, testing, list