
trivy README

The project's README from github.com/aquasecurity/trivy. As one markdown file: README.md.

GitHub Release Test Go Report Card License: Apache-2.0 GitHub Downloads Docker Pulls

📖 Documentation

Trivy (pronunciation) is a comprehensive and versatile security scanner. Trivy has scanners that look for security issues, and targets where it can find those issues.

Targets (what Trivy can scan):

Scanners (what Trivy can find there):

Trivy supports most popular programming languages, operating systems, and platforms. For a complete list, see the Scanning Coverage page.

To learn more, go to the Trivy homepage for feature highlights, or to the Documentation site for detailed information.

Quick Start

Get Trivy

Trivy is available in most common distribution channels. The full list of installation options is available in the Installation page. Here are a few popular examples:

Trivy is integrated with many popular platforms and applications. The complete list of integrations is available in the Ecosystem page. Here are a few popular examples:

Canary builds

There are canary builds (Docker Hub, GitHub, ECR images and binaries) generated with every push to the main branch.

Please be aware: canary builds might have critical bugs, so they are not recommended for use in production.

General usage

trivy <target> [--scanners <scanner1,scanner2>] <subject>

Examples:

trivy image python:3.4-alpine
Result

https://github.com/user-attachments/assets/af1c11e7-d9c5-48af-8e05-cb34dfd6352a

trivy fs --scanners vuln,secret,misconfig myproject/
Result

https://github.com/user-attachments/assets/6b3894b7-77c5-4ffc-ac94-ffe6648a30dc

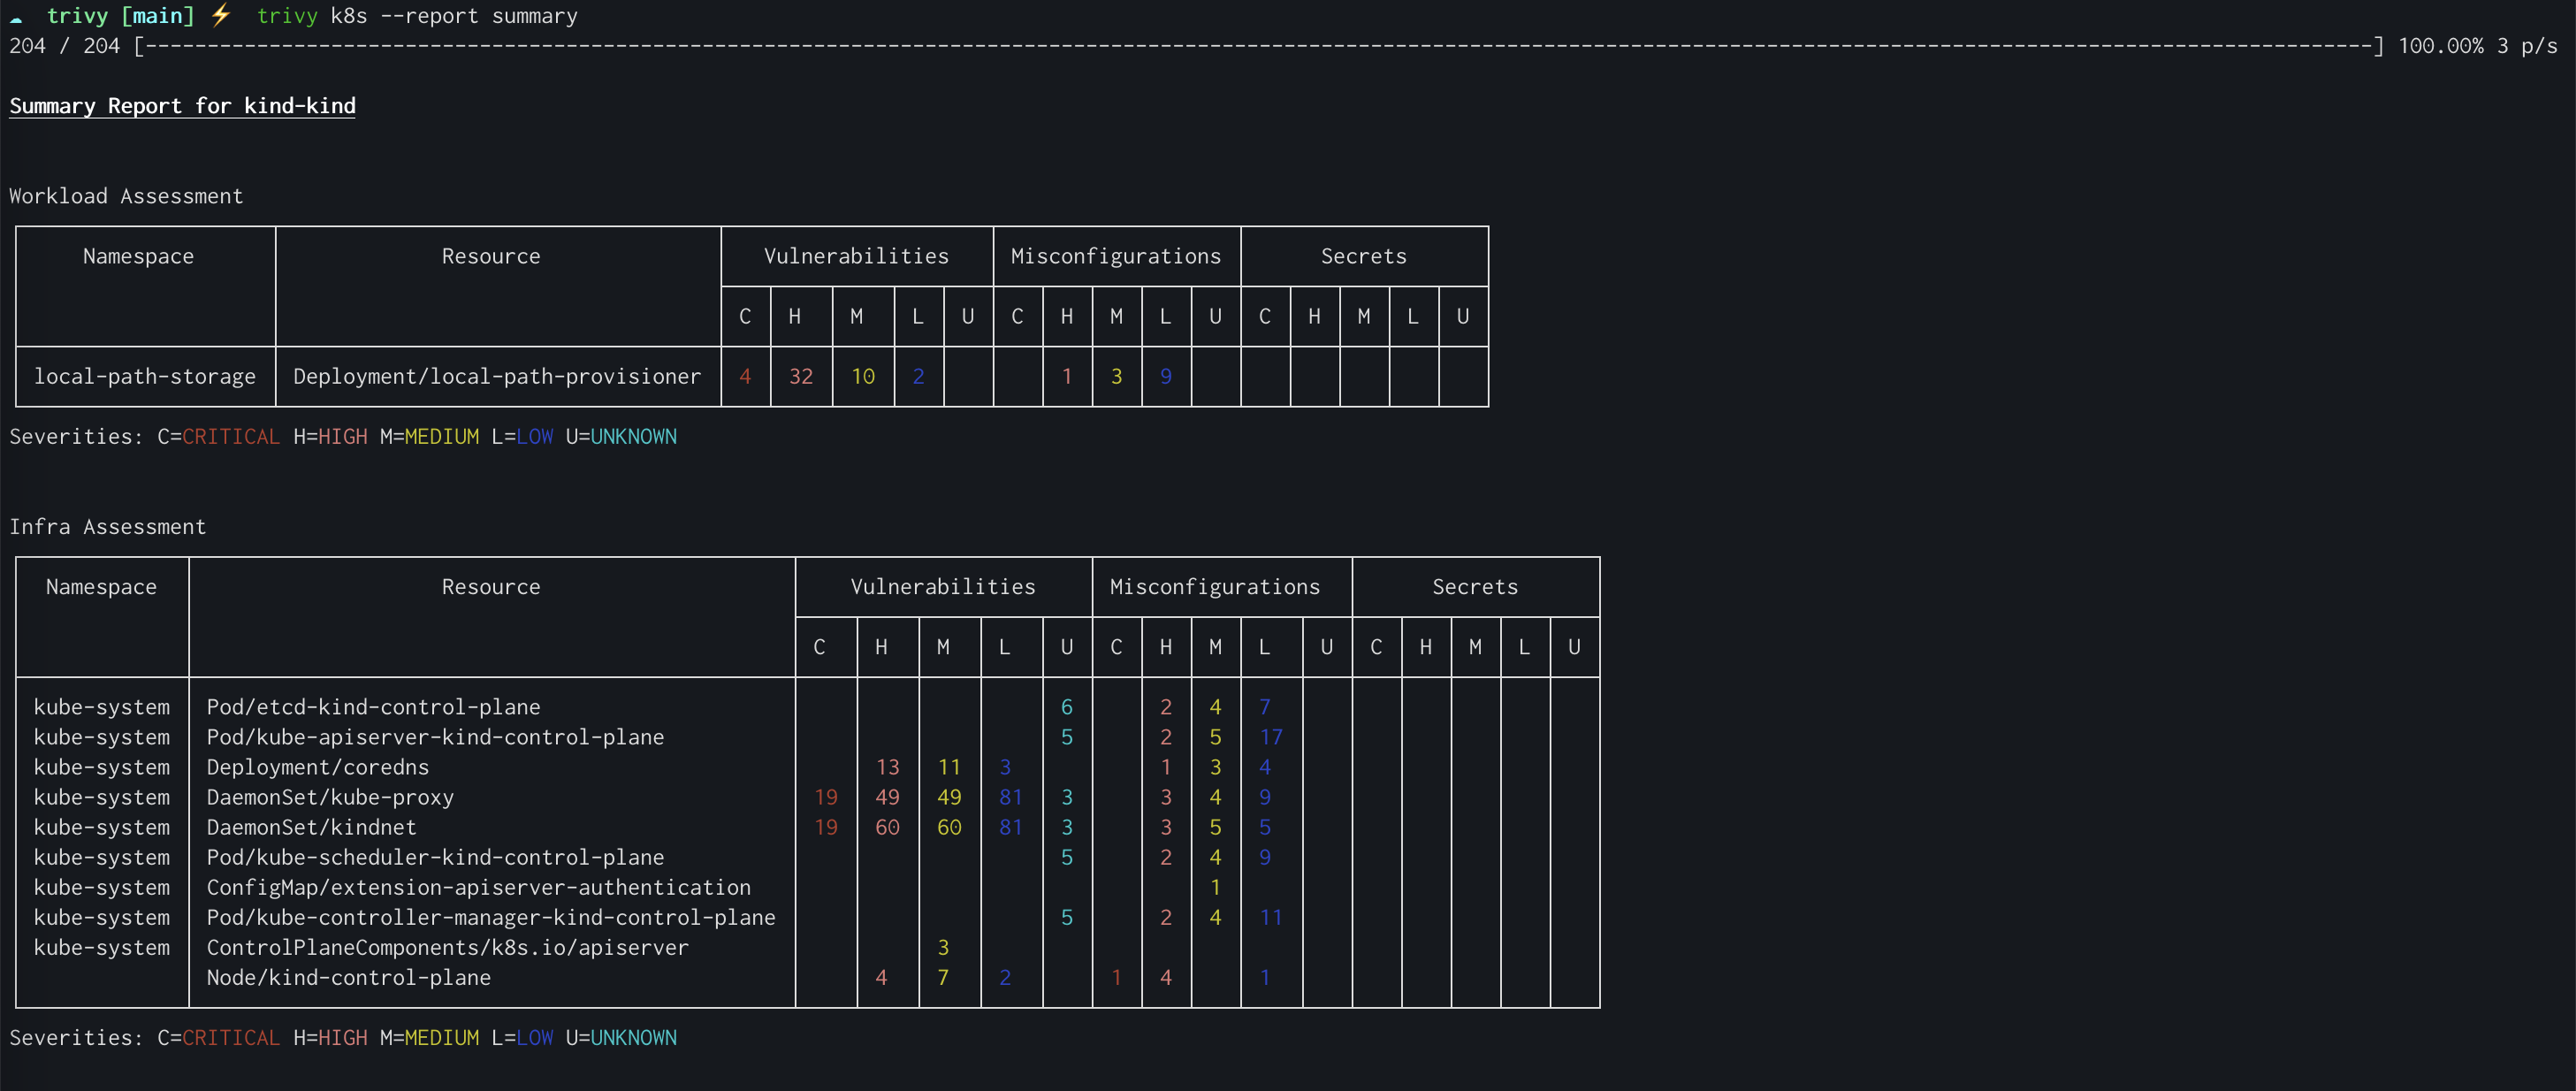
trivy k8s --report summary cluster
Result

k8s summary

FAQ

How to pronounce the name "Trivy"?

tri is pronounced like trigger, vy is pronounced like envy.

Want more? Check out Aqua

If you liked Trivy, you will love Aqua which builds on top of Trivy to provide even more enhanced capabilities for a complete security management offering.
You can find a high level comparison table specific to Trivy users here. In addition check out the https://aquasec.com website for more information about our products and services. If you'd like to contact Aqua or request a demo, please use this form: https://www.aquasec.com/demo

Community

Trivy is an Aqua Security open source project.
Learn about our open source work and portfolio here.
Contact us about any matter by opening a GitHub Discussion here

Please ensure to abide by our Code of Conduct during all interactions.

trivy (aquasecurity/trivy)

Searching Database…

38.5K ·GitHub
这是什么?Trivy 是一款一体化的安全扫描工具,可以检测容器镜像、文件系统、Git 仓库、虚拟机镜像和 Kubernetes 集群中的漏洞、配置错误、敏感信息(如密钥)以及软件许可证问题。
这是命令行工具,还是要在我的集群里运行的服务?它主要是一个命令行工具,可以作为二进制文件或 Docker 镜像安装;它也能生成 SBOM,并集成到 CI/CD 流水线中,而不是作为常驻服务运行。
怎么把它运行起来?可以用 Homebrew 执行 'brew install trivy' 安装,也可以直接用 'docker run aquasec/trivy' 运行,或者从发布页面下载预编译的二进制文件。
运行前需要先安装什么东西吗,比如 Docker?除了使用容器镜像时需要 Docker 之外,不需要其他特定的运行时依赖;否则二进制文件可以独立运行。
它是否支持所有编程语言和平台?Trivy 支持大多数主流编程语言、操作系统和平台,完整的兼容性列表单独放在 Scanning Coverage 页面中,而不在 README 里。
这个工具面向哪些人?它面向需要在代码或镜像发布前及时发现漏洞、不良配置和泄露密钥的开发者以及 DevSecOps 团队。
Trivy 具体能扫描哪些对象?它可以扫描容器镜像、文件系统、远程 Git 仓库、虚拟机镜像和 Kubernetes 集群。
Trivy 能检测哪些类型的问题?它能检测用于生成 SBOM 的操作系统和依赖软件包、已知 CVE 漏洞、IaC 配置错误、暴露的敏感信息,以及软件许可证问题。
基于 Trivy 有没有更高级的产品?有。Aqua 的商业平台基于 Trivy 构建,提供更完善、更全面的安全管理方案。
'Trivy' 怎么读?发音类似 trigger 中的 'tri' 加上 envy 中的 'vy'。
What are similar projects?gitleaks, grype, nuclei, vuls, slim, pulumi, trufflehog, kubescape
Size
923.2 MB
Stars
38.5K
Age
7y
Commits · 90 Days