





What is this?
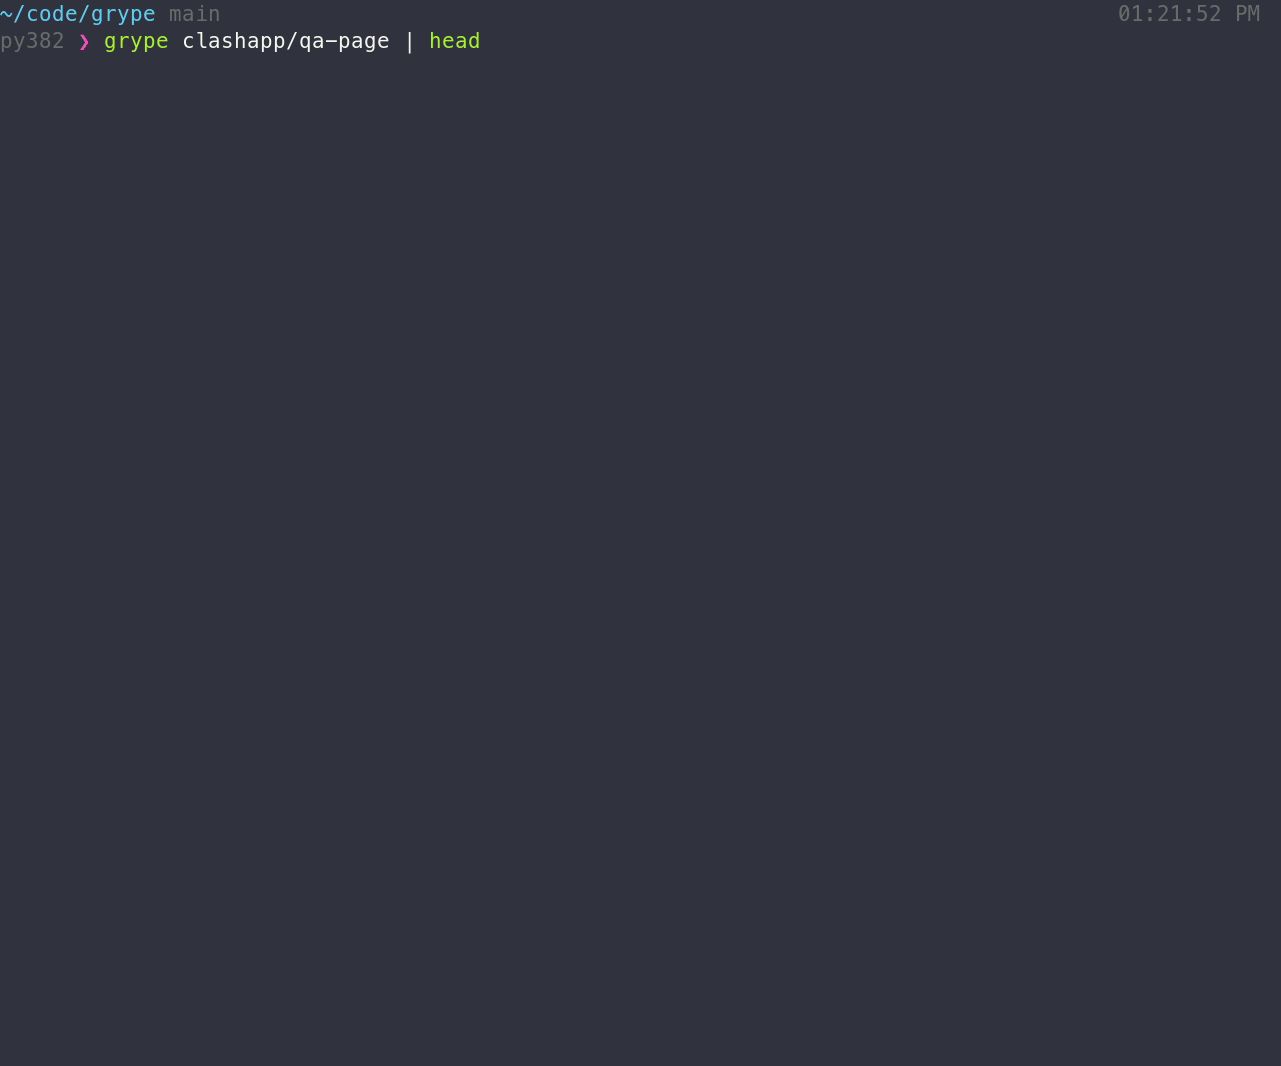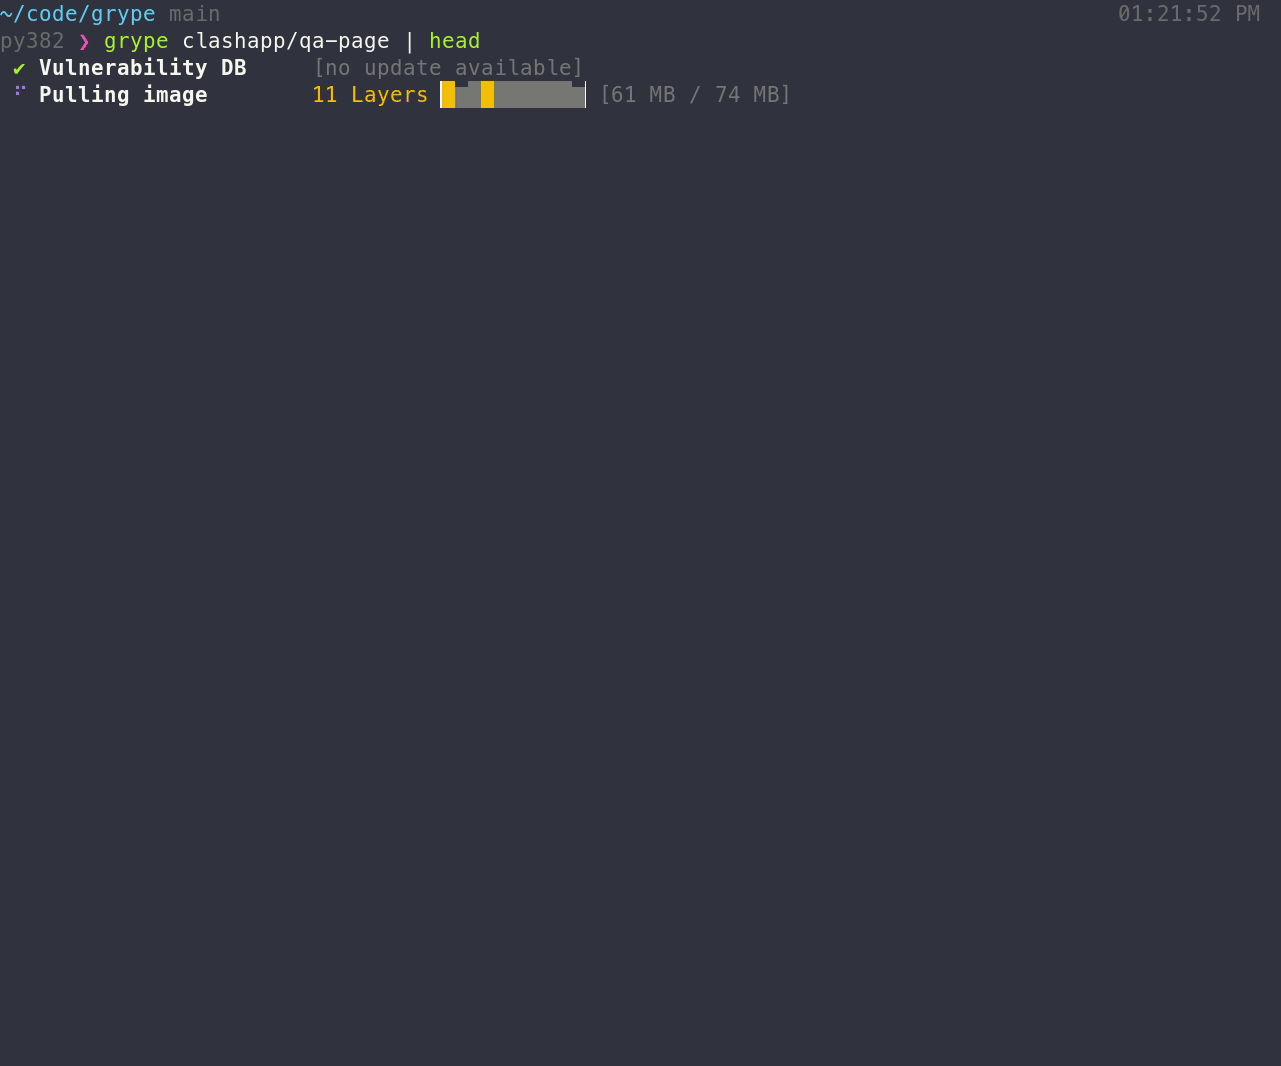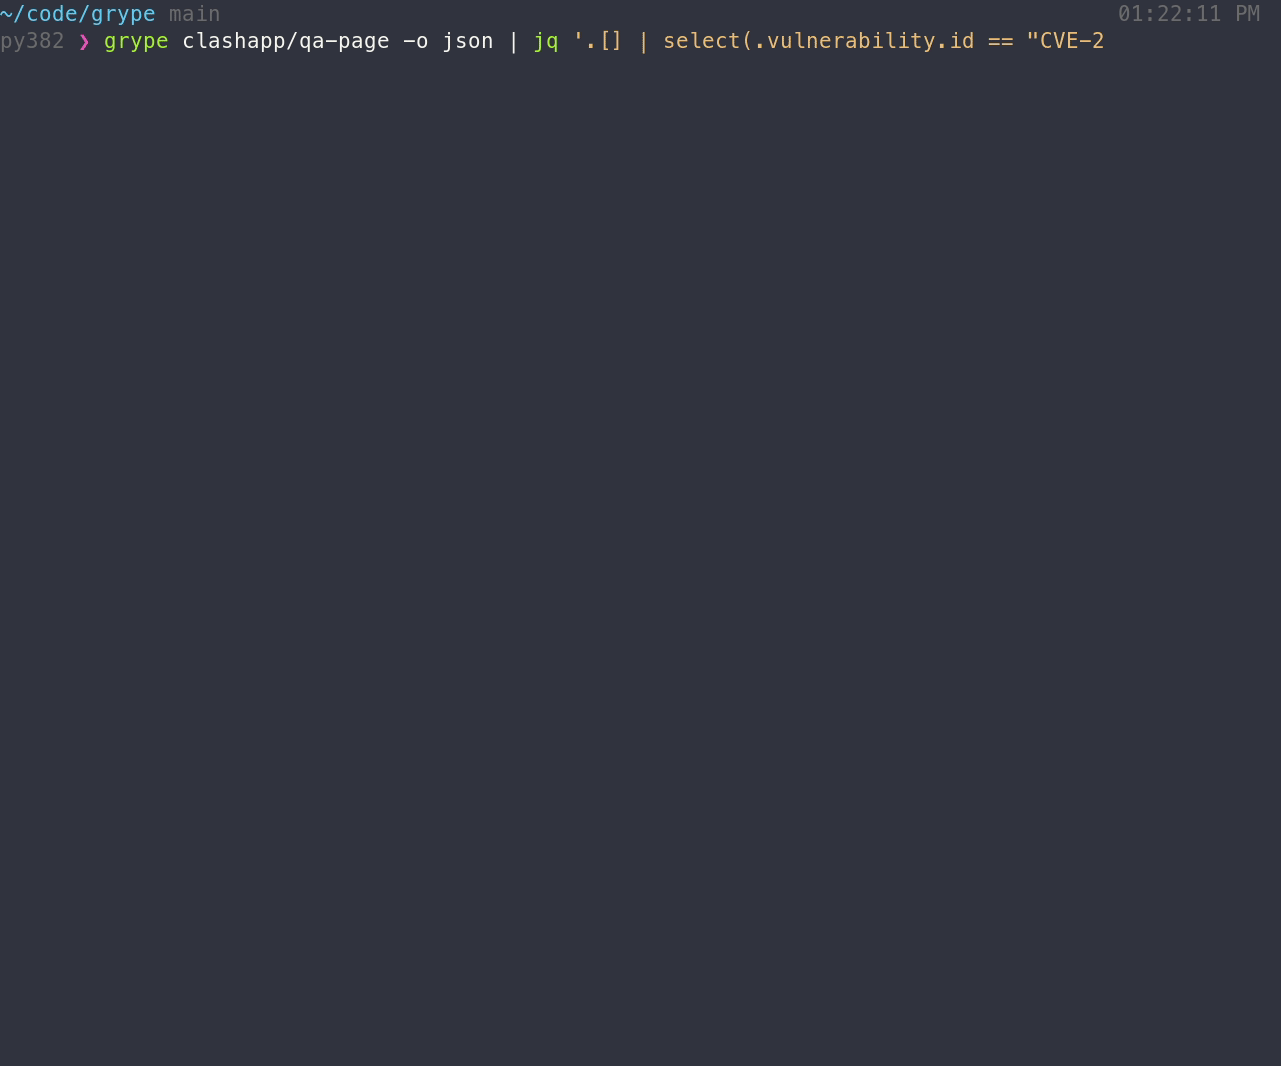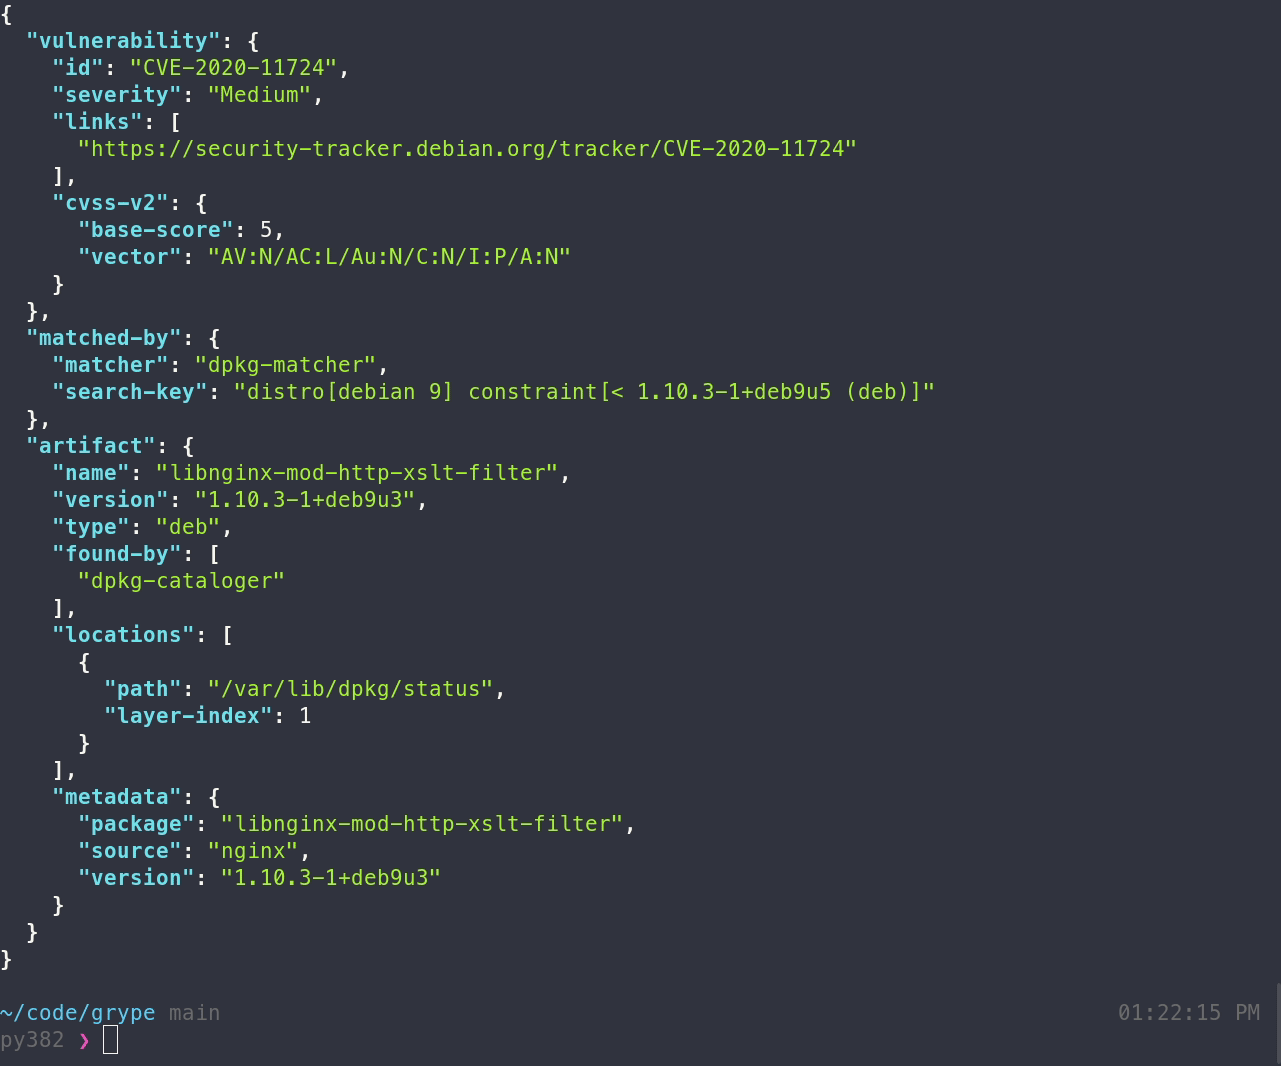
 Grype is a command-line vulnerability scanner that checks container images, filesystems, and SBOMs for known security vulnerabilities.
Is this a CLI tool or a library I'd import into my code?It is a standalone CLI tool written in Go that you run against an image, directory, or SBOM file — it's not a library you import.
It is a standalone CLI tool written in Go that you run against an image, directory, or SBOM file — it's not a library you import.How do I install Grype?You can run the one-line quick install script from the README, or install it through Homebrew, Docker, Chocolatey, or MacPorts as described in the Installation docs.
You can run the one-line quick install script from the README, or install it through Homebrew, Docker, Chocolatey, or MacPorts as described in the Installation docs.Do I need Syft or another SBOM tool before I can use it?No, Grype can scan container images and filesystems directly on its own, but feeding it a pre-generated SBOM makes the scan even faster.
No, Grype can scan container images and filesystems directly on its own, but feeding it a pre-generated SBOM makes the scan even faster.Which package ecosystems does it actually detect vulnerabilities in?It covers major OS distros like Alpine, Debian, Ubuntu, RHEL, Oracle Linux, and Amazon Linux, plus language ecosystems like Ruby, Java, JavaScript, Python, .NET, Go, PHP, and Rust — anything outside those isn't covered.
It covers major OS distros like Alpine, Debian, Ubuntu, RHEL, Oracle Linux, and Amazon Linux, plus language ecosystems like Ruby, Java, JavaScript, Python, .NET, Go, PHP, and Rust — anything outside those isn't covered.Does it run on Windows and macOS, or just Linux?It runs cross-platform: besides Linux, it can be installed via Chocolatey on Windows, MacPorts/Homebrew on macOS, or as a Docker container anywhere.
It runs cross-platform: besides Linux, it can be installed via Chocolatey on Windows, MacPorts/Homebrew on macOS, or as a Docker container anywhere.What container image formats can it scan?Grype supports Docker, OCI, and Singularity image formats, in addition to raw filesystems and SBOMs.
Grype supports Docker, OCI, and Singularity image formats, in addition to raw filesystems and SBOMs.How does it help me prioritize which vulnerabilities to fix first?It adds threat and risk prioritization signals using EPSS, KEV (known exploited vulnerabilities), and its own risk scoring, so you can focus on what matters most.
It adds threat and risk prioritization signals using EPSS, KEV (known exploited vulnerabilities), and its own risk scoring, so you can focus on what matters most.What is the OpenVEX support used for?OpenVEX documents let you filter and augment scan results, for example to mark vulnerabilities as not-affected so they stop showing up in reports.
OpenVEX documents let you filter and augment scan results, for example to mark vulnerabilities as not-affected so they stop showing up in reports.Is this related to Syft?Yes, Grype is a sister project from Anchore to Syft, the SBOM generator, and the two are designed to work together for faster scanning.
Yes, Grype is a sister project from Anchore to Syft, the SBOM generator, and the two are designed to work together for faster scanning.What are similar projects?clair, trivy, osv-scanner, slim, bashka, podman, SkillSpector, buildkit
clair, trivy, osv-scanner, slim, bashka, podman, SkillSpector, buildkitWhich topics is it in?vulnerabilities, oci, supply-chain-security, devsecops, vulnerability, containers, static-analysis, cybersecurity, golang, hacktoberfest, devops, go
vulnerabilities, oci, supply-chain-security, devsecops, vulnerability, containers, static-analysis, cybersecurity, golang, hacktoberfest, devops, go