




What is this?
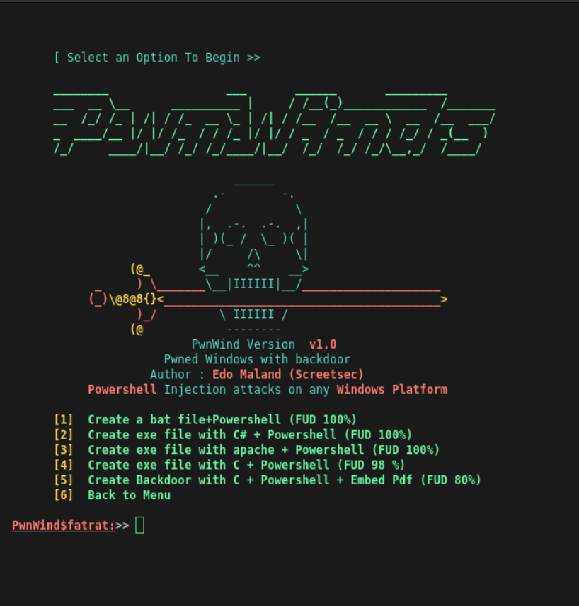
 TheFatRat is an exploiting tool that compiles malware from famous payloads — an easy way to generate backdoors built to slip past most anti-virus software.
What does it actually produce?Backdoor files — payloads in various formats matched to the target operating system — plus a local or remote listener to catch the incoming connection.
Backdoor files — payloads in various formats matched to the target operating system — plus a local or remote listener to catch the incoming connection.How do I get it running?Clone the repository and run setup.sh; if setup fails, run the bundled chktools script, which checks that everything is the right version and proposes a fix.
Clone the repository and run setup.sh; if setup fails, run the bundled chktools script, which checks that everything is the right version and proposes a fix.Do I need Metasploit for this?Yes — TheFatRat fully automates MSFvenom and Metasploit, so a working Metasploit setup, typically on Kali Linux, is the engine underneath.
Yes — TheFatRat fully automates MSFvenom and Metasploit, so a working Metasploit setup, typically on Kali Linux, is the engine underneath.Am I actually allowed to use this?Educational use only: attacking targets without prior mutual consent is illegal, and the developers assume no liability for any misuse or damage.
Educational use only: attacking targets without prior mutual consent is illegal, and the developers assume no liability for any misuse or damage.Where does the malware it builds actually run?The compiled malware can be executed on Linux, Windows, Mac and Android, and backdoors are generated per target-OS category.
The compiled malware can be executed on Linux, Windows, Mac and Android, and backdoors are generated per target-OS category.Can it hide payloads inside real files or apps?Yes — the project's demo videos cover embedding a trojan into a Debian package, injecting a payload into an original Android APK, and binding a payload with a JPG image.
Yes — the project's demo videos cover embedding a trojan into a Debian package, injecting a payload into an original Android APK, and binding a payload with a JPG image.What delivery helpers does it ship with?It automatically creates AutoRun files for USB/CDROM exploitation, detects your external IP and interface address, and includes a file pumper for increasing file size.
It automatically creates AutoRun files for USB/CDROM exploitation, detects your external IP and interface address, and includes a file pumper for increasing file size.What alternatives does the README mention?Veil Framework, Shellter, TrustedSec's Unicorn, MSFvenom Payload Creator (MSFPC), Venom and Phantom-Evasion are listed as comparable backdoor and AV-bypass generators.
Veil Framework, Shellter, TrustedSec's Unicorn, MSFvenom Payload Creator (MSFPC), Venom and Phantom-Evasion are listed as comparable backdoor and AV-bypass generators.What are similar projects?Claude-Red, nishang, Decepticon, Red-Teaming-Toolkit, mimikatz, PowerSploit, zphisher, Awesome-Hacking-Resources
Claude-Red, nishang, Decepticon, Red-Teaming-Toolkit, mimikatz, PowerSploit, zphisher, Awesome-Hacking-ResourcesWhich topics is it in?post-exploitation, kali-linux, remote, bypass, malware, trojan, remote-access, exploit, offensive-security, hacking-tool, pentesting, penetration-testing
post-exploitation, kali-linux, remote, bypass, malware, trojan, remote-access, exploit, offensive-security, hacking-tool, pentesting, penetration-testing