这是什么?
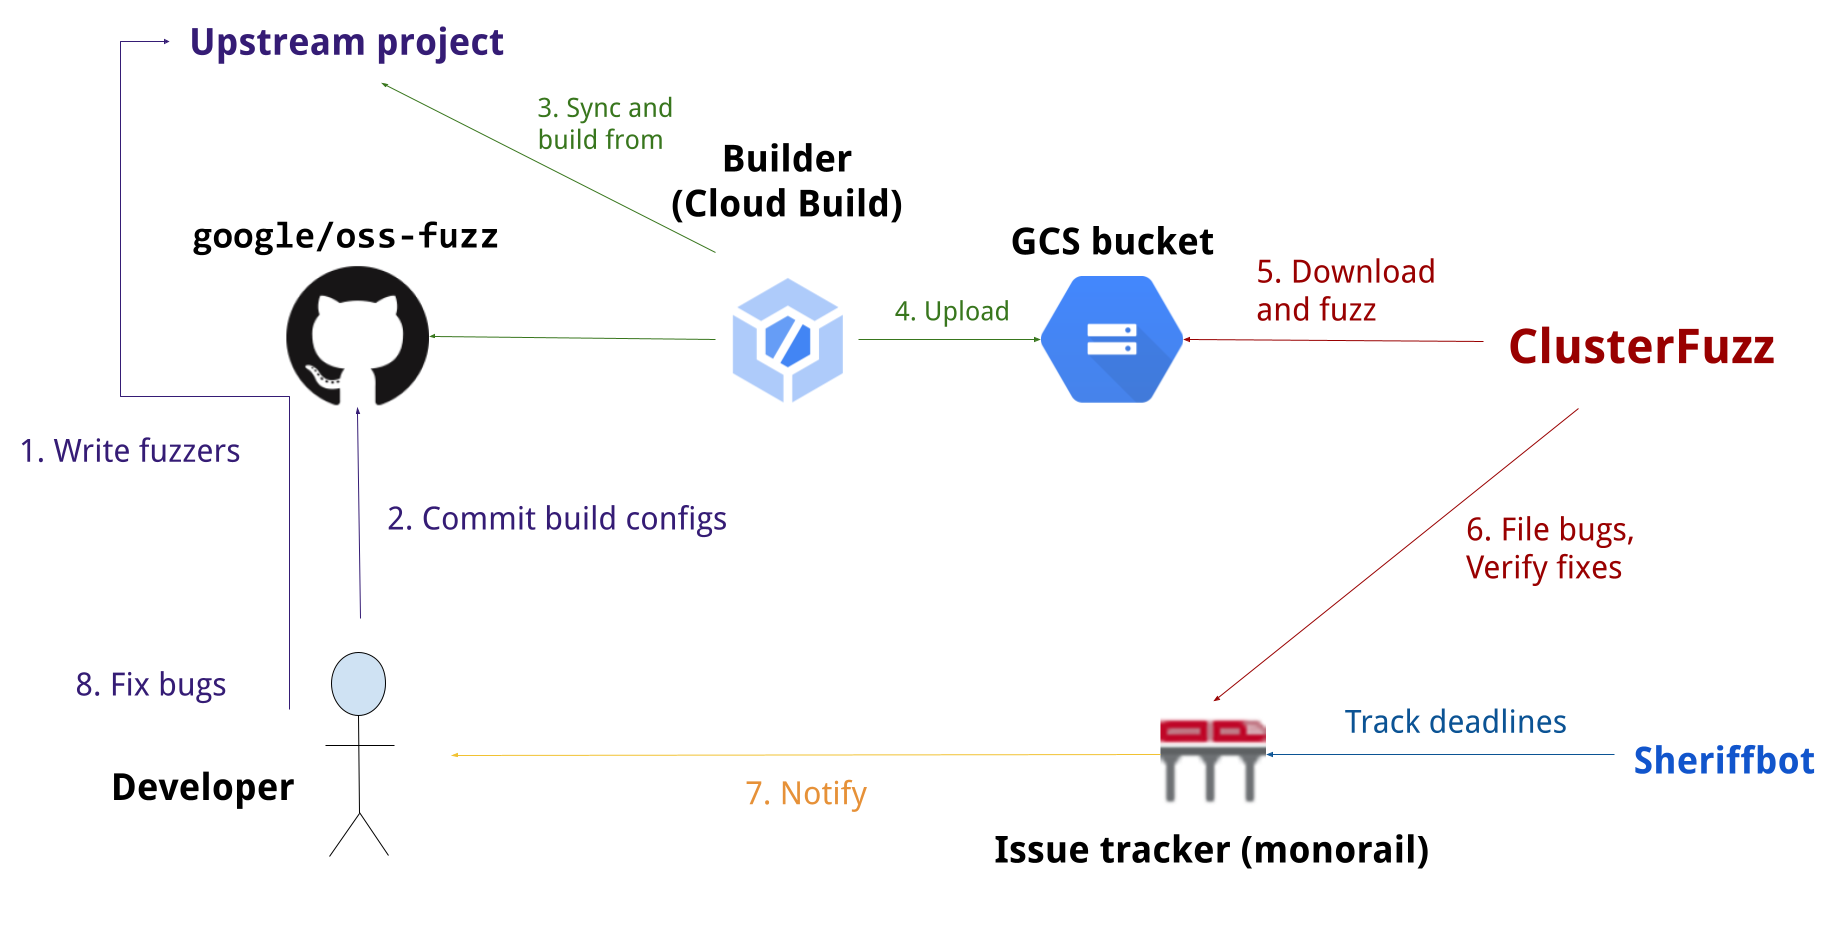
 OSS-Fuzz 是 Google 面向开源软件的免费持续模糊测试服务:它会不间断地运行引导式模糊测试,在攻击者之前发现安全漏洞和稳定性问题。
这是我下载的工具,还是 Google 运营的服务?这是 Google 为符合条件的开源项目运营的服务。不符合条件的项目(例如闭源项目)可以自己运行 ClusterFuzz 或 ClusterFuzzLite。
这是 Google 为符合条件的开源项目运营的服务。不符合条件的项目(例如闭源项目)可以自己运行 ClusterFuzz 或 ClusterFuzzLite。怎么把我的项目接入进去?按照详细文档操作就行,它会一步步教你把项目的构建接入 OSS-Fuzz,让它能对项目进行持续模糊测试。
按照详细文档操作就行,它会一步步教你把项目的构建接入 OSS-Fuzz,让它能对项目进行持续模糊测试。它能模糊测试的硬件或架构有限制吗?有——它只支持模糊测试 x86_64 和 i386 构建版本,其他架构不在覆盖范围内。
有——它只支持模糊测试 x86_64 和 i386 构建版本,其他架构不在覆盖范围内。它能模糊测试哪些编程语言?C/C++、Rust、Go、Python、Java/JVM、JavaScript 和 Lua 开箱即用,其他有 LLVM 支持的语言也可能可以用。
C/C++、Rust、Go、Python、Java/JVM、JavaScript 和 Lua 开箱即用,其他有 LLVM 支持的语言也可能可以用。它底层用的是哪些模糊测试引擎?libFuzzer、AFL++ 和 Honggfuzz,配合 Sanitizers,再加上 ClusterFuzz——一个分布式的模糊测试执行环境和报告工具。
libFuzzer、AFL++ 和 Honggfuzz,配合 Sanitizers,再加上 ClusterFuzz——一个分布式的模糊测试执行环境和报告工具。它真的发现过实际的漏洞吗?有——截至 2025 年 5 月,它已帮助在 1,000 个项目中识别并修复了超过 13,000 个漏洞和 50,000 个缺陷,其中包括通过 Jazzer Java 模糊测试器发现 Log4Shell。
有——截至 2025 年 5 月,它已帮助在 1,000 个项目中识别并修复了超过 13,000 个漏洞和 50,000 个缺陷,其中包括通过 Jazzer Java 模糊测试器发现 Log4Shell。它现在还在活跃开发吗?是的——它于 2016 年上线,项目博客一直更新到 2024 年底,最近还发了关于用 AI 挖掘更多漏洞的文章。
是的——它于 2016 年上线,项目博客一直更新到 2024 年底,最近还发了关于用 AI 挖掘更多漏洞的文章。What are similar projects?nuclei, vuls, strix, codex-guard, super-linter, wazuh, kani, sonarqube
nuclei, vuls, strix, codex-guard, super-linter, wazuh, kani, sonarqubeWhich topics is it in?vulnerabilities, vulnerability-detection, fuzzing, code-quality, ci, security-tools, shell, testing, cloud, security, automation, docker
vulnerabilities, vulnerability-detection, fuzzing, code-quality, ci, security-tools, shell, testing, cloud, security, automation, docker