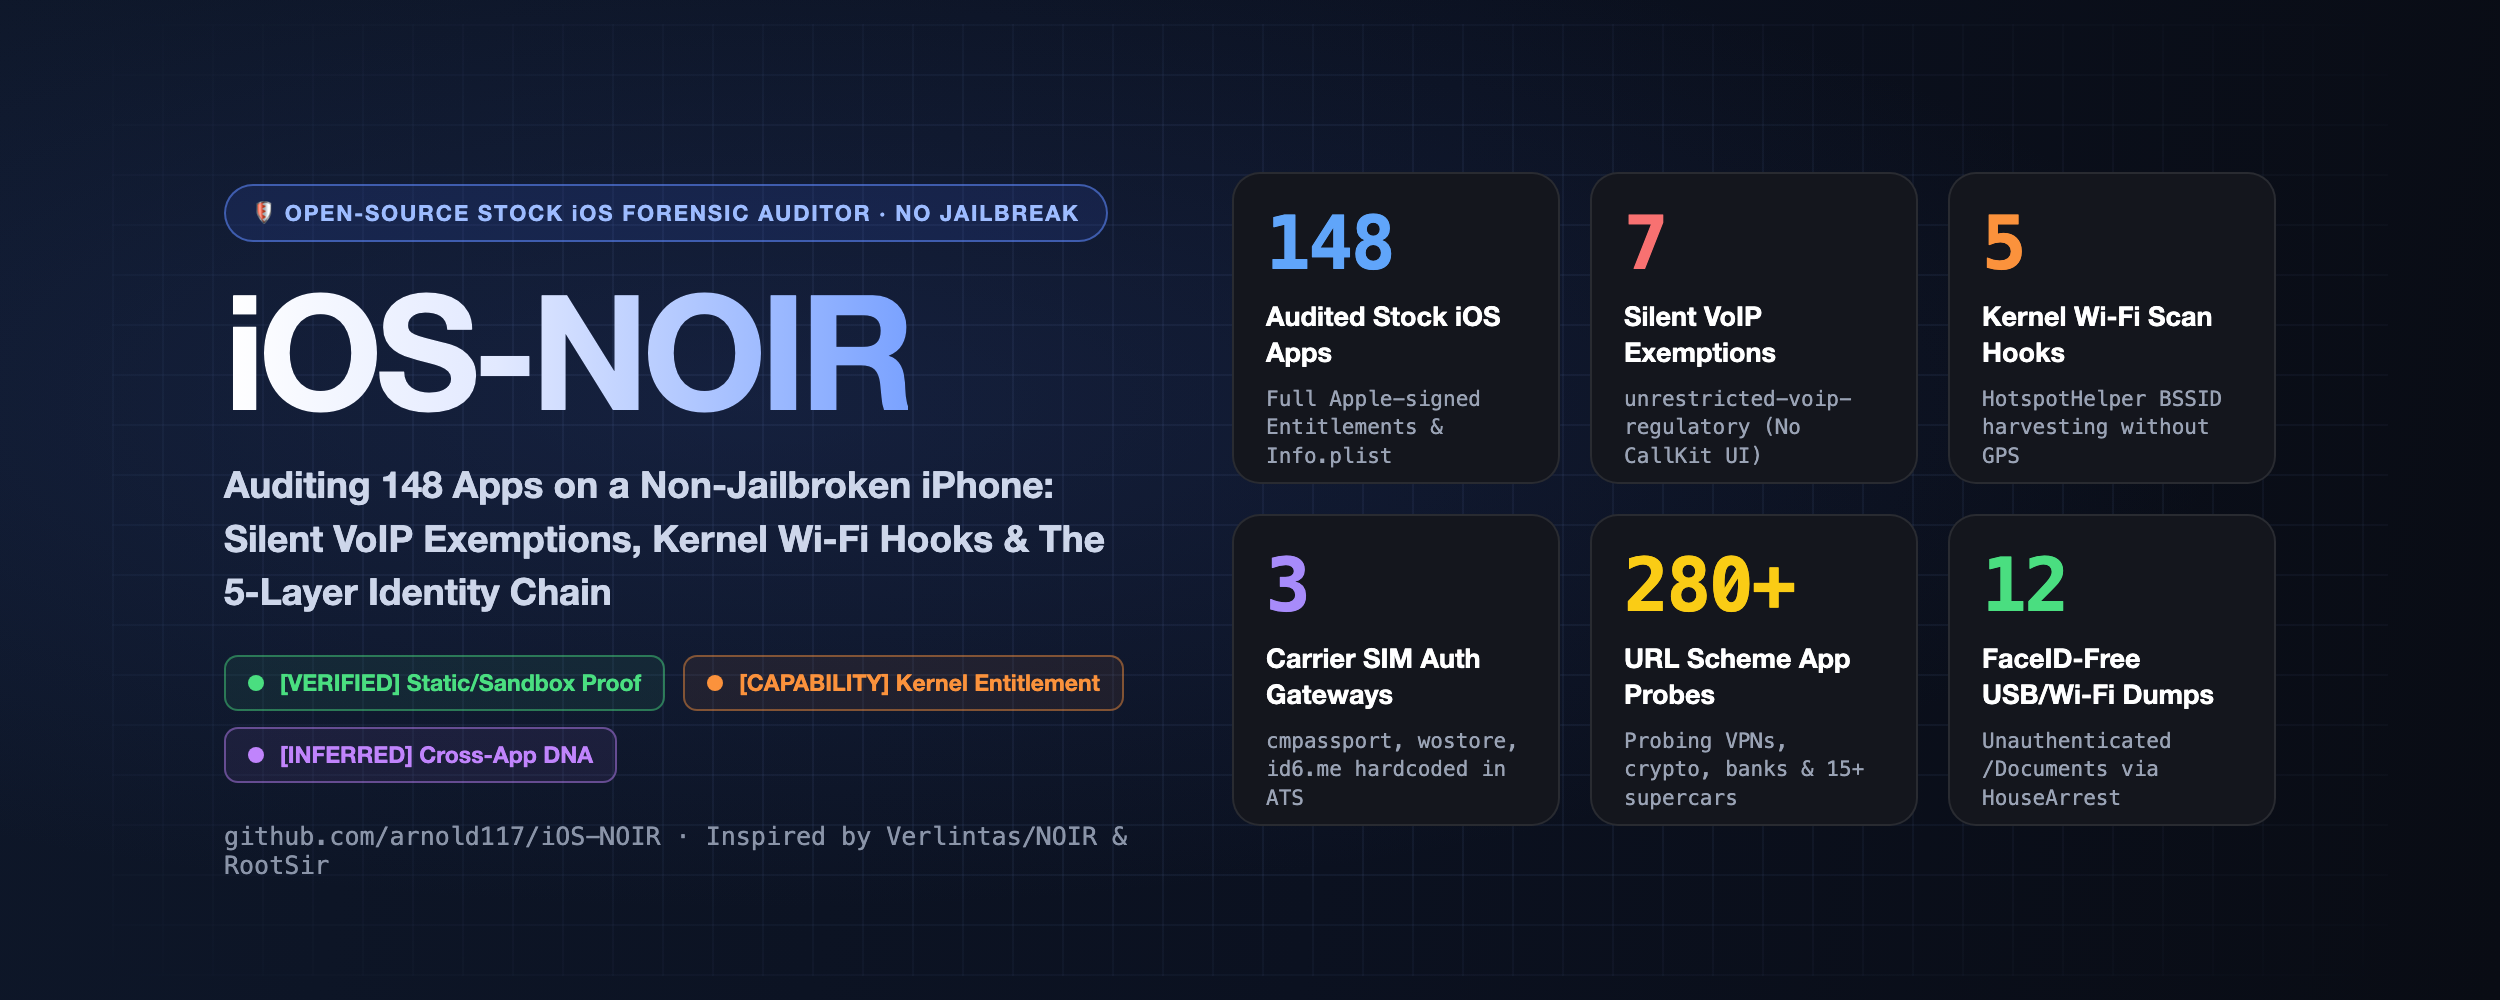

What is this?
 A no-jailbreak forensic auditor for iPhone. It reads entitlements, Info.plist, sandbox and syslog data over USB and writes a report on what apps may be leaking, with each finding graded by evidence strength.
Is it an app I install on my phone, or something else?Neither exactly. It's a Python command-line tool that runs on your computer and talks to the iPhone over USB, so no jailbreak is needed.
Neither exactly. It's a Python command-line tool that runs on your computer and talks to the iPhone over USB, so no jailbreak is needed.How do I get it running?Install the dependencies from the Quick Start section, plug in your unlocked iPhone, tap 'Trust This Computer' on the phone, then run the full audit to get a terminal summary and a standalone HTML report.
Install the dependencies from the Quick Start section, plug in your unlocked iPhone, tap 'Trust This Computer' on the phone, then run the full audit to get a terminal summary and a standalone HTML report.What do I need besides the iPhone?A Mac with Python and a USB cable. The tool is built on pymobiledevice3 for device access and rich for terminal output.
A Mac with Python and a USB cable. The tool is built on pymobiledevice3 for device access and rich for terminal output.Does it decrypt app code to show what the apps do?No. Store apps are FairPlay-encrypted, so it audits entitlements, plists, sandbox and syslog without decompiling code. For function-level analysis, the README suggests pairing it with RootSir's claude-ios-privacy-analysis.
No. Store apps are FairPlay-encrypted, so it audits entitlements, plists, sandbox and syslog without decompiling code. For function-level analysis, the README suggests pairing it with RootSir's claude-ios-privacy-analysis.Does it work on Windows or Linux too?Not verified yet. Only macOS has been tested, where Apple's usbmuxd runs natively. Windows and Linux may need extra iTunes or usbmuxd driver setup.
Not verified yet. Only macOS has been tested, where Apple's usbmuxd runs natively. Windows and Linux may need extra iTunes or usbmuxd driver setup.What is the 5-layer persistent identity chain?The README lays out five layers that can keep tracking you across reinstalls and VPN use on stock iOS. They include iCloud key-value store, shared Keychain, App Group containers, carrier phone-number gateways and Wi-Fi BSSID hooks.
The README lays out five layers that can keep tracking you across reinstalls and VPN use on stock iOS. They include iCloud key-value store, shared Keychain, App Group containers, carrier phone-number gateways and Wi-Fi BSSID hooks.What can it learn from iOS crash logs?It parses kernel .ips logs to find apps that exceeded their 24-hour disk-write limit, ranked by how far over they went. It also flags CPU-related kills and embedded binary SDKs, all without jailbreaking.
It parses kernel .ips logs to find apps that exceeded their 24-hour disk-write limit, ranked by how far over they went. It also flags CPU-related kills and embedded binary SDKs, all without jailbreaking.Does it spot apps probing for my VPN or crypto wallets?Yes. It finds apps hardcoding up to 280+ URL schemes in LSApplicationQueriesSchemes to check whether VPN clients, crypto wallets or car apps are installed.
Yes. It finds apps hardcoding up to 280+ URL schemes in LSApplicationQueriesSchemes to check whether VPN clients, crypto wallets or car apps are installed.Does it come with a way to block trackers?Yes. The shields folder has a .mobileconfig that sets encrypted DNS at the OS level, plus a Shadowrocket/Surge overlay module that blocks carrier silent-auth gateways, DNA fingerprinting and ad-tech domains.
Yes. The shields folder has a .mobileconfig that sets encrypted DNS at the OS level, plus a Shadowrocket/Surge overlay module that blocks carrier silent-auth gateways, DNA fingerprinting and ad-tech domains.What are similar projects?NOIR, Zero-Breach-Toolkit, hackingtool, mvt, OhMyKeymint, FilzaSlop, awesome-malware-analysis, qufz
NOIR, Zero-Breach-Toolkit, hackingtool, mvt, OhMyKeymint, FilzaSlop, awesome-malware-analysis, qufzWhich topics is it in?audit, mobile-security, iphone, telemetry, forensics, osint, privacy-tools, static-analysis, sandbox, cybersecurity, security-tools, ios
audit, mobile-security, iphone, telemetry, forensics, osint, privacy-tools, static-analysis, sandbox, cybersecurity, security-tools, ios