


opennhp README

The project's README from github.com/OpenNHP/opennhp. As one markdown file: README.md.

en zh-cn zh-tw de ja fr es id

OpenNHP Logo

OpenNHP: Open Source Zero Trust Security Toolkit

Build Release License codecov Ask DeepWiki

OpenNHP is a lightweight, cryptography-powered, open-source toolkit implementing Zero Trust security for infrastructure, applications, and data. It is the reference implementation of the Cloud Security Alliance (CSA) Network-infrastructure Hiding Protocol (NHP) specification, and features two core protocols:

Website · Vision · Live Demo · Documentation · Discord


Why OpenNHP

The modern internet is a dark forest. Attackers — increasingly backed by LLMs that scan, fingerprint, and exploit at machine speed via Autonomous Vulnerability Exploitation — treat every reachable service as a target. Gartner projects AI-driven cyberattacks will rise rapidly. Traditional defenses authenticate users after the network lets them in, leaving exposed ports, IPs, and domains as a permanent attack surface.

In the AI era, VISIBILITY = VULNERABILITY.

OpenNHP inverts that model: invisible until trusted. Every port, IP, and hostname sits behind a default-deny gate. Access is granted only after a cryptographically signed knock is authenticated and authorized out-of-band. Attackers can't exploit what they can't discover.

The third-generation network hiding protocol

NHP is the next step in a line of "hide the service first" designs:

Generation Protocol Limitations
1 Port Knocking Plaintext, replay-prone
2 Single Packet Authorization (SPA) Shared secrets, one-way, typically hides ports only, typically C/C++
3 NHP Modern crypto, bi-directional with status, hides domain + IP + ports, stateless and horizontally scalable, memory-safe Go

NHP slots in alongside existing IAM, DNS, FIDO, and Zero Trust policy engines rather than replacing them — it extends your stack instead of forking it.


Architecture

OpenNHP follows a modular design with three core components, inspired by the NIST Zero Trust Architecture:

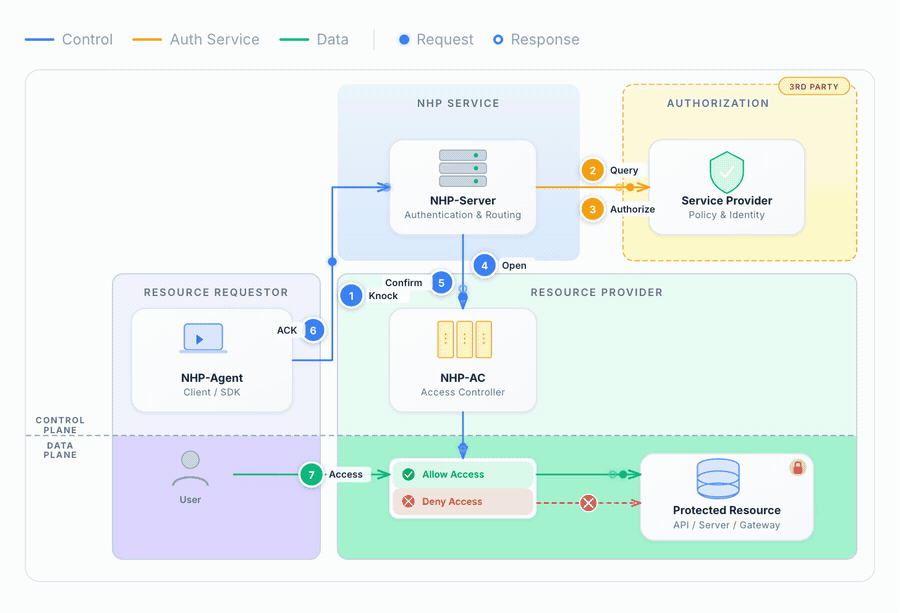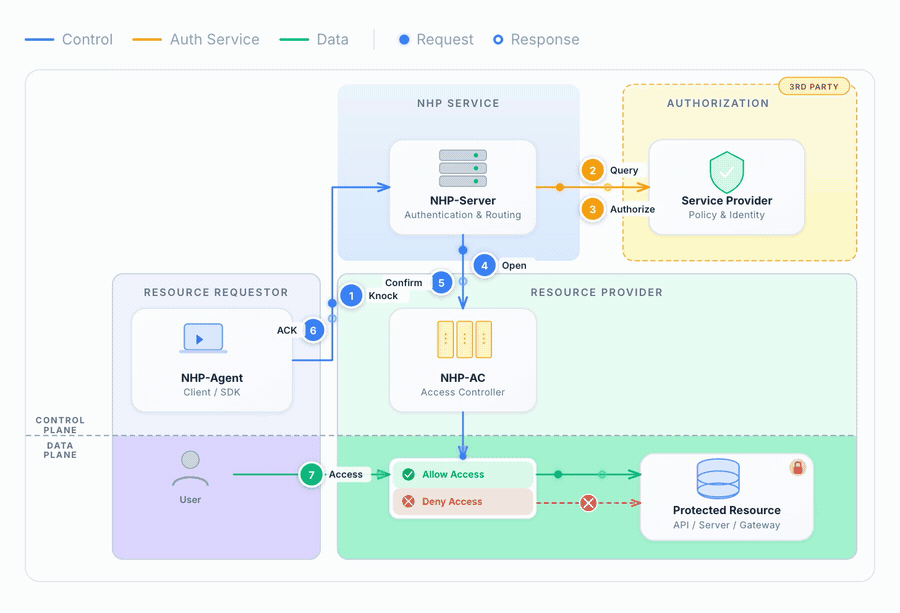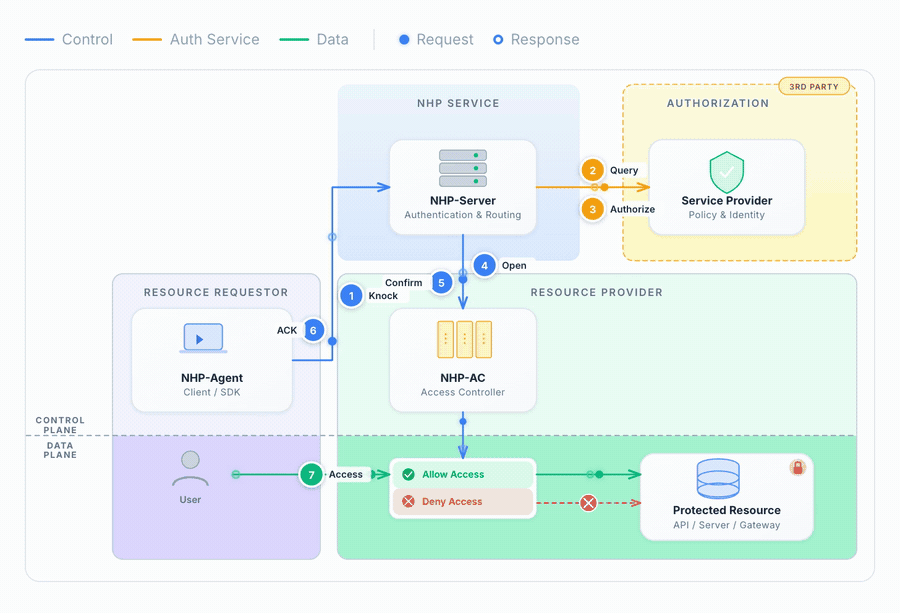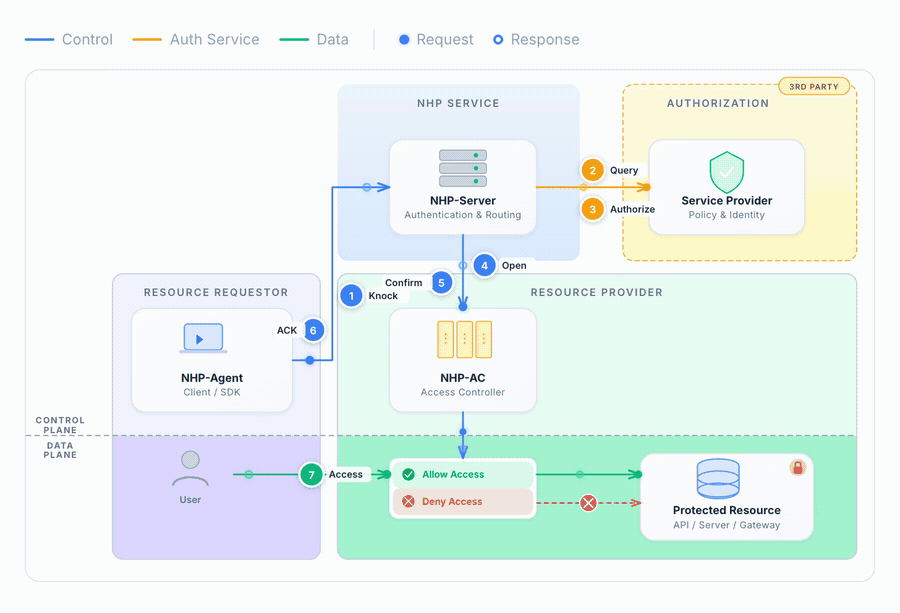
OpenNHP architecture

Core Component Role
NHP-Agent Client that sends encrypted knock requests to gain access
NHP-Server Authenticates and authorizes requests; runs separately and is architecturally decoupled from the protected host
NHP-AC Access controller that manages firewall rules on the protected server
Addon Component Role
NHP-Relay HTTP-to-UDP bridge enabling browser-based agents to send NHP knocks via HTTPS
NHP-KGC Key Generation Center for Identity-Based Cryptography (IBC)

Protocol flow

  1. Agent sends an encrypted knock (NHP_KNK) to the Server.
  2. Server validates the knock and sends an operation request (NHP_AOP) to the AC.
  3. AC opens the firewall and replies (NHP_ART) to the Server.
  4. Server returns an acknowledgment (NHP_ACK) with access info to the Agent.
  5. Agent reaches the protected resource through the AC.

Cryptography

OpenNHP ships with two interchangeable cipher suites:

Both are driven by the Noise Protocol Framework. An Identity-Based Cryptography (IBC) mode is available via the Key Generation Center (KGC).

For protocol details, deployment models, and cryptographic design, see the documentation.


Repository Structure

opennhp/
├── nhp/              # Core protocol library (Go module)
│   ├── core/         # Packet handling, cryptography, Noise Protocol, device management
│   ├── common/       # Shared types and message definitions
│   ├── utils/        # Utility functions
│   ├── plugins/      # Plugin handler interfaces
│   ├── log/          # Logging infrastructure
│   └── etcd/         # Distributed configuration support
└── endpoints/        # Daemon implementations (Go module, depends on nhp)
    ├── agent/        # NHP-Agent daemon
    ├── server/       # NHP-Server daemon
    ├── ac/           # NHP-AC (access controller) daemon
    ├── db/           # NHP-DB (Data Broker for DHP)
    ├── kgc/          # NHP-KGC (Key Generation Center)
    └── relay/        # NHP-Relay daemon

Quick Start

Prerequisites

Build

# Build all components
make

# Build individual daemons
make agentd    # NHP-Agent
make serverd   # NHP-Server
make acd       # NHP-AC
make db        # NHP-DB
make relayd    # NHP-Relay
make kgc       # NHP-KGC

Test

cd nhp && go test ./...
cd endpoints && go test ./...

Run with Docker

cd docker && docker-compose up --build

Follow the Quick Start tutorial to simulate the full authentication workflow in a Docker environment.


Contributing

We welcome contributions! Please read CONTRIBUTING.md before submitting pull requests.

Note: All commits must be signed with a verified GPG or SSH key.

git commit -S -m "your message"

Security

Found a vulnerability? Please follow the responsible-disclosure process in SECURITY.md rather than opening a public issue.


Sponsors

LayerV.ai logo    Atlas Cloud logo    Tencent Cloud logo

License

Released under the Apache 2.0 License.

Contact

opennhp (OpenNHP/opennhp)

Searching Database…

13.9K ·GitHub
这是什么?OpenNHP 是一个轻量级的开源零信任工具包,基于密码学技术:它会隐藏服务器的端口、IP 地址和域名,只有在客户端通过密码学授权之后,你的基础设施才会显现出来。
这是一个单独的程序,还是需要一起部署的多个组件?它是一套相互协作的组件,而不是单个应用:NHP-Agent(客户端)、NHP-Server(验证敲门请求,与受保护的主机分离部署)和 NHP-AC(管理受保护服务器上的防火墙规则)。
我怎么把它跑起来?构建需要 Go 1.26+ 和 make,运行演示还需要 Docker 和 Docker Compose。Quick Start 教程会在 Docker 环境里模拟完整的认证流程。
客户端连接需要装专门的软件吗——普通的浏览器能用吗?客户端必须支持 NHP 敲门协议;普通浏览器没法直接发送 UDP 敲门请求。针对基于浏览器的场景,提供了 NHP-Relay,它是一个 HTTP 到 UDP 的桥接器,可以通过 HTTPS 发送敲门请求。
它到底能跑在什么地方?它以 Go 编译的组件形式部署在你自己的服务器上(通常是 Linux),Quick Start 会用 Docker Compose 把整套服务跑起来。
除了保护网络,它在数据本身的保护上有没有做什么?有——这是第二个协议:DHP 利用加密和机密计算技术,让数据即使在处理过程中也保持“可用不可见”。
NHP 和 DHP 有什么区别?NHP 工作在网络层:端口、IP 地址和域名保持隐藏,直到经过授权的敲门请求将其打开。DHP 工作在数据层:加密和机密计算让数据即使在被处理的地方也保持“可用不可见”。
NHP 和老旧的端口敲门方式有什么不同?它被定位为第三代技术。端口敲门发送的是明文序列,容易被重放攻击;单包授权(Single Packet Authorization)引入了加密,但依赖共享密钥、只能单向通信,而且通常只能隐藏端口。NHP 采用了现代的 Noise 框架加密,支持双向状态确认,在隐藏 IP 和端口的同时还能隐藏域名,并且是无状态设计,可以横向扩展——全部用内存安全的 Go 编写。
现在都有 AI 驱动的扫描器了,为什么还要隐藏服务器?因为用作者的话说,在 AI 时代,可见就等于可被攻击:由大模型驱动的攻击者能以机器的速度对暴露的服务进行指纹识别和利用。OpenNHP 的应对思路是默认拒绝——攻击者发现不了的东西就无法利用。
NHP-KGC 是干什么的?它是标识密码体系(Identity-Based Cryptography)的密钥生成中心——这是一种可选模式,密钥与身份绑定,由 KGC 签发,而不是在每个 agent 和服务器之间预先分发证书。
What are similar projects?flowsint, pangolin, cloudflared, scuttle, trufflehog, netbird, nebula, gun
Creator
OpenNHP
Size
100.8 MB
Stars
13.9K
Age
12y
Commits · 90 Days