
voidaccess README

项目的 README,来自 github.com/KatrielMoses/voidaccess。合并为一个 markdown 文件:README.md。

VoidAccess: dark-web threat intel in your browser

Hosted at voidaccess.pro PyPI version Downloads GitHub stars License: MIT

Ask one question. Get a sourced report, a graph you can search, and IOCs you can load.
For security researchers, threat-intel teams, MSSPs and authorized investigators.

Use it hosted → voidaccess.pro  ·  Run it yourself → pip install voidaccess

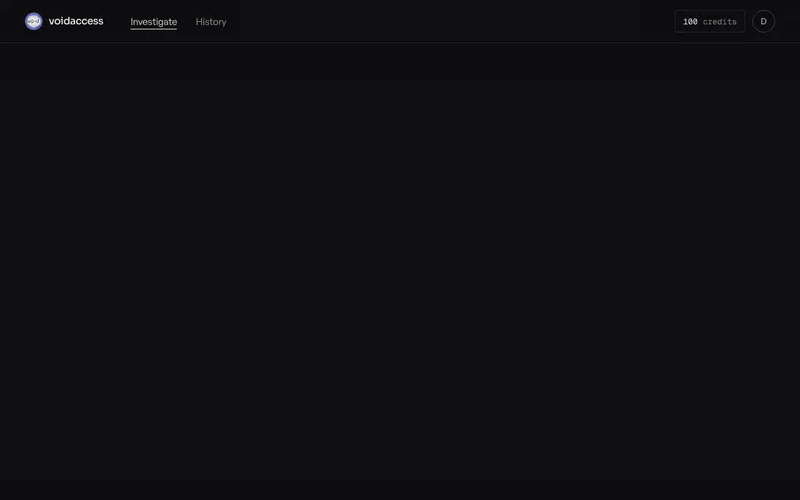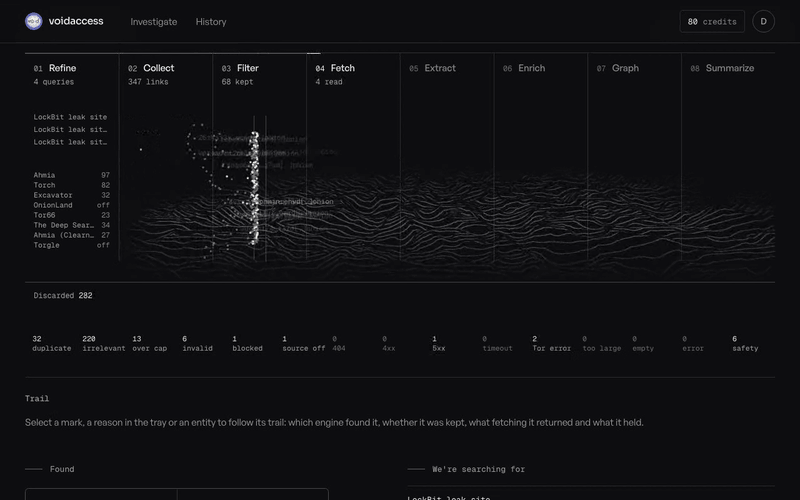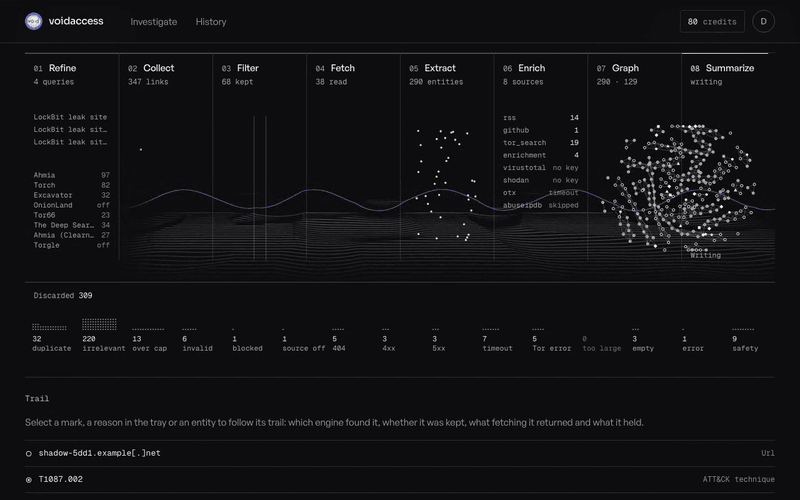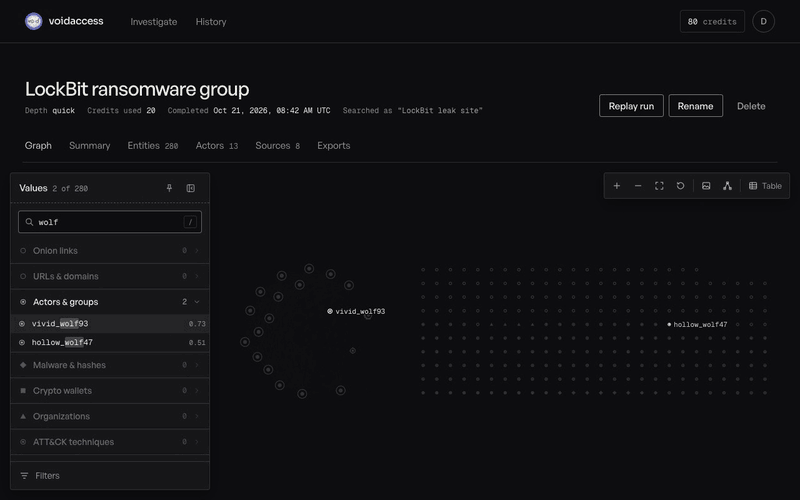
An investigation on voidaccess.pro: the live view collects and filters dark-web results, then the results open as a searchable graph

Hosted, at voidaccess.pro

Skip the setup. Keep your distance.

The hosted version runs this engine for you. Searches and page fetches go out from our servers through Tor, so your research doesn't start from your laptop or office network. A live view shows every link found, kept or discarded (duplicates, 404s, timeouts, the safety filter), then the results open as a graph with every value searchable by category.

Start free at voidaccess.pro →

How it works

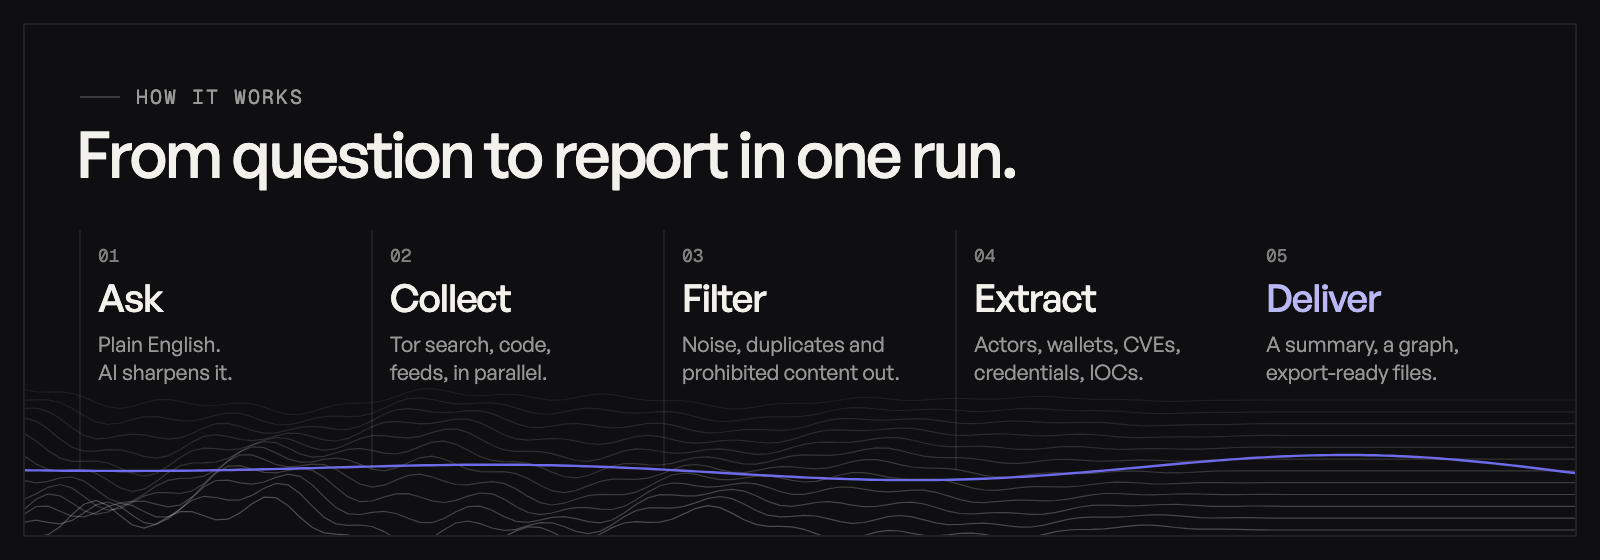
Ask, collect, filter, extract, deliver

One query fans out in parallel to 12+ Tor search engines, code hosts, security feeds and curated .onion seeds, then follows new .onion links as it finds them. Prohibited queries, URLs and content are dropped at mandatory safety gates. The full pipeline, with timeouts and recovery, is in Architecture.

What it finds

Category Examples
Threat actors Actor handles, ransomware groups, malware families, MITRE ATT&CK techniques
Infrastructure IPv4/IPv6, domains, URLs, .onion addresses, file hashes
Crypto wallets Bitcoin, Ethereum, Monero, Litecoin, Zcash, Solana, Tron and more
Credentials Cloud keys, tokens, JWTs, API keys, stealer-log and combo-list entries (masked)
Messaging Telegram, Discord, XMPP, Tox, Session, Matrix, Wire, ICQ, Wickr
Vulnerabilities CVEs, Exploit-DB IDs

Entities are linked into a relationship graph with communities and infrastructure clusters, and cross-referenced against earlier findings.

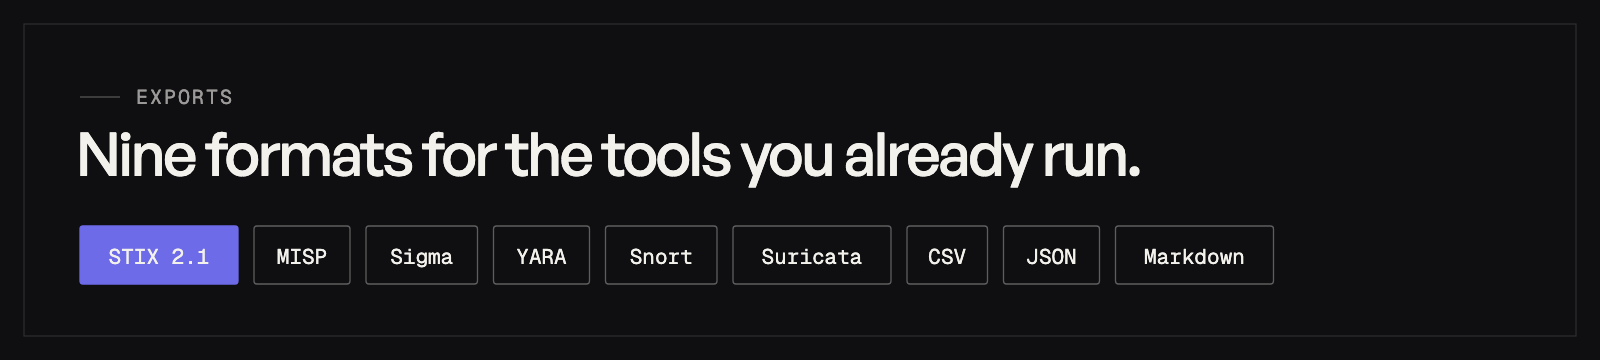
Nine export formats: STIX 2.1, MISP, Sigma, YARA, Snort, Suricata, CSV, JSON, Markdown

Run it yourself

Open source at the core. MIT.
pip install voidaccess
voidaccess configure                      # LLM provider, enrichment keys, Tor
voidaccess investigate "LockBit ransomware"
voidaccess export <id> --format stix     # stix, misp, sigma, yara, snort, suricata, package, csv, md, json

No Tor or LLM key yet? voidaccess investigate "LockBit ransomware" --no-llm --no-tor --depth shallow runs a clearnet-only pass. For the full stack (PostgreSQL, Tor, API and web UI) with Docker Compose, see the self-hosting guide. Python 3.10+.

CLI reference
Command Description
voidaccess investigate "QUERY" Run an investigation
voidaccess show Open the interactive entity browser
voidaccess export ID --format FORMAT Export as STIX, MISP, Sigma, YARA, Snort, Suricata, package, CSV, Markdown or JSON
voidaccess package ID Build an IOC package ZIP
voidaccess enrich ID Re-enrich a saved investigation
voidaccess list List saved investigations
voidaccess status Show configuration, Tor, cache, engine and seed status
voidaccess actors List persistent actor profiles
voidaccess actor HANDLE [--timeline] [--note "TEXT"] Show an actor, its timeline, or add a note
voidaccess configure [llm | keys | tor] Run the setup wizard, or one part of it
voidaccess version Print the installed version

Optional clearnet requests can use ScrapingAnt with --use-scraping-api or --use-proxies; Tor, .onion, GitHub and GitLab traffic are unaffected.

Sources and enrichment
Layer Sources
Dark-web search 12+ Tor search engines and curated .onion seeds
Open-web collection Paste sites, GitHub, GitLab and curated RSS feeds
Threat feeds AlienVault OTX, abuse.ch (MalwareBazaar, ThreatFox, URLhaus), CISA KEV
IP and domain context Shodan InternetDB, GreyNoise, AbuseIPDB, Feodo Tracker, crt.sh, URLScan.io, Wayback Machine, CIRCL PDNS, RDAP
File and identity context VirusTotal, Hybrid Analysis, Have I Been Pwned, EmailRep
Blockchain BlockCypher and Etherscan

Sources that need an API key are skipped cleanly without one. The hosted version uses a subset whose terms allow it. Full configuration: Architecture. For full sentence-transformer embeddings, pip install "voidaccess[nlp]"; without it, a deterministic fallback encoder is used.

LLM providers
Provider Typical models Notes
OpenRouter DeepSeek, Llama, Claude Default route; free models available
Groq Llama Fast hosted inference with a free tier
OpenAI GPT models API key required
Anthropic Claude Claude Haiku is the tested default
Google Gemini Gemini Flash and Pro Google AI Studio key required
Ollama Any installed local model Local, suitable for air-gapped deployments

voidaccess.pro · Self-hosting · Architecture · Contributing · Security · Usage policy · PyPI

License

MIT. Use VoidAccess only for authorized security research and threat-intelligence work; see the Usage Policy.

voidaccess (KatrielMoses/voidaccess)

正在搜索数据库…

这是什么?VoidAccess 是一个自托管的 OSINT 平台,通过包含采集、实体提取、富化、关系图谱构建和导出的 13 步流水线,把暗网调查查询转化为结构化威胁情报,定位为 Recorded Future、DarkOwl 和 Flare 的免费替代品。
这是命令行工具还是网页应用?两者都是:它既可以作为 CLI 在本地使用 SQLite 运行,也可以作为带 PostgreSQL 和浏览器网页界面的 Docker Compose 服务栈部署。
怎么把它跑起来?安装本地 CLI 的 Python 包(基于 SQLite)并运行设置向导,或通过 Docker Compose 自托管完整服务栈(PostgreSQL、Tor、FastAPI、Next.js)。
它需要 Tor 和 LLM API 密钥才能工作吗?采集需要访问 Tor,查询优化和分析需要 LLM 服务商;默认使用 OpenRouter 的免费模型,也可以接入 Groq、OpenAI、Anthropic、Google Gemini 或本地 Ollama 模型。Shodan、VirusTotal 等富化集成如果未配置 API 密钥,会直接跳过,不会报错。
在暗网上查询任何内容都是免费的吗?不是。强制性的内容安全闸门会在流水线的每个阶段过滤被禁止的查询、URL、内容和提取出的实体,并且项目依据《使用政策》将使用限定为经授权的安全研究。
这是为谁设计的?面向安全研究人员、威胁情报团队以及其他经授权的调查人员,帮助他们在同一工作流中完成采集、富化、关系图谱构建和导出。
它能完全离线运行吗?可以。它支持在 LLM 步骤中使用本地 Ollama 模型,因此流水线可以在离线隔离环境中运行;如果没有安装可选的 PyTorch/sentence-transformer 依赖,它会退回到确定性的 SHA-256 编码器生成嵌入向量,而不是直接报错。
它能提取哪些类型的实体?它可以提取加密货币地址、网络指标(IP、域名、.onion 链接、PGP 密钥)、文件哈希和恶意软件家族、泄露的凭据和令牌、即时通讯账号、CVE 和 MITRE ATT&CK 技术、YARA/Snort 规则等检测内容,以及威胁行为体身份。
支持哪些导出格式?调查结果可以导出为 STIX 2.1、MISP、Sigma、YARA、Snort、Suricata、CSV、Markdown 或 JSON,也可以通过 CLI 打包成 IOC 包 ZIP 文件。
它会记住过去的调查和行为体吗?会。行为体情报会保存别名、基础设施、备注、时间线以及跨调查的关联关系,你可以用 voidaccess actor HANDLE --timeline 之类的命令浏览行为体档案或为其添加批注。
它究竟从哪里采集暗网内容?它会并行采集 16 个以上的 Tor 搜索引擎和精选的 .onion 种子站点,以及 Pastebin、GitHub、GitLab 和 RSS 源等明网来源,然后将发现的结果与 AlienVault OTX、abuse.ch、CISA KEV 等威胁情报源交叉比对。
大小
40.3 MB
星标
1.1K
时长
6个月
提交 · 90 天