





What is this?
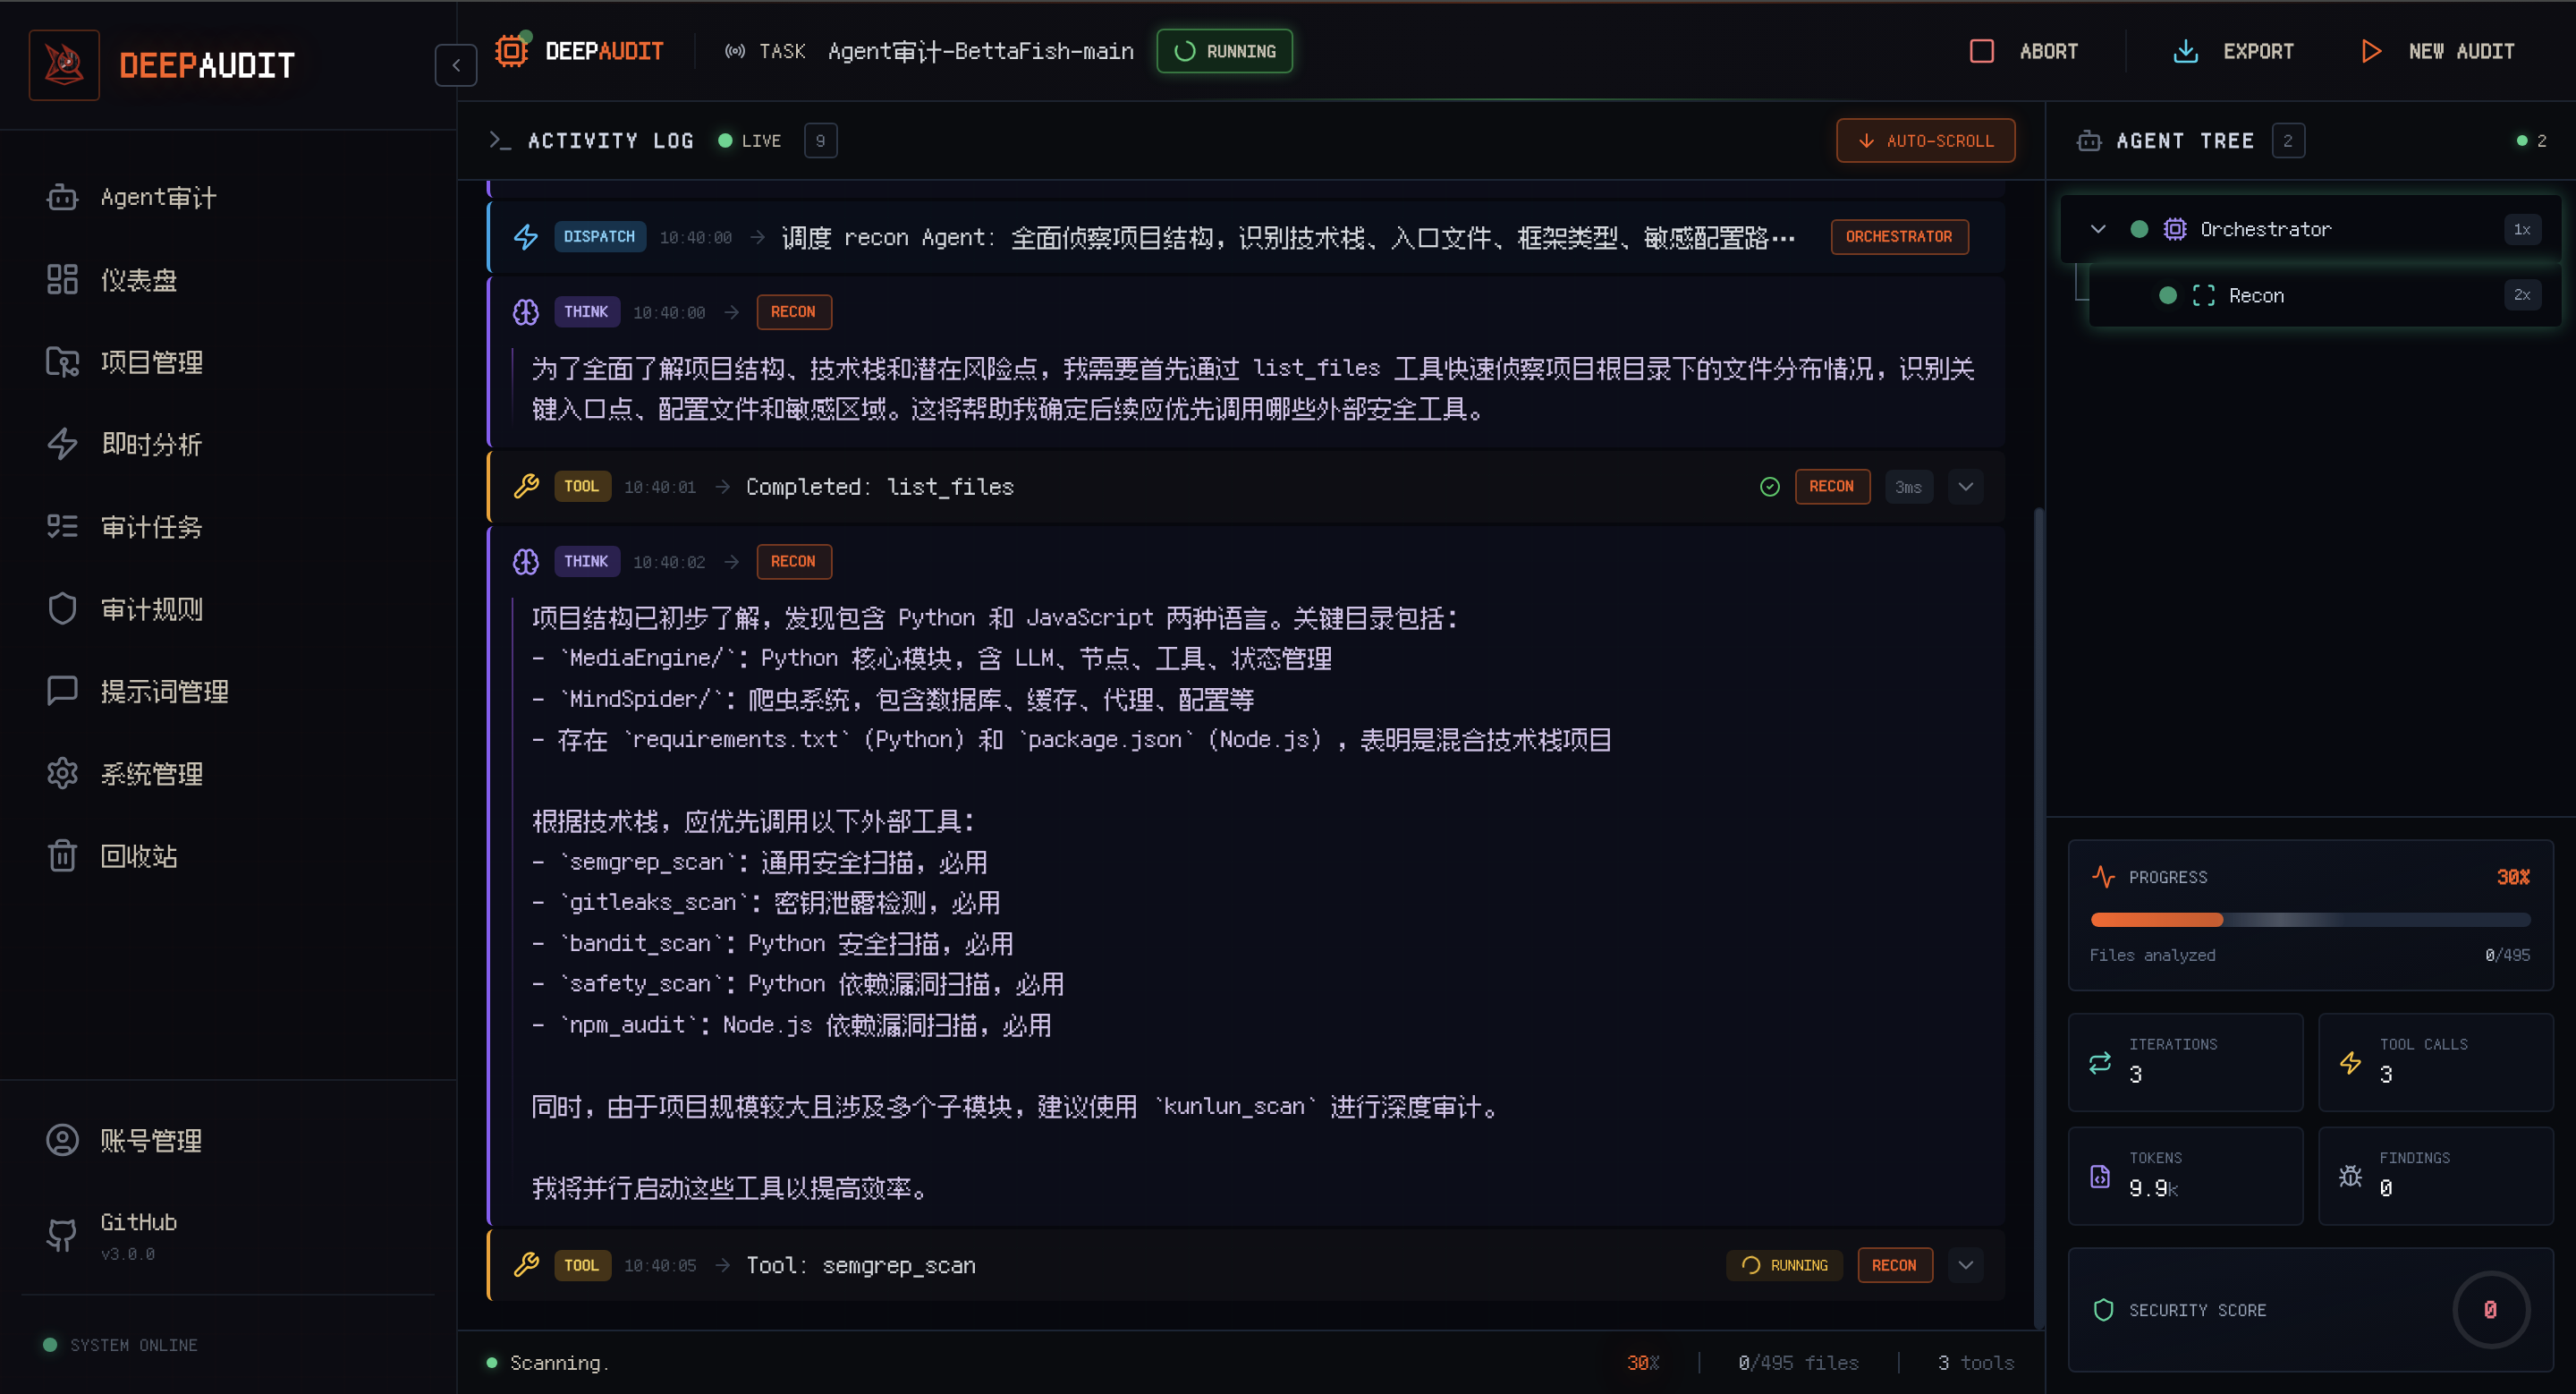
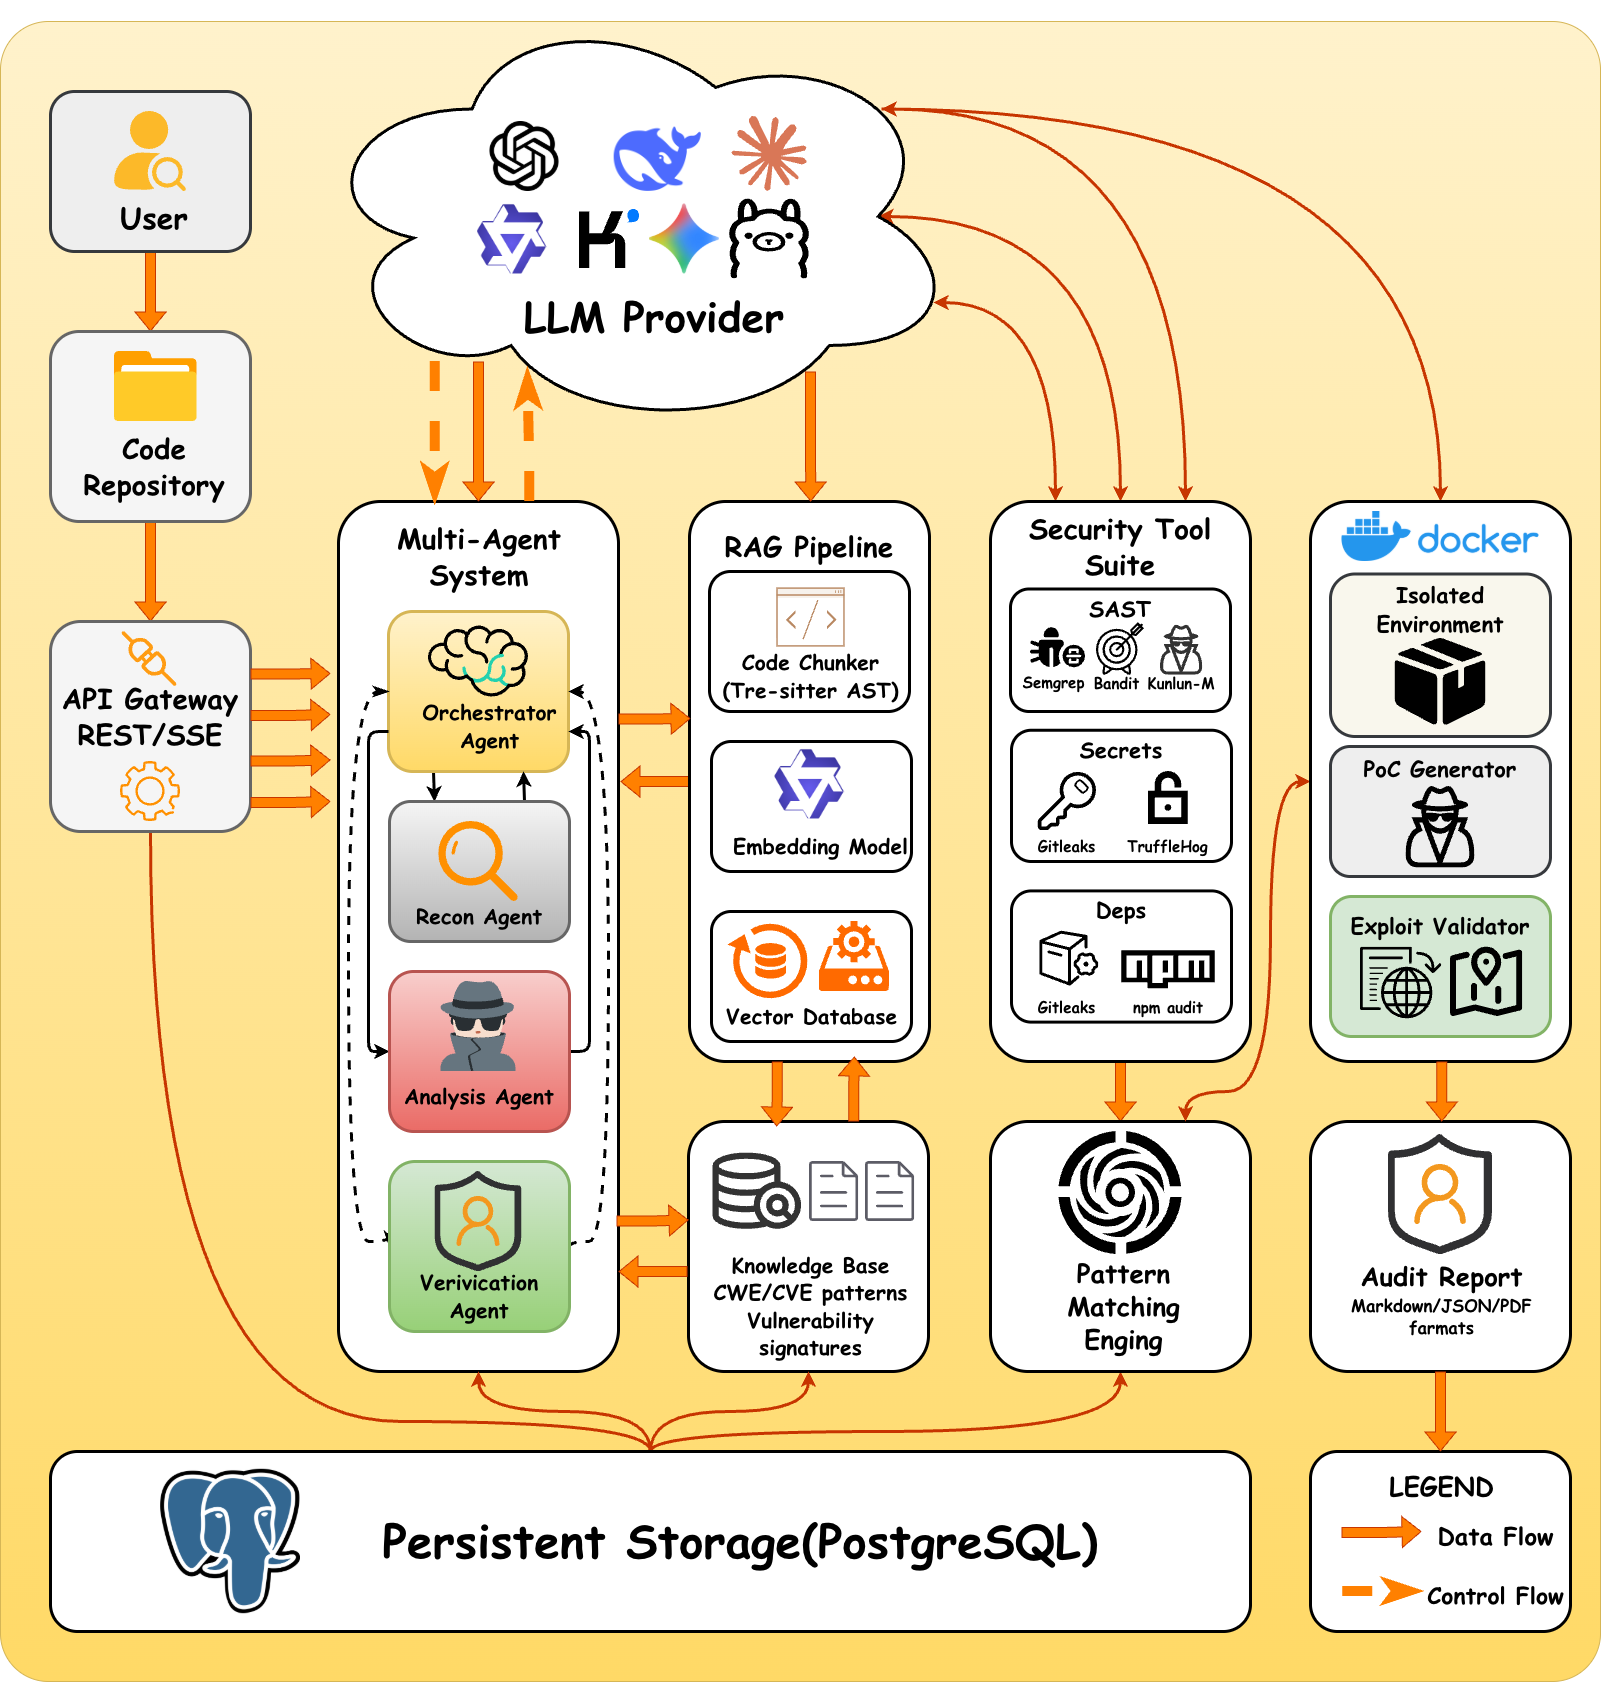
 DeepAudit is a multi-agent AI platform for code security auditing. It mimics how a security expert thinks, using cooperating agents (Orchestrator, Recon, Analysis, Verification) to find vulnerabilities and then verify them with automated sandbox PoC exploitation.
Is this a static scanner or something more?It is more than a static scanner: it is a self-hosted multi-agent system with a React/TypeScript web dashboard on top of a Python backend, where several specialized agents collaborate instead of a single rule-based scan.
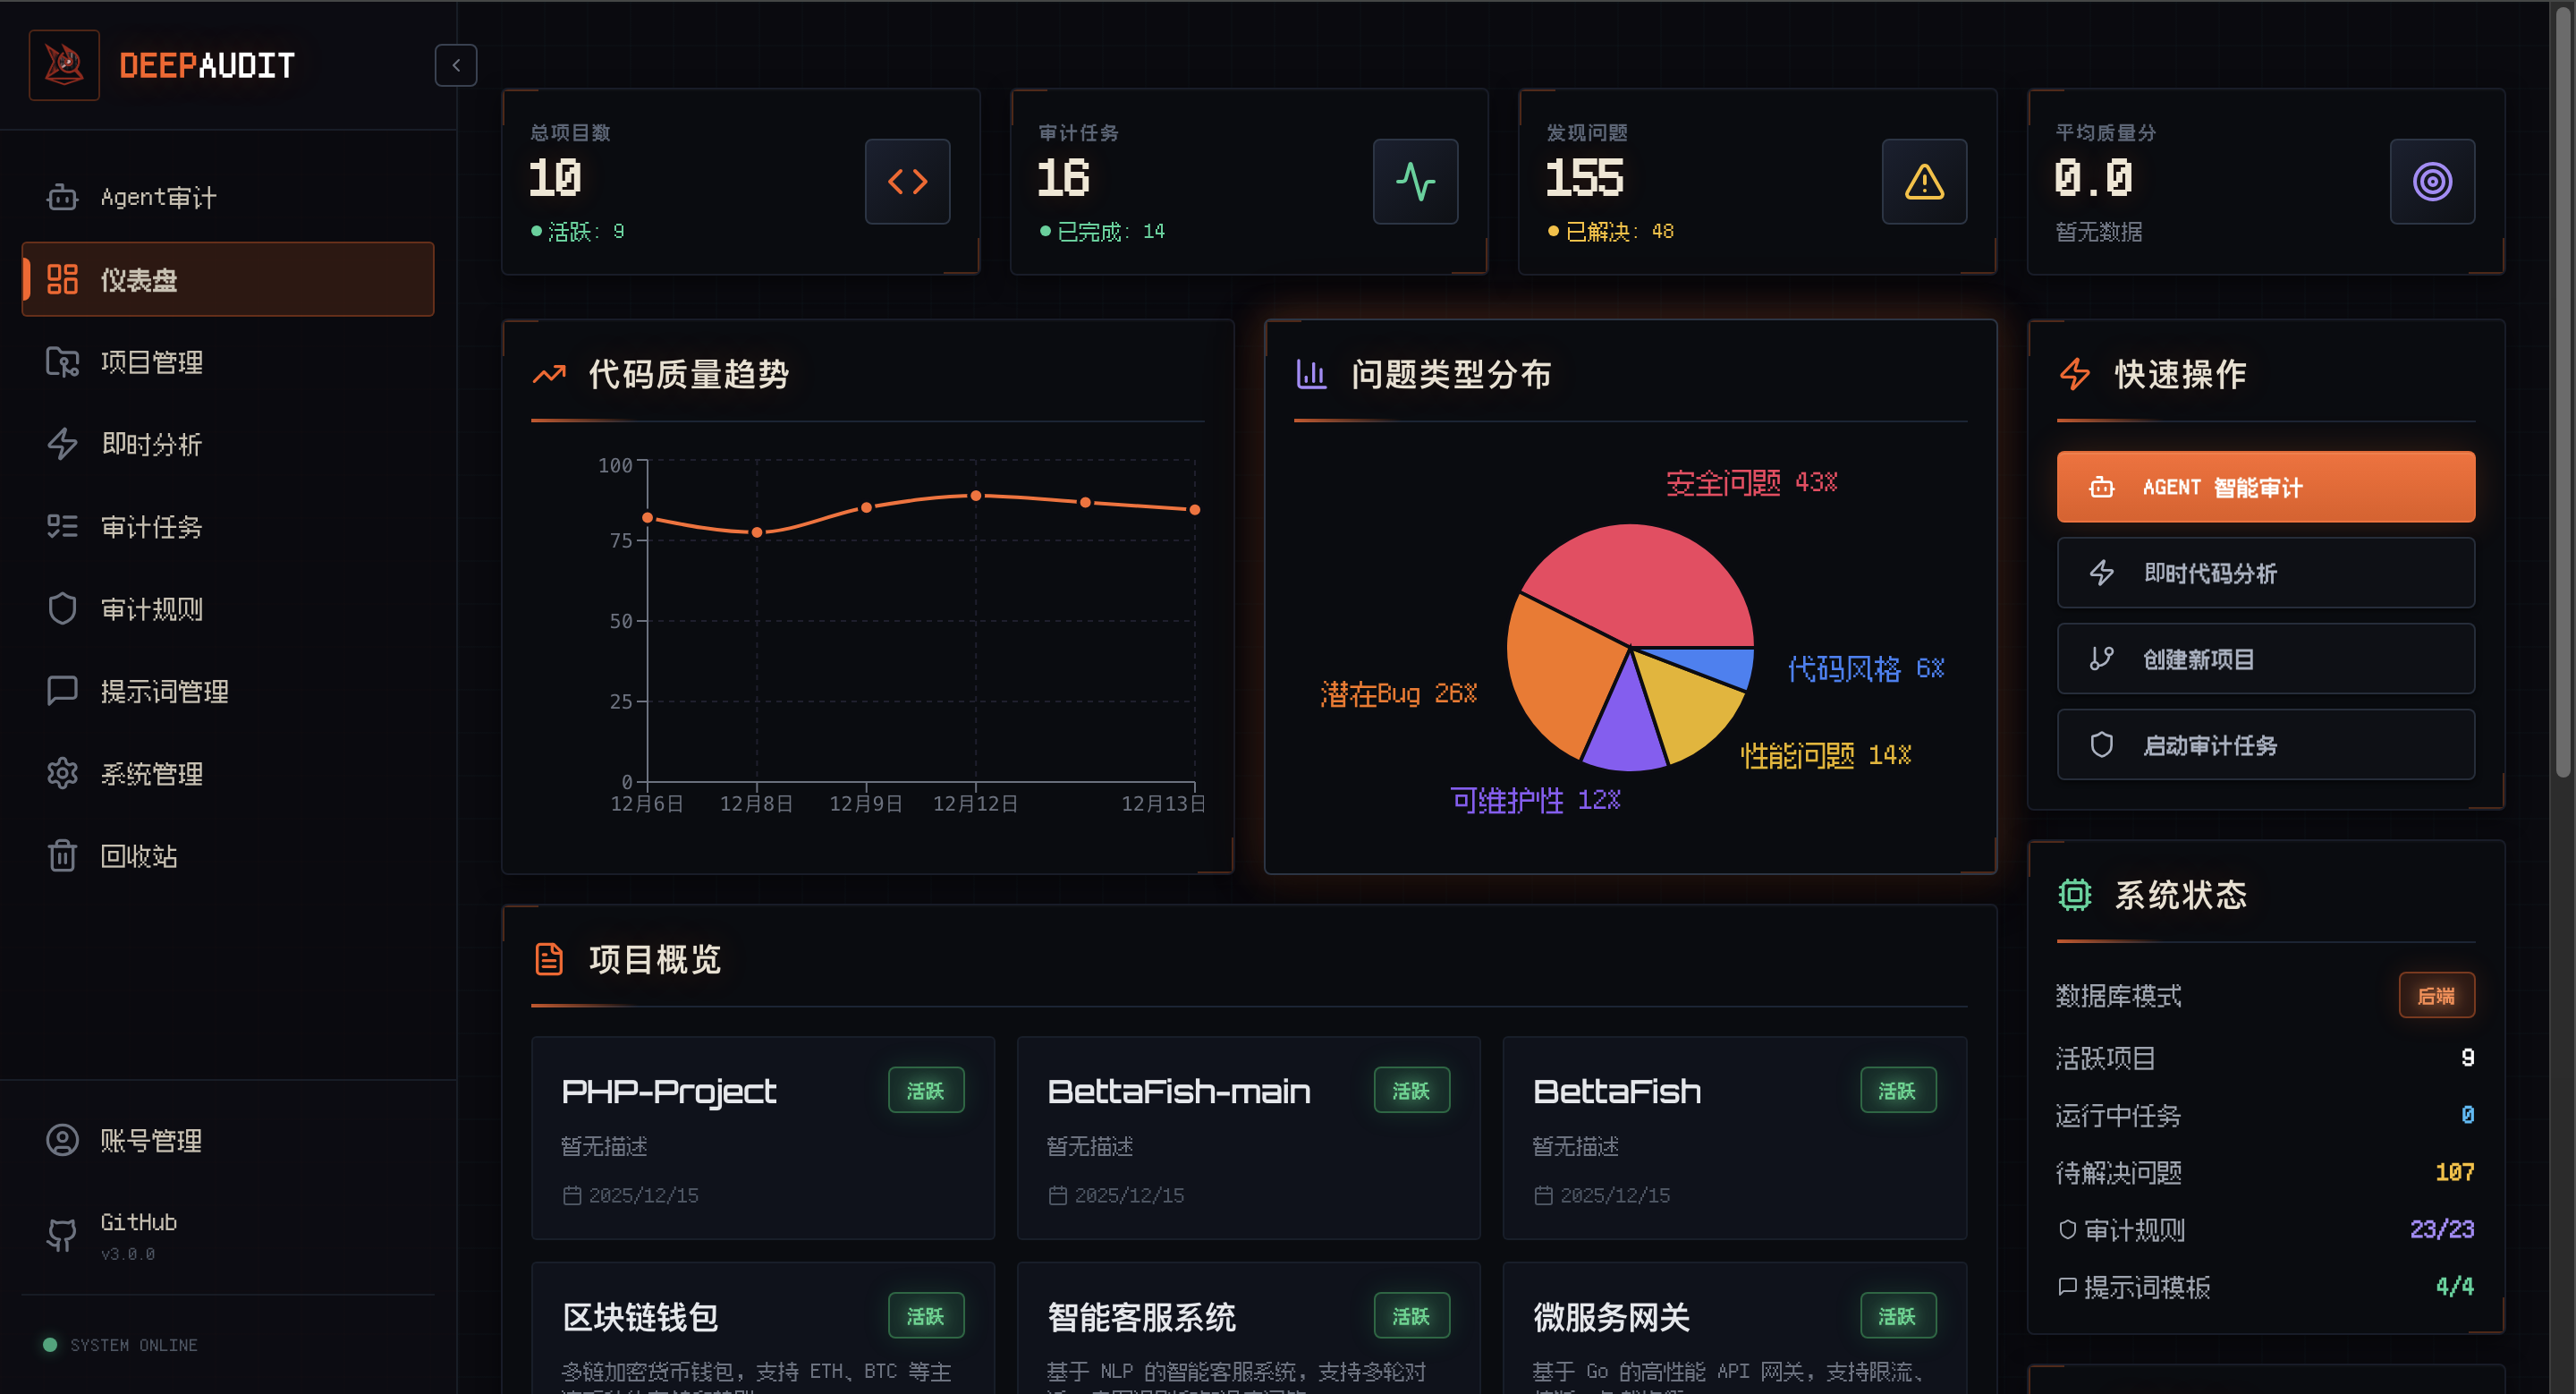
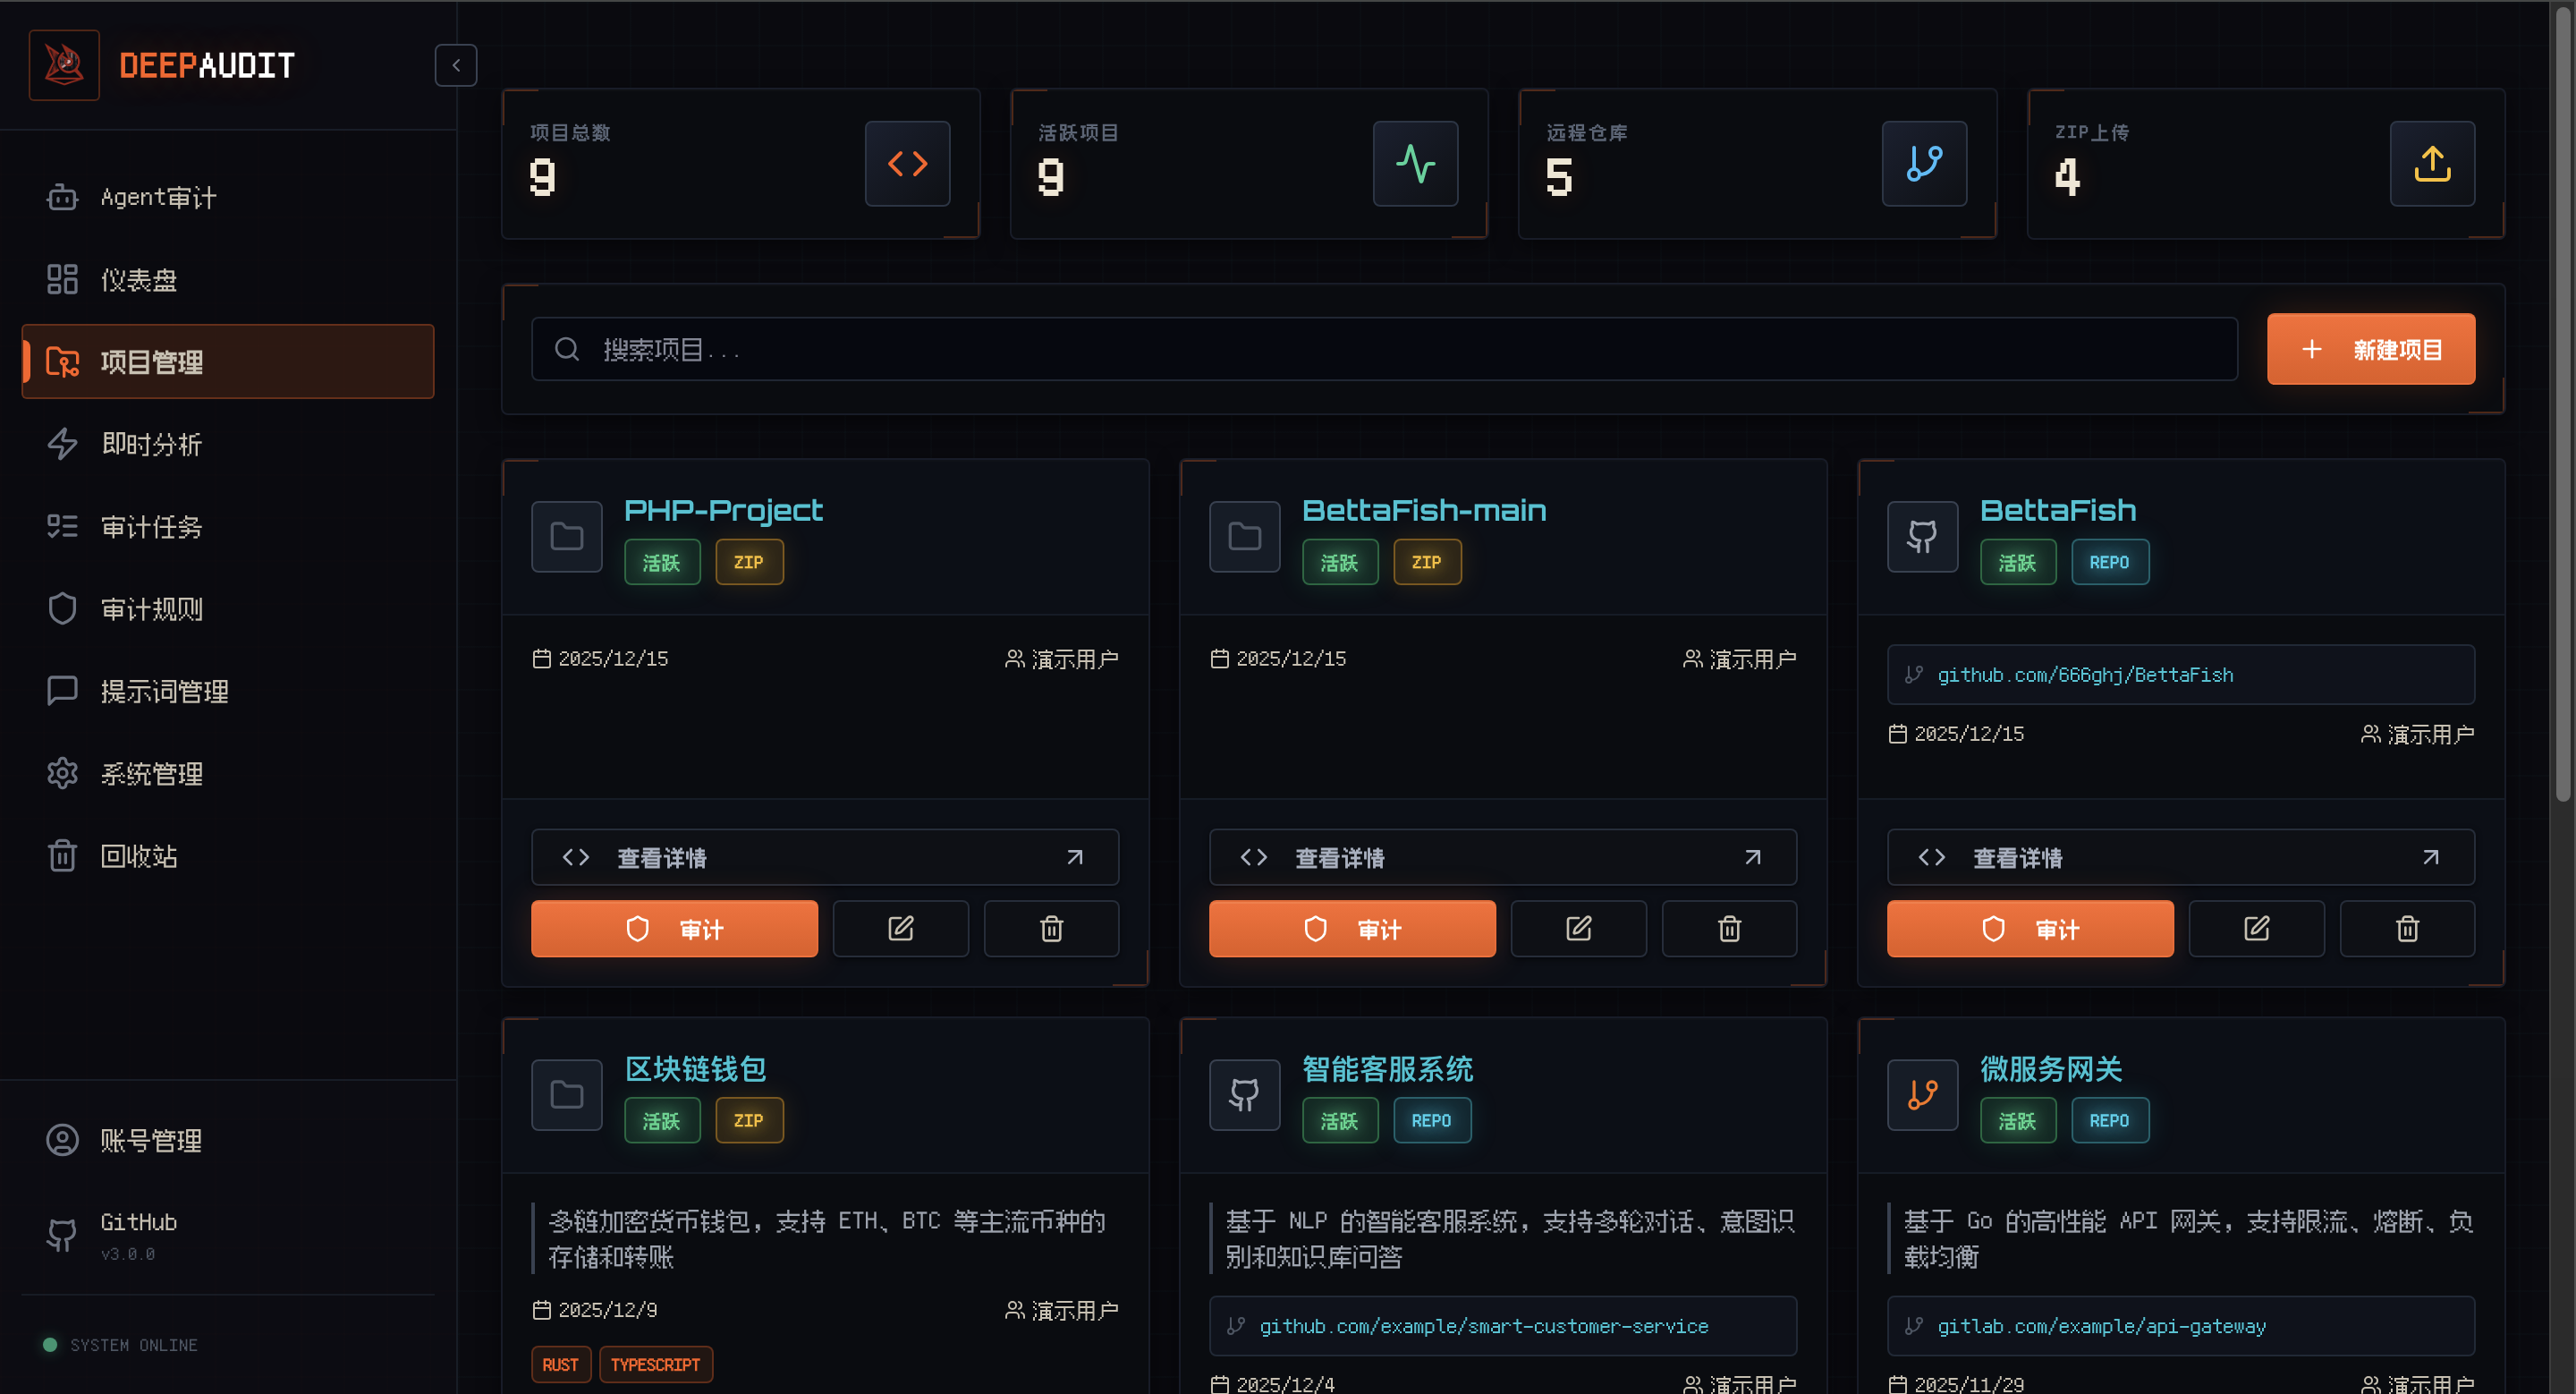
It is more than a static scanner: it is a self-hosted multi-agent system with a React/TypeScript web dashboard on top of a Python backend, where several specialized agents collaborate instead of a single rule-based scan.How do I start auditing a project with it?You connect a repository from GitHub, GitLab or Gitea and manage multiple projects from the dashboard; DeepAudit then automatically works through tech-stack detection, risk analysis, PoC generation, sandbox verification and report generation.
You connect a repository from GitHub, GitLab or Gitea and manage multiple projects from the dashboard; DeepAudit then automatically works through tech-stack detection, risk analysis, PoC generation, sandbox verification and report generation.What do I need to run the PoC verification step?Docker is required because the Verification Agent writes exploit scripts and runs them inside a Docker sandbox to confirm whether a finding is really exploitable; it also supports Ollama for running local models like Llama3 or DeepSeek.
Docker is required because the Verification Agent writes exploit scripts and runs them inside a Docker sandbox to confirm whether a finding is really exploitable; it also supports Ollama for running local models like Llama3 or DeepSeek.Does the PoC verification always succeed on the first try?No — if the generated exploit script fails to prove the vulnerability, the Verification Agent self-corrects and retries rather than giving up immediately.
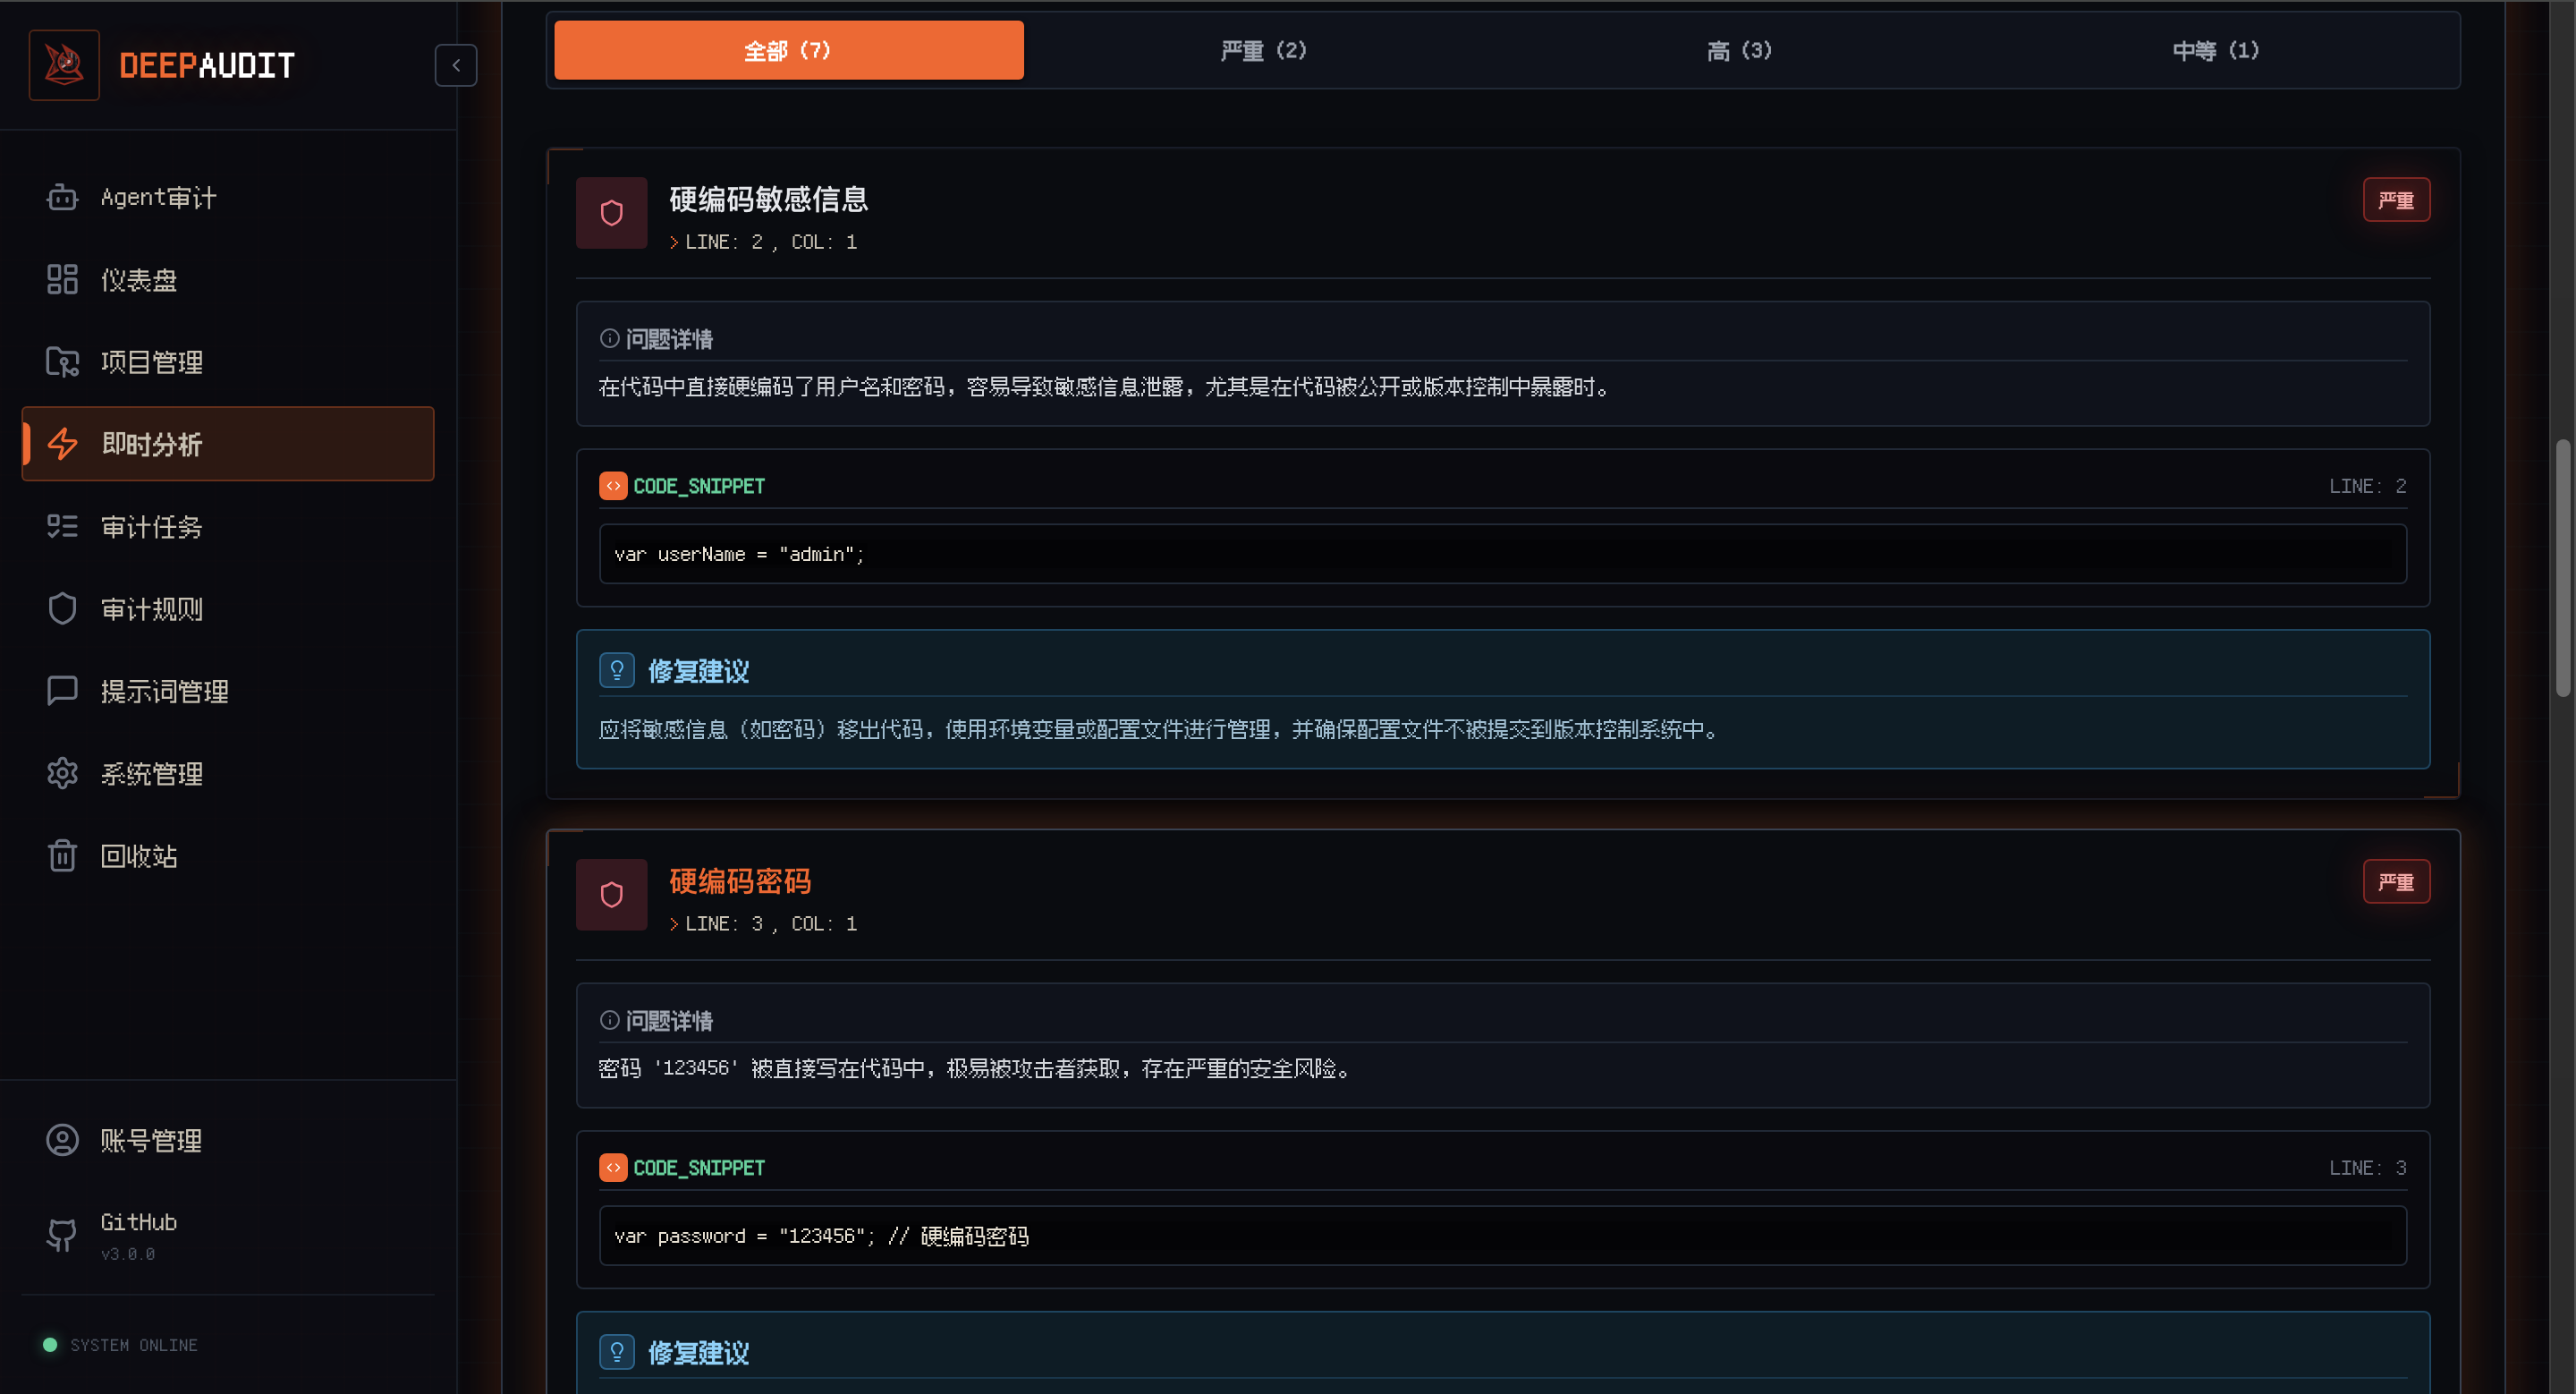
No — if the generated exploit script fails to prove the vulnerability, the Verification Agent self-corrects and retries rather than giving up immediately.How is this different from a traditional SAST tool?Traditional SAST tools flag issues with no semantic understanding, causing high false-positive rates and no way to tell if a bug is real. DeepAudit adds a RAG knowledge base for context-aware analysis and a sandboxed PoC step that actually exploits the finding before it is reported.
Traditional SAST tools flag issues with no semantic understanding, causing high false-positive rates and no way to tell if a bug is real. DeepAudit adds a RAG knowledge base for context-aware analysis and a sandboxed PoC step that actually exploits the finding before it is reported.What has DeepAudit's closed-source beta actually found?The internal (closed-source) version of DeepAudit has been credited with 49 CVEs and 6 GHSA advisories across 17 known open-source projects, including several high-severity bugs in OpenClaw like signature-verification bypass and remote code execution.
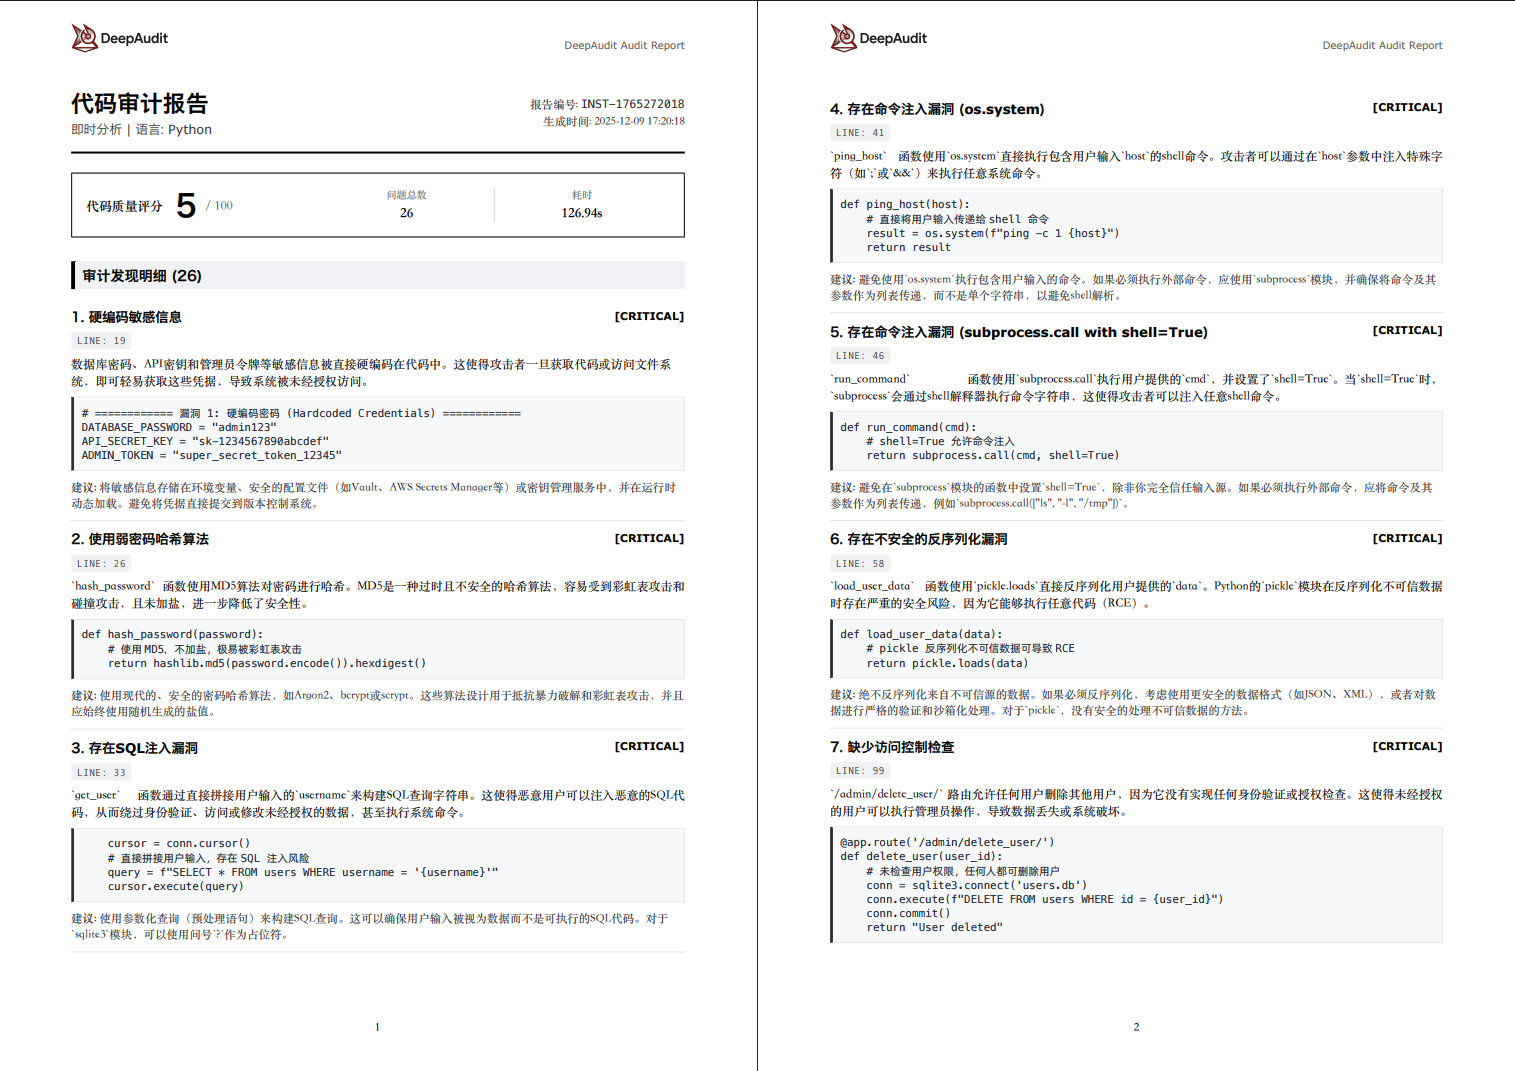
The internal (closed-source) version of DeepAudit has been credited with 49 CVEs and 6 GHSA advisories across 17 known open-source projects, including several high-severity bugs in OpenClaw like signature-verification bypass and remote code execution.What report formats can I export?Audit results can be exported as PDF, Markdown, or JSON reports summarizing the agents' findings after false positives have been filtered out.
Audit results can be exported as PDF, Markdown, or JSON reports summarizing the agents' findings after false positives have been filtered out.What is the full audit pipeline?It runs in five stages: the Orchestrator plans the audit, the Recon Agent maps the attack surface, the Analysis Agent hunts for vulnerabilities using AST and RAG, the Verification Agent proves exploitability in a Docker sandbox, and the Orchestrator compiles the final report.
It runs in five stages: the Orchestrator plans the audit, the Recon Agent maps the attack surface, the Analysis Agent hunts for vulnerabilities using AST and RAG, the Verification Agent proves exploitability in a Docker sandbox, and the Orchestrator compiles the final report.What are similar projects?semgrep, 0, mike, VulnHunter, SkillSpector, MemoryBear, sim, Cybermes
semgrep, 0, mike, VulnHunter, SkillSpector, MemoryBear, sim, CybermesWhich topics is it in?sast, security-scanner, xai, supabase, devsecops, vulnerability-scanner, code-quality, code-review, microservices, vite, local-llm, ollama
sast, security-scanner, xai, supabase, devsecops, vulnerability-scanner, code-quality, code-review, microservices, vite, local-llm, ollama