
netbird README

The project's README from github.com/netbirdio/netbird. As one markdown file: README.md.

NetBird logo

SonarCloud alert status BSD-3 License NetBird Slack Community forum Gurubase: Ask NetBird Guru

Start using NetBird at netbird.io
See Documentation
Join our Slack channel or our Community forum


🚀 We are hiring! Join us at https://netbird.io/careers

🤖 NetBird Agent Network (Beta)

Identity-aware access control for AI agents — keyless access to LLM APIs and private resources over the encrypted NetBird tunnel. See agent-network/ or read the docs at netbird.ai.

NetBird combines a configuration-free peer-to-peer private network and a centralized access control system in a single platform, making it easy to create secure private networks for your organization or home.

Connect. NetBird creates a WireGuard-based overlay network that automatically connects your machines over an encrypted tunnel, leaving behind the hassle of opening ports, complex firewall rules, VPN gateways, and so forth.

Secure. NetBird enables secure remote access by applying granular access policies while allowing you to manage them intuitively from a single place. Works universally on any infrastructure.

https://github.com/user-attachments/assets/10cec749-bb56-4ab3-97af-4e38850108d2

Self-host NetBird (video)

Watch the video

Key features

Connectivity Management Security Automation Platforms
✓ Kernel WireGuard ✓ Admin Web UI ✓ SSO & MFA support ✓ Public API ✓ Linux
✓ Peer-to-peer connections ✓ Auto peer discovery and configuration ✓ Access control: groups & rules ✓ Setup keys for bulk provisioning ✓ macOS
✓ Connection relay fallback ✓ IdP integrations ✓ Activity logging ✓ Self-hosting quickstart script ✓ Windows
✓ Routes to external networks ✓ Private DNS ✓ Traffic events ✓ IdP groups sync with JWT ✓ Android
✓ Domain-based DNS routes ✓ Custom DNS zones ✓ Device posture checks ✓ Terraform provider ✓ Android TV
✓ Exit nodes ✓ Multiuser support ✓ Peer-to-peer encryption ✓ Ansible collection ✓ iOS
✓ IPv6 dual-stack overlay ✓ Multi-account profile switching ✓ SSH with central access policies ✓ Apple TV
✓ Browser SSH & RDP ✓ Quantum-resistance with Rosenpass ✓ FreeBSD
✓ Reverse proxy with auto-TLS ✓ Periodic re-authentication ✓ pfSense
✓ OPNsense
✓ MikroTik RouterOS
✓ OpenWRT
✓ Synology
✓ TrueNAS
✓ Proxmox
✓ Raspberry Pi
✓ Serverless
✓ Container

Quickstart with NetBird Cloud

Quickstart with self-hosted NetBird

This is the quickest way to try self-hosted NetBird. It should take around 5 minutes to get started if you already have a public domain and a VM. Follow the Advanced guide with a custom identity provider for installations with different IdPs.

Infrastructure requirements:

Software requirements:

Steps

export NETBIRD_DOMAIN=netbird.example.com; curl -fsSL https://github.com/netbirdio/netbird/releases/latest/download/getting-started.sh | bash

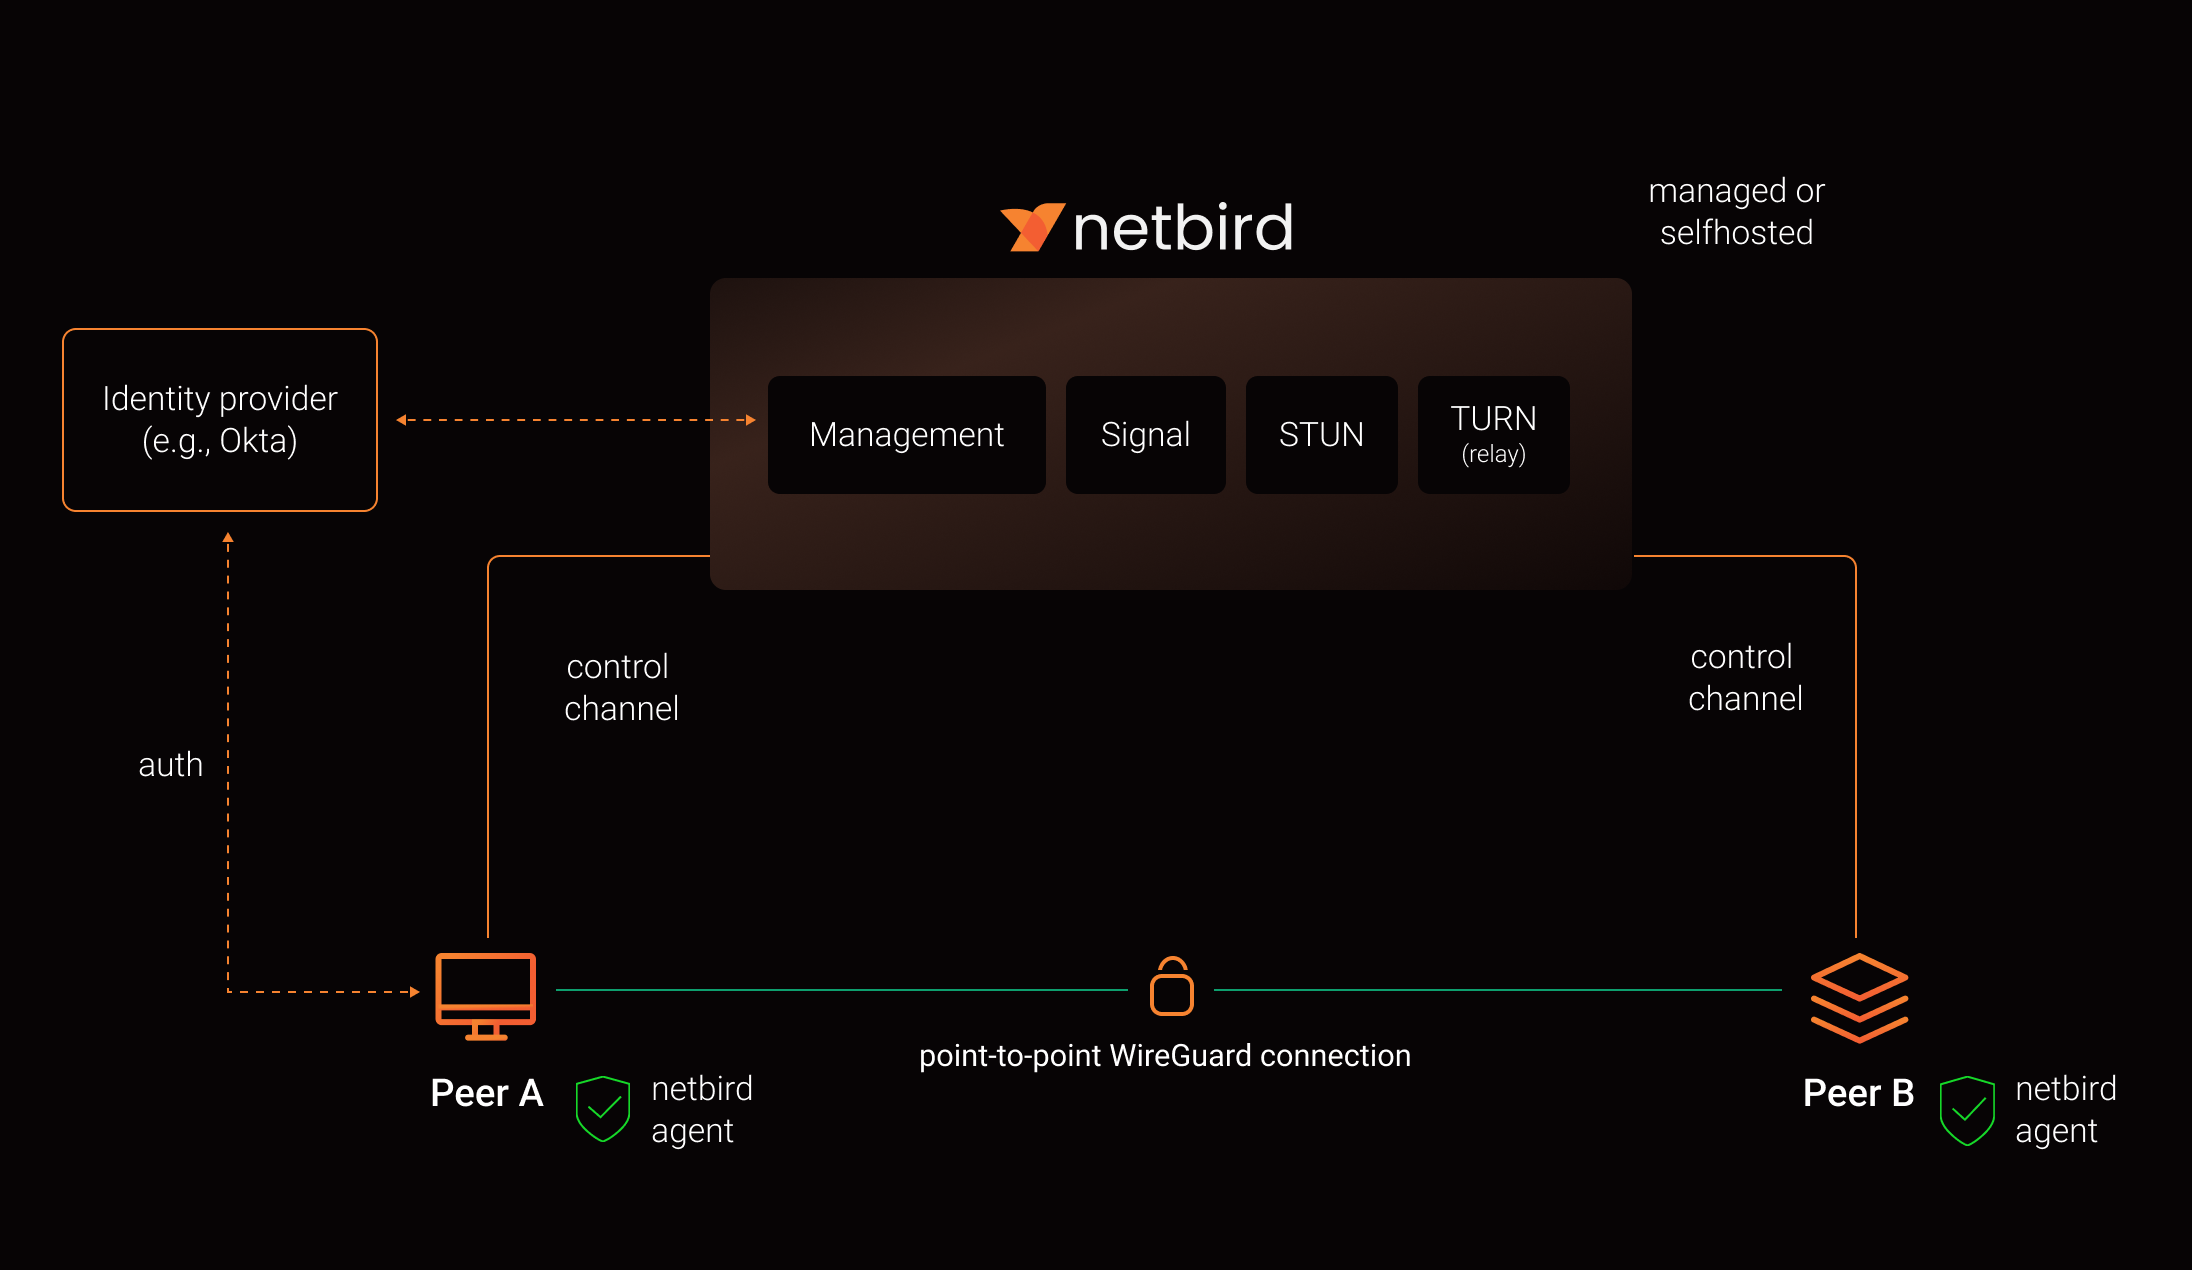
A bit on NetBird internals

NetBird high-level architecture diagram

See a complete architecture overview for details.

Community projects

Note: The main branch may be in an unstable or even broken state during development. For stable versions, see releases.

Support acknowledgement

In November 2022, NetBird joined the StartUpSecure program sponsored by the Federal Ministry of Education and Research of the Federal Republic of Germany. Together with the CISPA Helmholtz Center for Information Security, NetBird brings security best practices and simplicity to private networking.

CISPA_Logo_BLACK_EN_RZ_RGB (1)

Acknowledgements

We build on open source technologies like WireGuard®, Pion ICE, and Rosenpass. We greatly appreciate the work these projects are doing, and we'd love it if you could support them too (e.g., by starring or contributing).

This repository is licensed under the BSD-3-Clause license, which applies to all parts of the repository except for the directories management/, signal/ and relay/. Those directories are licensed under the GNU Affero General Public License version 3.0 (AGPLv3). See the respective LICENSE files inside each directory.

WireGuard and the WireGuard logo are registered trademarks of Jason A. Donenfeld.

netbird (netbirdio/netbird)

Searching Database…

30.1K ·GitHub
这是干什么的?NetBird 是一个开源的零信任网络平台:它会搭建一个无需配置的点对点 WireGuard 覆盖网络,并带有集中式访问控制,让你不用开放端口、不用复杂的防火墙规则、也不用 VPN 网关,就能创建安全的私有网络。
它是安装一个应用,还是要我自己跑一整套平台?两部分都有:每台机器上运行一个 NetBird 代理来管理 WireGuard,同时由一个管理服务保存网络状态——可以用 NetBird 云服务,也可以自己托管,全部通过管理网页界面来管理。
我该怎么上手?安装 NetBird 应用,用 Google、Microsoft、GitHub 或你的邮箱注册,然后到管理网页界面查看。如果要自托管,在一台 Linux 虚拟机(1 核 CPU、2 GB 内存)上运行快速安装脚本,需要 Docker Compose v2+ 和一个公网域名——大约 5 分钟就能搞定。
点对点连接一定都能建立吗?不一定——在运营商级 NAT 后面,直接的 p2p 连接可能失败,这时 NetBird 会改经一个中继服务(Relay Service)来建立安全的 WireGuard 隧道。
哪些设备和系统可以用它?Linux、macOS、Windows、FreeBSD、iOS、Android、Apple TV、树莓派,还有 pfSense、OPNsense、MikroTik RouterOS、OpenWRT、群晖、TrueNAS、Proxmox、容器和无服务器环境。
它是完全开源的吗?大部分是:整个仓库采用 BSD-3-Clause 许可证,但 management/、signal/ 和 relay/ 这三个目录除外,它们采用 AGPLv3 许可证。
我怎么控制网络里谁能访问什么?在管理网页界面里操作:基于分组和规则的访问策略、SSO 和 MFA 支持、IdP 集成、设备安全状态检查,以及由中央访问策略管控的 SSH。
NetBird Agent Network 是什么?一个测试版功能:面向 AI 代理的身份感知访问控制——通过加密的 NetBird 隧道,无需密钥即可访问 LLM API 和私有资源。
流量可以路由到我自己的节点之外吗?可以:支持到外部网络的路由、基于域名的 DNS 路由、出口节点、私有和自定义 DNS 区域,以及 IPv6 双栈覆盖网络。
我怎么一次性给大量机器做配置?可以使用 setup keys 批量配置、公开 API、Terraform provider 或 Ansible collection;通过 JWT 同步 IdP 分组能让成员关系与你的身份提供商保持一致。
main 分支可以直接部署吗?不行——开发期间它可能不稳定,甚至无法运行;要稳定的版本请使用正式的 releases。
Creator
netbirdio
Size
171.1 MB
Stars
30.1K
Age
5y
Commits · 90 Days