


Что это такое?
 NetBird — это Open Source-платформа сетей с нулевым доверием (Zero Trust): она строит одноранговую overlay-сеть на WireGuard без необходимости что-либо настраивать, с централизованным контролем доступа. Это позволяет создавать защищённые частные сети без открытых портов, сложных правил файрвола или VPN-шлюзов.
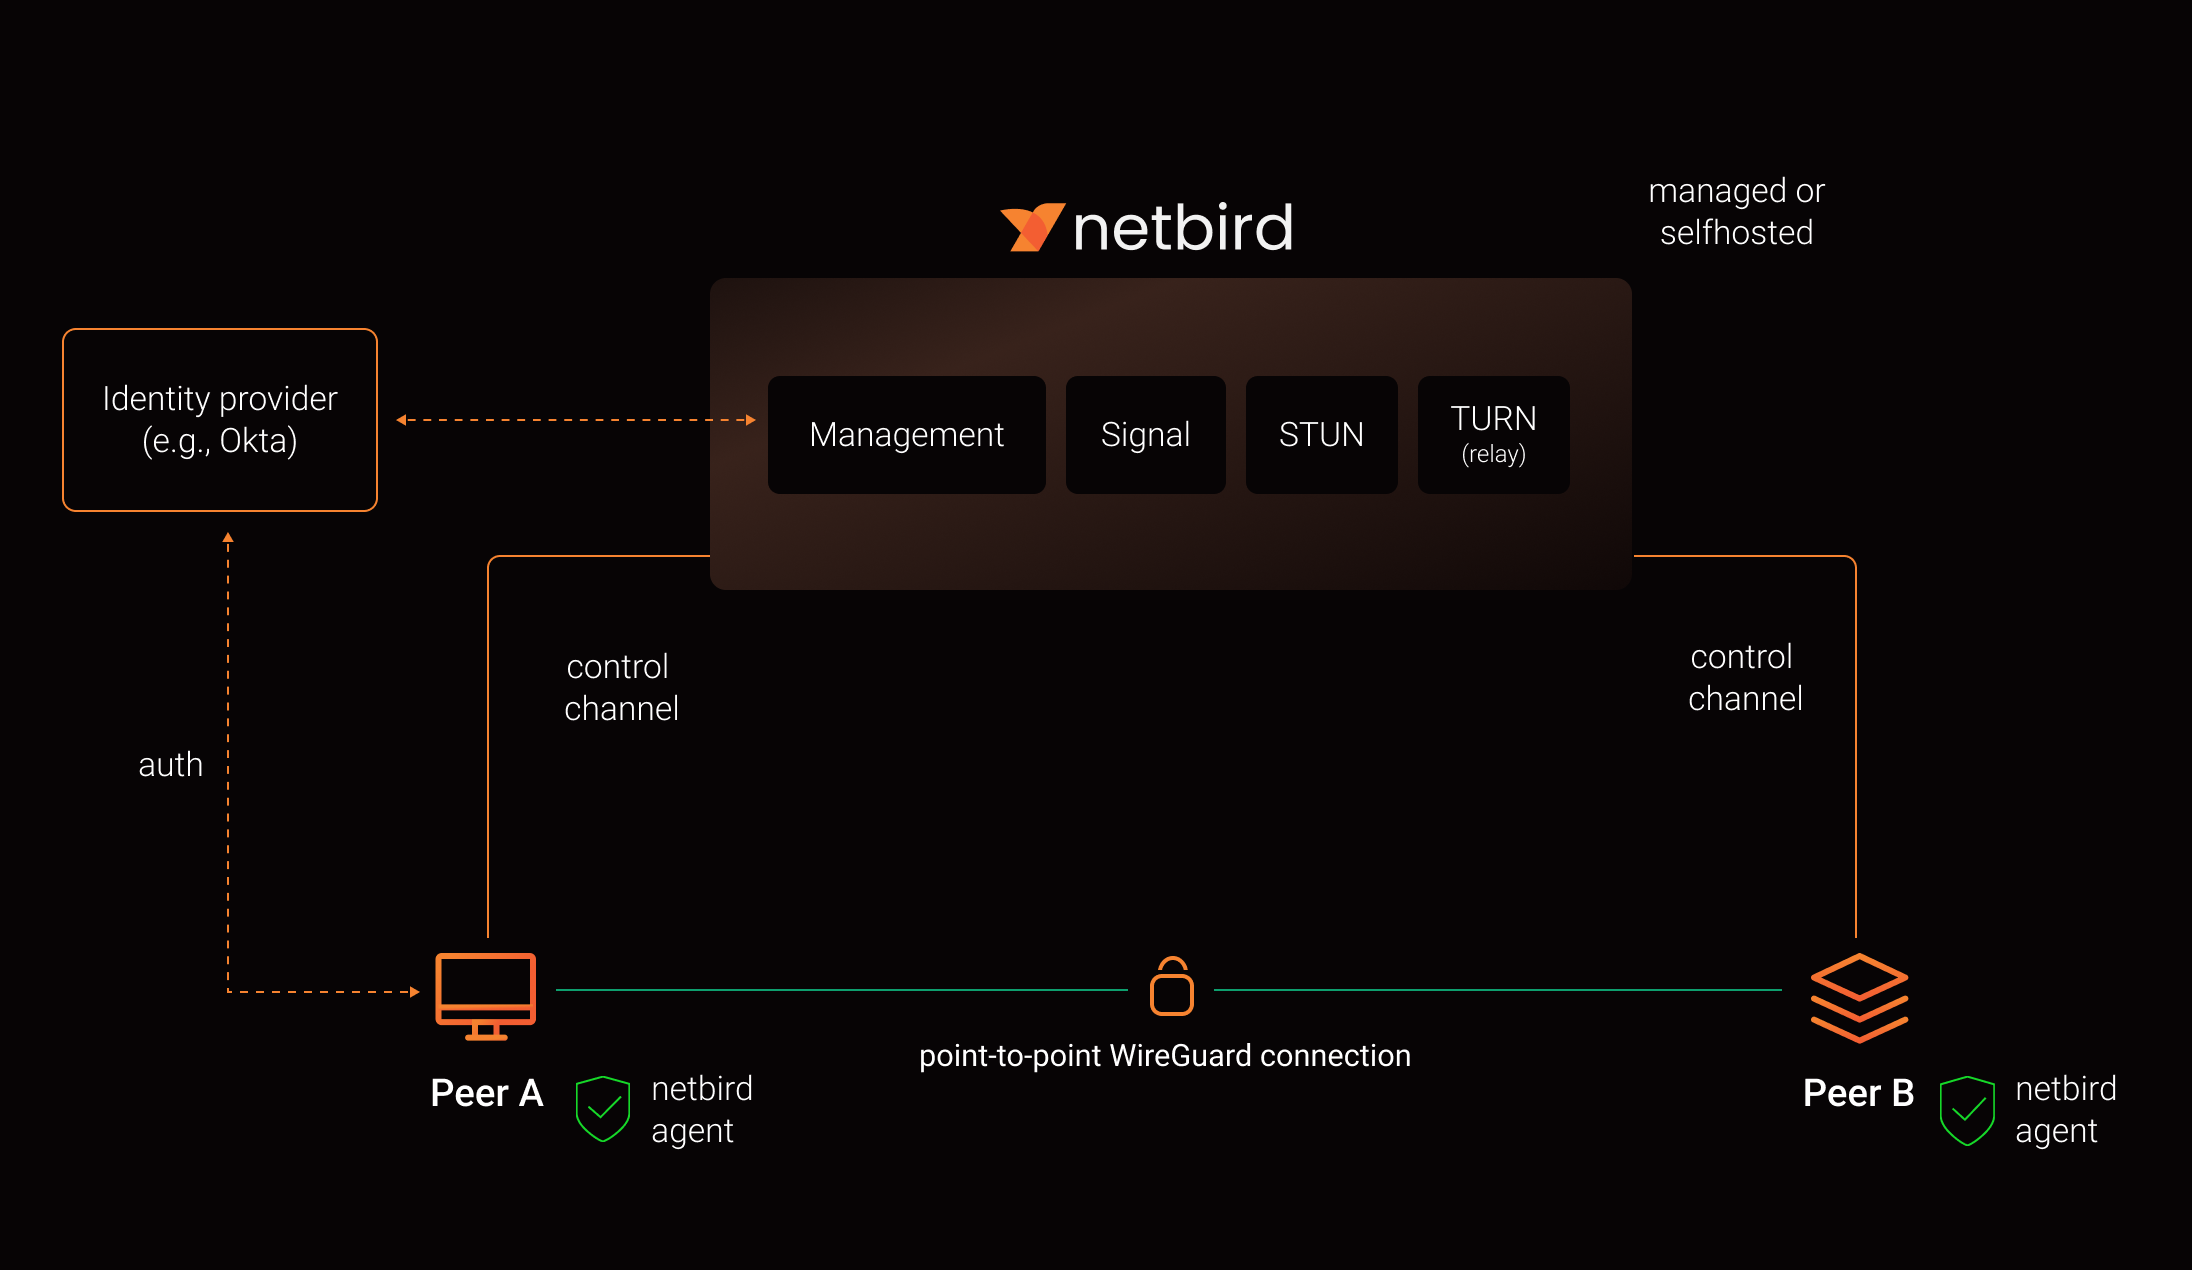
Это приложение, которое я устанавливаю, или целая платформа, которую нужно развернуть?И то и другое: на каждой машине работает агент NetBird, который управляет WireGuard, а сервис управления (Management Service) хранит состояние сети — это либо облако NetBird Cloud, либо ваш собственный self-hosted-экземпляр; всё управляется через веб-интерфейс администратора.
И то и другое: на каждой машине работает агент NetBird, который управляет WireGuard, а сервис управления (Management Service) хранит состояние сети — это либо облако NetBird Cloud, либо ваш собственный self-hosted-экземпляр; всё управляется через веб-интерфейс администратора.С чего мне начать?Установите приложение NetBird и зарегистрируйтесь через Google, Microsoft, GitHub или свою почту, затем откройте веб-интерфейс администратора. Для самостоятельного размещения запустите скрипт быстрой установки на Linux-виртуалке (1 CPU, 2 ГБ ОЗУ) с Docker Compose v2+ и публичным доменом — это займёт около 5 минут.
Установите приложение NetBird и зарегистрируйтесь через Google, Microsoft, GitHub или свою почту, затем откройте веб-интерфейс администратора. Для самостоятельного размещения запустите скрипт быстрой установки на Linux-виртуалке (1 CPU, 2 ГБ ОЗУ) с Docker Compose v2+ и публичным доменом — это займёт около 5 минут.Прямое соединение между устройствами работает всегда?Нет, не всегда — за carrier-grade NAT прямое p2p-соединение может не установиться, и тогда NetBird организует защищённый туннель WireGuard через Relay-сервис.
Нет, не всегда — за carrier-grade NAT прямое p2p-соединение может не установиться, и тогда NetBird организует защищённый туннель WireGuard через Relay-сервис.На каких устройствах и системах это работает?Linux, macOS, Windows, FreeBSD, iOS, Android и Apple TV, Raspberry Pi, а также pfSense, OPNsense, MikroTik RouterOS, OpenWRT, Synology, TrueNAS, Proxmox, контейнеры и serverless.
Linux, macOS, Windows, FreeBSD, iOS, Android и Apple TV, Raspberry Pi, а также pfSense, OPNsense, MikroTik RouterOS, OpenWRT, Synology, TrueNAS, Proxmox, контейнеры и serverless.Проект полностью открытый?Почти: лицензия BSD-3-Clause покрывает весь репозиторий, кроме каталогов management/, signal/ и relay/, которые распространяются под AGPLv3.
Почти: лицензия BSD-3-Clause покрывает весь репозиторий, кроме каталогов management/, signal/ и relay/, которые распространяются под AGPLv3.Как мне настроить, кто и к чему имеет доступ в сети?Через веб-интерфейс администратора: политики доступа на основе групп и правил, поддержка SSO и MFA, интеграции с IdP, проверки состояния устройств (device posture checks), а также SSH под контролем централизованных политик доступа.
Через веб-интерфейс администратора: политики доступа на основе групп и правил, поддержка SSO и MFA, интеграции с IdP, проверки состояния устройств (device posture checks), а также SSH под контролем централизованных политик доступа.Что такое NetBird Agent Network?Это бета-функция: контроль доступа с учётом личности для AI-агентов — доступ к LLM API и приватным ресурсам без ключей через зашифрованный туннель NetBird.
Это бета-функция: контроль доступа с учётом личности для AI-агентов — доступ к LLM API и приватным ресурсам без ключей через зашифрованный туннель NetBird.Можно ли направлять трафик дальше моих собственных устройств в сети?Да: маршруты во внешние сети, DNS-маршруты по доменам, exit-узлы, приватные и кастомные DNS-зоны, а также IPv6 dual-stack overlay.
Да: маршруты во внешние сети, DNS-маршруты по доменам, exit-узлы, приватные и кастомные DNS-зоны, а также IPv6 dual-stack overlay.Как подключить много машин сразу?Используйте setup-ключи для массового подключения, публичный API, Terraform-провайдер или коллекцию Ansible; синхронизация групп IdP через JWT держит состав участников сети в соответствии с вашим провайдером идентификации.
Используйте setup-ключи для массового подключения, публичный API, Terraform-провайдер или коллекцию Ansible; синхронизация групп IdP через JWT держит состав участников сети в соответствии с вашим провайдером идентификации.Безопасно ли разворачивать ветку main?Нет — во время разработки она может быть нестабильной и даже сломанной; для стабильных версий используйте релизы.
Нет — во время разработки она может быть нестабильной и даже сломанной; для стабильных версий используйте релизы.What are similar projects?pangolin, nebula, tailscale, algo, EasyTier, netmaker, SoftEtherVPN, tailcat
pangolin, nebula, tailscale, algo, EasyTier, netmaker, SoftEtherVPN, tailcatWhich topics is it in?wireguard-vpn, nat-traversal, ansible, terraform, wireguard, firewall, remote-access, sso, network-security, p2p, raspberry-pi, vpn
wireguard-vpn, nat-traversal, ansible, terraform, wireguard, firewall, remote-access, sso, network-security, p2p, raspberry-pi, vpn