



Что это такое?
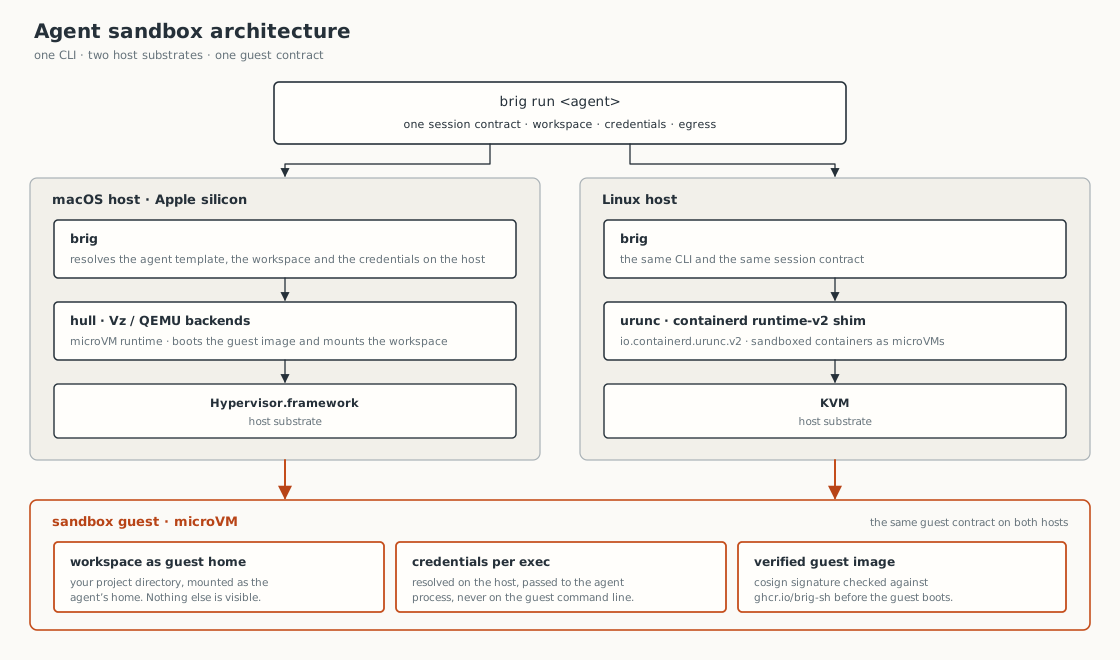
 Brig — это CLI-утилита на Go (brig) с фоновым демоном сессий (brigd), который запускает агентов для программирования внутри песочницы microVM прямо на вашем компьютере. Так автономный агент может испортить только тот один проект, который вы ему вручили.
Так что же я на самом деле запускаю — CLI, сервис или виртуальную машину?И CLI, и демон: одна команда создаёт песочницу microVM и запускает в ней агента, а все команды работают с ссылкой на сессию вроде claude или claude@refactor.
И CLI, и демон: одна команда создаёт песочницу microVM и запускает в ней агента, а все команды работают с ссылкой на сессию вроде claude или claude@refactor.Как установить программу и как выглядит первый запуск?Установите cask из Homebrew — вместе с ним ставятся runtime hull и cosign; про install.sh, Linux и сборку из исходников написано в docs/install.md. Первый запуск скачивает образ гостевой системы и загрузочные файлы, поэтому идёт медленно.
Установите cask из Homebrew — вместе с ним ставятся runtime hull и cosign; про install.sh, Linux и сборку из исходников написано в docs/install.md. Первый запуск скачивает образ гостевой системы и загрузочные файлы, поэтому идёт медленно.Программа запустится на моём компьютере или ей нужно особое железо?Mac на чипах Apple Silicon с macOS 15 или новее; на macOS 14 работает с BRIGHYPERVISOR=vz, а Mac на Intel не поддерживаются. Также подходит Linux на x86-64 или arm64, но там нужны nerdctl, containerd и shim urunc.
Mac на чипах Apple Silicon с macOS 15 или новее; на macOS 14 работает с BRIGHYPERVISOR=vz, а Mac на Intel не поддерживаются. Также подходит Linux на x86-64 или arm64, но там нужны nerdctl, containerd и shim urunc.Насколько сильно на самом деле ограничен агент?Папка проекта смонтирована в режиме чтения и записи и содержит ваши настоящие файлы, так что агент может менять в ней всё что угодно. В сети по умолчанию (shared) у него также есть доступ в интернет — всё, что он может прочитать, он может и отправить наружу.
Папка проекта смонтирована в режиме чтения и записи и содержит ваши настоящие файлы, так что агент может менять в ней всё что угодно. В сети по умолчанию (shared) у него также есть доступ в интернет — всё, что он может прочитать, он может и отправить наружу.Может ли агент подглядеть в мои другие файлы, пароли или SSH-ключи?Нет: песочница запускается без каких-либо учётных данных, а передаёте вы их только тогда, когда агент просит вас войти в систему. Он никогда не получает доступ к другим папкам вашего компьютера, к связке ключей или к вашему SSH-агенту.
Нет: песочница запускается без каких-либо учётных данных, а передаёте вы их только тогда, когда агент просит вас войти в систему. Он никогда не получает доступ к другим папкам вашего компьютера, к связке ключей или к вашему SSH-агенту.Зачем вообще запускать агента для программирования в песочнице?Автономный агент может испортить только то, что вы ему вручили: укажите ему один проект, и неудачная правка или неудачная команда дальше этого проекта не дойдут. Когда закончите, просто выбросьте песочницу и начните с чистого листа.
Автономный агент может испортить только то, что вы ему вручили: укажите ему один проект, и неудачная правка или неудачная команда дальше этого проекта не дойдут. Когда закончите, просто выбросьте песочницу и начните с чистого листа.Какие агенты для программирования поддерживаются сразу из коробки?Встроен Claude Code: имя сессии claude указывает на агента claude-code, который при первом запуске предложит вам войти в систему внутри песочницы. О запуске собственного агента рассказано в docs/profiles.md, а о собственном гостевом образе — в docs/guest-image.md.
Встроен Claude Code: имя сессии claude указывает на агента claude-code, который при первом запуске предложит вам войти в систему внутри песочницы. О запуске собственного агента рассказано в docs/profiles.md, а о собственном гостевом образе — в docs/guest-image.md.Which topics is it in?microvm, ai-safety, vm, sandboxing, virtualization, ai-coding, sandbox, apple-silicon, cli-tool, agentic-ai, coding-agent, go
microvm, ai-safety, vm, sandboxing, virtualization, ai-coding, sandbox, apple-silicon, cli-tool, agentic-ai, coding-agent, go