



What is this?
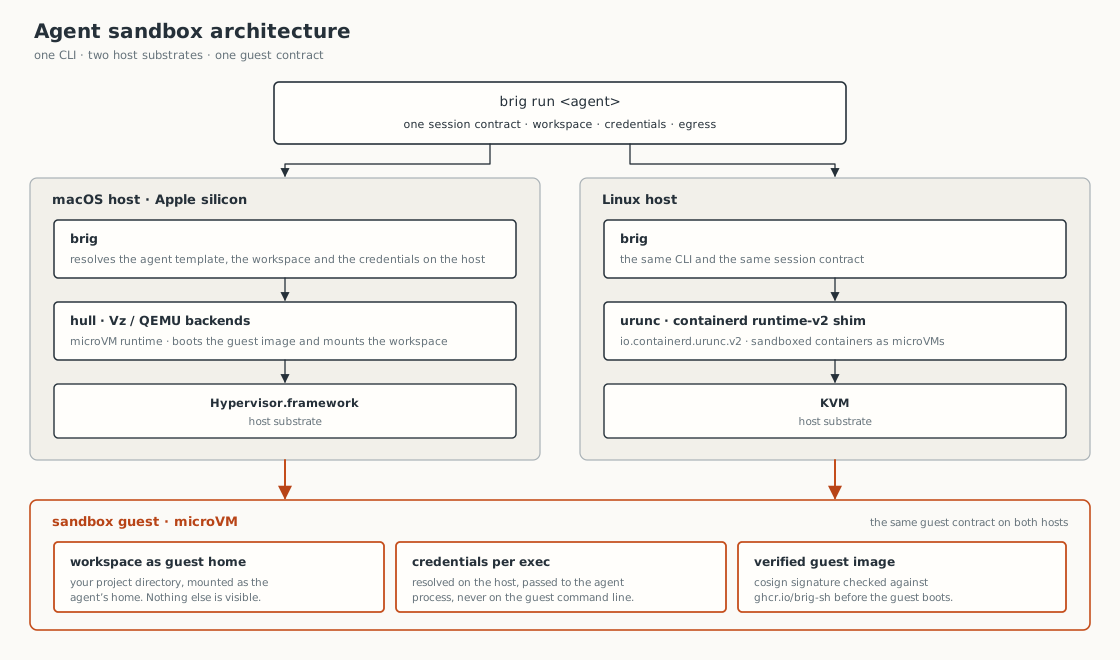
 Brig is a Go CLI (brig) with a session daemon (brigd) that runs coding agents inside a microVM sandbox on your own machine, so an unattended agent can only damage the one project you hand it.
So what am I actually running — a CLI, a service, a VM?Both a CLI and a daemon: one command starts a microVM sandbox and runs the agent in it, and every command works on a session ref like claude or claude@refactor.
Both a CLI and a daemon: one command starts a microVM sandbox and runs the agent in it, and every command works on a session ref like claude or claude@refactor.How do I install it, and what does the first run look like?Install the Homebrew cask — it brings the hull runtime and cosign with it; install.sh, Linux and source builds are covered in docs/install.md. The first run pulls the guest image and boot assets, so it is slow.
Install the Homebrew cask — it brings the hull runtime and cosign with it; install.sh, Linux and source builds are covered in docs/install.md. The first run pulls the guest image and boot assets, so it is slow.Will it run on my machine, or does it need special hardware?Apple Silicon Macs on macOS 15 or newer; macOS 14 works with BRIGHYPERVISOR=vz, and Intel Macs are not supported. Linux on x86-64 or arm64 also works, but needs nerdctl, containerd and the urunc shim.
Apple Silicon Macs on macOS 15 or newer; macOS 14 works with BRIGHYPERVISOR=vz, and Intel Macs are not supported. Linux on x86-64 or arm64 also works, but needs nerdctl, containerd and the urunc shim.How locked down is the agent, really?The project directory is mounted read-write and holds your real files, so the agent can change anything under it. On the default shared network it also reaches the internet — anything it can read, it can send out.
The project directory is mounted read-write and holds your real files, so the agent can change anything under it. On the default shared network it also reaches the internet — anything it can read, it can send out.Can the agent peek at my other files, passwords or SSH keys?No: the sandbox boots with no credentials, and you deliver them only when the agent asks you to log in. It never gets your other host directories, your keychain or your SSH agent.
No: the sandbox boots with no credentials, and you deliver them only when the agent asks you to log in. It never gets your other host directories, your keychain or your SSH agent.Why run a coding agent in a sandbox at all?An unattended agent can only damage what you hand it: point it at one project and a bad edit or a bad command reaches no further than that project. When you are done, you throw the sandbox away and start clean.
An unattended agent can only damage what you hand it: point it at one project and a bad edit or a bad command reaches no further than that project. When you are done, you throw the sandbox away and start clean.Which coding agents does it support out of the box?Claude Code is built in: the session name claude resolves to the claude-code agent, which asks you to log in inside the sandbox on first run. docs/profiles.md covers running your own agent, and docs/guest-image.md your own guest image.
Claude Code is built in: the session name claude resolves to the claude-code agent, which asks you to log in inside the sandbox on first run. docs/profiles.md covers running your own agent, and docs/guest-image.md your own guest image.Which topics is it in?microvm, ai-safety, vm, sandboxing, virtualization, ai-coding, sandbox, apple-silicon, cli-tool, agentic-ai, coding-agent, go
microvm, ai-safety, vm, sandboxing, virtualization, ai-coding, sandbox, apple-silicon, cli-tool, agentic-ai, coding-agent, go