Apache Casbin


News: still worry about how to write the correct Apache Casbin policy? Apache Casbin online editor is coming to help! Try it at: https://casbin.apache.org/editor/

Apache Casbin is a powerful and efficient open-source access control library for Golang projects. It provides support for enforcing authorization based on various access control models.
All the languages supported by Apache Casbin:
Table of contents
Supported models
- ACL (Access Control List)
- ACL with superuser
- ACL without users: especially useful for systems that don't have authentication or user log-ins.
- ACL without resources: some scenarios may target for a type of resources instead of an individual resource by using permissions like
write-article, read-log. It doesn't control the access to a specific article or log.
- RBAC (Role-Based Access Control)
- RBAC with resource roles: both users and resources can have roles (or groups) at the same time.
- RBAC with domains/tenants: users can have different role sets for different domains/tenants.
- ABAC (Attribute-Based Access Control): syntax sugar like
resource.Owner can be used to get the attribute for a resource.
- RESTful: supports paths like
/res/*, /res/:id and HTTP methods like GET, POST, PUT, DELETE.
- Deny-override: both allow and deny authorizations are supported, deny overrides the allow.
- Priority: the policy rules can be prioritized like firewall rules.
How it works?
In Casbin, an access control model is abstracted into a CONF file based on the PERM metamodel (Policy, Effect, Request, Matchers). So switching or upgrading the authorization mechanism for a project is just as simple as modifying a configuration. You can customize your own access control model by combining the available models. For example, you can get RBAC roles and ABAC attributes together inside one model and share one set of policy rules.
The most basic and simplest model in Casbin is ACL. ACL's model CONF is:
# Request definition
[request_definition]
r = sub, obj, act

# Policy definition
[policy_definition]
p = sub, obj, act

# Policy effect
[policy_effect]
e = some(where (p.eft == allow))

# Matchers
[matchers]
m = r.sub == p.sub && r.obj == p.obj && r.act == p.act
An example policy for ACL model is like:
p, alice, data1, read
p, bob, data2, write
It means:
- alice can read data1
- bob can write data2
We also support multi-line mode by appending '\' in the end:
# Matchers
[matchers]
m = r.sub == p.sub && r.obj == p.obj \
  && r.act == p.act
Further more, if you are using ABAC, you can try operator in like following in Casbin golang edition (jCasbin and Node-Casbin are not supported yet):
# Matchers
[matchers]
m = r.obj == p.obj && r.act == p.act || r.obj in ('data2', 'data3')
But you SHOULD make sure that the length of the array is MORE than 1, otherwise there will cause it to panic.
For more operators, you may take a look at govaluate
Features
What Apache Casbin does:
- enforce the policy in the classic
{subject, object, action} form or a customized form as you defined, both allow and deny authorizations are supported.
- handle the storage of the access control model and its policy.
- manage the role-user mappings and role-role mappings (aka role hierarchy in RBAC).
- support built-in superuser like
root or administrator. A superuser can do anything without explicit permissions.
- multiple built-in operators to support the rule matching. For example,
keyMatch can map a resource key /foo/bar to the pattern /foo*.
What Apache Casbin does NOT do:
- authentication (aka verify
username and password when a user logs in)
- manage the list of users or roles. I believe it's more convenient for the project itself to manage these entities. Users usually have their passwords, and Apache Casbin is not designed as a password container. However, Apache Casbin stores the user-role mapping for the RBAC scenario.
Installation
go get github.com/casbin/casbin/v3
Documentation
https://casbin.apache.org/docs/overview
Online editor
You can also use the online editor (https://casbin.apache.org/editor/) to write your Casbin model and policy in your web browser. It provides functionality such as syntax highlighting and code completion, just like an IDE for a programming language.
Tutorials
https://casbin.apache.org/docs/tutorials
Get started
New a Casbin enforcer with a model file and a policy file:
e, _ := casbin.NewEnforcer("path/to/model.conf", "path/to/policy.csv")
Note: you can also initialize an enforcer with policy in DB instead of file, see Policy-persistence section for details.
Add an enforcement hook into your code right before the access happens:
sub := "alice" // the user that wants to access a resource.
obj := "data1" // the resource that is going to be accessed.
act := "read" // the operation that the user performs on the resource.

if res, _ := e.Enforce(sub, obj, act); res {
    // permit alice to read data1
} else {
    // deny the request, show an error
}
Besides the static policy file, Apache Casbin also provides API for permission management at run-time. For example, You can get all the roles assigned to a user as below:
roles, _ := e.GetImplicitRolesForUser(sub)
See Policy management APIs for more usage.
Policy management
Apache Casbin provides two sets of APIs to manage permissions:
- Management API: the primitive API that provides full support for Apache Casbin policy management.
- RBAC API: a more friendly API for RBAC. This API is a subset of Management API. The RBAC users could use this API to simplify the code.
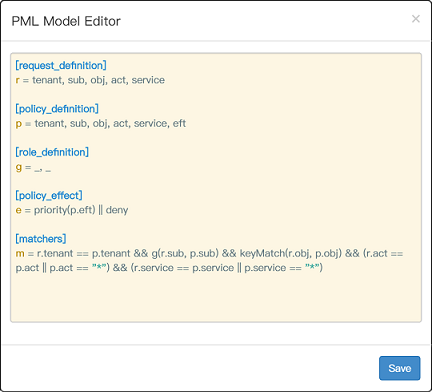
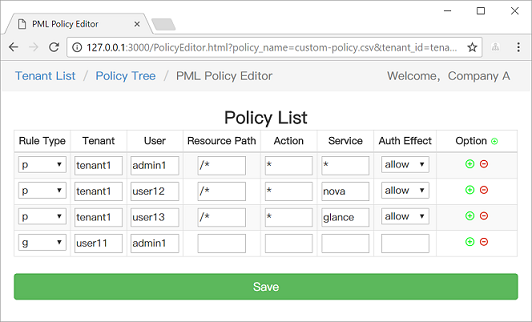
We also provide a web-based UI for model management and policy management:
Policy persistence
https://casbin.apache.org/docs/adapters
Policy consistence between multiple nodes
https://casbin.apache.org/docs/watchers
Role manager
https://casbin.apache.org/docs/role-managers
Benchmarks
https://casbin.apache.org/docs/benchmark
Examples
Middlewares
Authz middlewares for web frameworks: https://casbin.apache.org/docs/middlewares
Our adopters
https://casbin.apache.org/docs/adopters
How to Contribute
Please read the contributing guide.
Contributors
This project exists thanks to all the people who contribute.

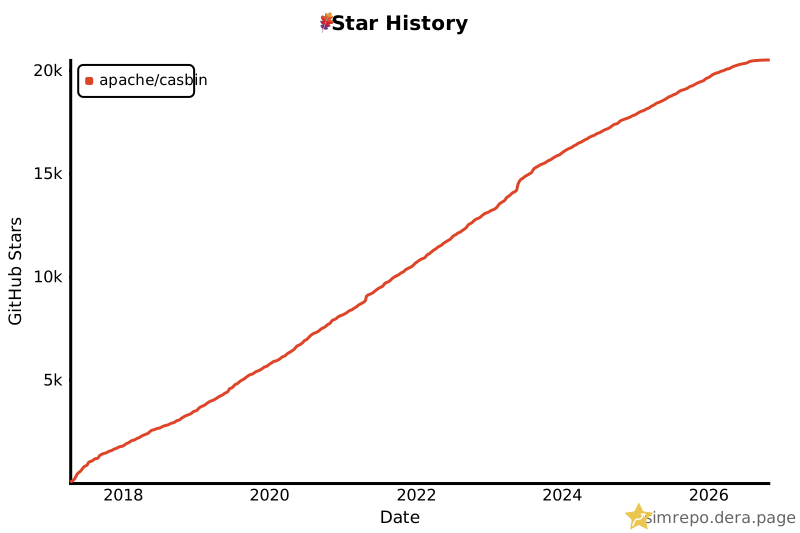
Star History
License
This project is licensed under the Apache 2.0 license.
If you have any issues or feature requests, please contact us. PR is welcomed.

 一个面向 Go 项目的开源访问控制库:它基于可配置的模型(如 ACL、RBAC 和 ABAC)来执行授权。