Topics / #permissions
Permissions projects on GitHub
Permission systems controlling user access to resources
As of , the most-starred Permissions projects on GitHub are casbin (20.5K stars), PermissionsDispatcher (11.1K stars) and RxPermissions (10.4K stars). GitHub.Locker tracks 6 Permissions repositories with 43K stars combined. The fastest-growing on October 16 was casbin, with +5 stars in a day.
Hot right now
Most stars gained in a day · Oct 16
The all-time top
6 projects · by stars
- 20.5K
 #1 · apache/casbin
casbin
An open-source access control library for Go projects: it enforces authorization based on configurable models like ACL, RBAC and ABAC.
- 11.1K
 #2 · permissions-dispatcher/PermissionsDispatcher
PermissionsDispatcher
PermissionsDispatcher is an annotation-based library for Android that generates the boilerplate code needed to request and check runtime permissions, so you do not have to write permission check statements by hand.
- 10.4K
 #3 · tbruyelle/RxPermissions
RxPermissions
An open-source Android library that handles runtime permissions through RxJava2, wrapping the Android M permission model in observables.
- 4
casbin-gateway
642apache/casbin-gateway · GoAn open-source gateway for the AI coding agents on your machine: it watches what every agent does, relays their model traffic through one endpoint covering 44 vendors, and grades whether the API behind each key is what you actually paid for.
- 5
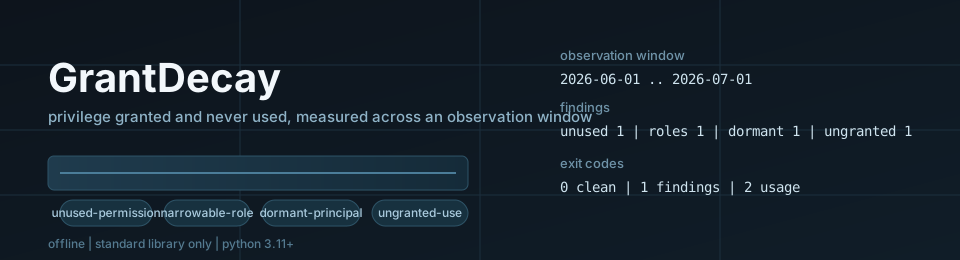
GDecay
197shivanipoddariiith/GDecay · PythonGrantDecay is a CLI tool that finds privilege that was granted but never used. It compares an entitlement export (who holds which permissions) against an access log export covering a time window, then reports unused permissions, narrowable roles, dormant principals, and ungranted use.
- 6
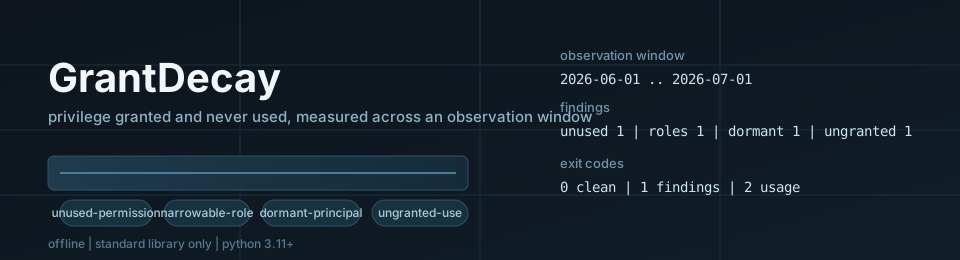
GrantDecay
128rojiloro/GrantDecay · PythonGrantDecay is a CLI that compares what each principal was granted against what it actually used over an observation window, and reports unused permissions, narrowable roles, dormant principals, and ungranted use.
Related topics
Often tagged together