AI coworkers you can hand real work to, and actually trust with the access. Each gets a computer of its own: a real browser with its own logins, its own files, and only the tools you grant. Every action decided before it happens and recorded after.
Bring any AG-UI agent, written on a framework or by hand, and it arrives as a
coworker with a channel of its own. Watch it work on its own screen, take the
wheel when it reaches something it should not do alone, then hand it back. It
answers with components rather than only prose, and the whole thing runs on
your own machine.
A template, not a product. OpenBot is meant to be cloned and made your own. There is no hosted version to sign up for, and nothing here is published as a package to depend on: every workspace in this repository is private. You take the repository, replace the example tenant package under examples/ with your own coworkers, channels and skills, and run it. Everything below describes a starting point, not a finished thing somebody operates for you.
Alpha, and under active development. OpenBot is early. Expect rough edges and bugs, and expect things to move. Issues and pull requests are welcome.
Runs on your machine. Everything below is written for a laptop. .env.example carries OPENBOT_SINGLE_USER=true, which admits every request as one administrator, so a fresh clone reaches the product without registering an OAuth client first. Sign-in turns that off, and is required before anybody else can reach the deployment.
What it is
An agent platform that runs inside your own infrastructure. Docker Compose brings up every part of it, the data sits in your PostgreSQL, and the model is yours to choose: no model ships in the box, and an administrator supplies the credential, which is encrypted at rest and never logged.
Three coworkers ship in the example package, and they are configuration rather than code: General Assistant for everyday work, Knowledge for company questions, Risk Analyst for risk and compliance. Add your own by editing agents.yaml or from /agents in the UI.
Anything a Bot does to a computer, a file, an MCP server or a component goes through one gateway that decides and records it. That is the difference between an agent that can use your tools and an agent you can let near them.
A Bot is any endpoint speaking AG-UI, the open protocol for agent-to-user interaction, so OpenBot is not tied to a framework and neither are you. Agents built with LangGraph, Mastra, CrewAI, Pydantic AI, Google ADK or written by hand all arrive the same way, and the governance rides the protocol rather than the framework.
A CopilotKit Intelligence project and license. A free plan is available, and Intelligence can be self-hosted.
A model key. The proof-of-concept Bot uses OpenAI; the LangGraph Bot can use OpenAI, Anthropic, or Google.
Quick start
Setting up with an AI assistant? Paste prompt.txt into it first. It carries the
same steps as below plus the things that are easy to get wrong: which of the ten blank keys in
.env.example are actually yours to fill (three), which the start script generates for you, and
what each start-up refusal means. Every claim in it is checked against this repository.
Put the cpk-... runtime key from project select in .env as
INTELLIGENCE_API_KEY. That is the only Intelligence credential you need:
managed Intelligence derives entitlement from the project key, so there is
no separate licence token to fetch.
Fill the remaining required values:
OPENAI_API_KEY
Keep the managed Intelligence URLs from .env.example unless you run Intelligence yourself. The example KEY_ENCRYPTION_KEY is public and fine locally; generate your own with:
scripts/start.sh starts Docker services, applies migrations, starts the API server on port 3001, starts the app on port 3010, and checks that the services answer their own health routes before printing next steps.
scripts/stop.sh takes the same things down, including each Bot's computer, which compose does not own. Nothing is deleted: the database, the Bots' files and their browser profiles are volumes.
Deploy it
One image carries the app, the API, the browser the Bots drive, and optionally PostgreSQL. Same
.env, no Kubernetes.
Leave EMBEDDED_POSTGRES off and set DATABASE_URL to point at a database you already run.
docs/deployment.md has the minimum sizes, the platform notes, and how it behaves behind more than one replica.
Try it
Open /bot and ask: Open news.ycombinator.com and tell me the top story.
Open /admin/boundaries, add a deny rule or preset, and retry the same browser action.
Create a coworker from /agents, give it a standing role, and start a channel with it.
Main surfaces
Route
Purpose
/
Start and browse channels.
/agents
Create, edit, duplicate, hide, delete, and launch coworkers.
/channel/:id
Converse with one coworker, watch its screen, and see what it ran.
/bot
Direct chat with a Bot; ?agent=<id> selects one.
/skills
Create and enable personal skills.
/settings
User preferences.
/admin/credentials
Store write-only encrypted credentials.
/admin/computers
View, stop, and reset Bot computers.
/admin/boundaries
Configure browser/file/MCP action policy.
/admin/components
Publish components and govern which Bots may use them.
/admin/playground
Draft and publish sandboxed components in the browser.
/admin/plugins
Configure MCP servers, MCP grants, and deployment skills.
/admin/audit
Review permitted, refused, and failed actions.
Features
A computer per Bot: the supervisor gives each Bot its own container, its own /workspace volume and its own browser profile. Set COMPUTER_RUNTIME=runsc to run them under gVisor where the host supports it.
A shell, not just a browser: a Bot can run a command in its workspace, install what it needs, and process a file it saved. Through the same gate as everything else, so a rule can refuse a shell outright or refuse particular commands, and the command is on the record either way. The command inherits PATH, locale, terminal and proxy variables, not the rest of the deployment's environment.
The gateway is the only way in: it resolves the target from a server-held snapshot, evaluates the policy, writes the audit row, and only then calls the computer. There is no path that acts without the record existing first.
CEL policy, fail closed: rules can inspect tool.name, intent, bot.id, actor.id, page.url, page.host, element.*, key, file.* and mcp.*. Deny is evaluated before allow, a missing policy permits nothing, and a broken rule refuses rather than opens.
Watch what it is doing: the screen shows what a Bot is looking at, and the Activity tab beside it shows what it ran, read and saved, with the output. A command line in the transcript opens to the same thing. A saved file shows its path and size, never its contents.
Take the wheel: a Bot that hits a login wall or a 2FA prompt asks for help. Control is handed over in the same panel and recorded as computer.help_requested, computer.control_taken and computer.control_released. While a person is driving, Bot actions are refused rather than queued.
Secrets never enter the transcript: the trail records that a secret was requested and how long it was, not what it said.
Bring your own agent: any AG-UI endpoint is a Bot, on a framework or hand-written. Endpoints are validated with the same target checks used for browser navigation, and an auth header is stored write-only.
Components instead of prose: compiled React components live in app/src/components/gallery/, sandboxed ones are authored in /admin/playground and published with no deployment. Every call asks the server whether the component exists, is published, and is not withheld from that Bot. Data functions are granted per component.
Governed MCP: Google Drive and Notion ship in the catalogue, reached as the person asking. The catalogue carries only vendors this deployment stands behind, so adding one is a review of that vendor. Custom servers must pass URL checks; unknown tools and custom-server tools are treated as writes, and a catalogue tool the server advertises but does not name as a write classifies as a read. A Bot is told which connectors exist here and which it holds, so it says it has not been granted one rather than browsing to the vendor's website.
Skills are instructions, not capabilities: personal skills attach only to Bots their author owns, deployment skills are admin-owned, and both are invoked with / in the composer. A Bot granted the shipped skill-creator skill can write one with you in the conversation, and saves it only when you press the button on the card.
Sign in with what your company already has: Google, Microsoft or Okta from the environment, or a company's own SAML or OpenID Connect provider registered while the deployment runs and routed by email domain. Any one turns sign-in on; several may be configured at once.
Decide who gets in: /admin/people lists everybody who has signed in, promotes and demotes them, and removes access, which ends the session they are using and stops the next sign-in. Every change is on the audit trail.
An audit trail you can read: /admin/audit lists what was permitted, what was refused and what failed, and every refusal carries the rule that caused it.
Credentials encrypted at rest: stored through /admin/credentials, never returned by an API, and redacted from audit events.
Loopback by default: computers bind to 127.0.0.1 and require a per-container token, so nothing reaches a logged-in browser by knowing its port. The supervisor binds there too, because it holds the Docker socket and its token is a shared secret rather than a network boundary.
Durable threads and memory: conversations survive restarts through CopilotKit Intelligence, and each deployment stamps the threads it owns.
Routines: ask a Bot to do something on a schedule and it does, running as you, in the channel you asked in. A 15-minute floor and a cap of 20 enabled routines keep a sentence from scheduling more than a person meant, and ten failures in a row switch a routine off rather than burn model spend forever. Needs a worker process; see docs/routines.md.
Bring your own agent
Any AG-UI endpoint can be a Bot.
From /agents, create a coworker with:
name, title, and role description;
private or public visibility;
optional AG-UI endpoint;
optional write-only authorization header.
The server validates agent endpoints with the same target checks used for browser navigation, at registration and again on every redirect the endpoint answers with. If no custom endpoint is set, product-created coworkers use MANAGED_AGENT_AG_UI_URL when it is configured, and are refused when it is not.
A private address is refused unless it is listed in AGENT_ENDPOINT_ALLOWED_HOSTS:
A host on its own covers any port on that host; a host with a port pins that port. Matching is exact: no wildcards, no suffixes. An entry written as a URL, or containing *, stops startup and names that entry.
The list covers agent endpoints only. Browsing is unaffected, the addresses holding a deployment's own cloud credentials are refused whatever is listed, and listing an address permits registering an agent there rather than granting that agent anything.
Tenant package agents are declared in agents.yaml as either:
.env.example is the source template. The API server refuses to start without:
DATABASE_URL
KEY_ENCRYPTION_KEY
INTELLIGENCE_API_URL
INTELLIGENCE_GATEWAY_WS_URL
INTELLIGENCE_API_KEY
COPILOTKIT_LICENSE_TOKEN is optional. A self-hosted Intelligence with its own
licence can still set it and it is forwarded to the runtime; managed Intelligence
does not issue one and startup no longer asks for it.
Settings worth knowing:
Variable
Use
OPENBOT_SINGLE_USER
Admits every request as one administrator. Required when no identity provider is configured; .env.example ships it on.
OPENAI_BASE_URL
Answers the OpenAI-shaped calls from somewhere else: a gateway, a proxy.
ANTHROPIC_BASE_URL, GOOGLE_GENERATIVE_AI_BASE_URL
The same, for those two APIs.
COMPUTER_TOKEN
Secret every Bot computer request must present. start.sh sets one.
SUPERVISOR_TOKEN
Secret the supervisor requires. start.sh sets one.
AGENT_TOOL_TOKEN
Secret a Bot presents to call a granted tool back. start.sh sets one. Without it no Bot may call tools.
COMPUTER_SUPERVISOR_URL
Gives each Bot a computer of its own instead of one shared computer.
COMPUTER_RUNTIME
Set to runsc to run computers under gVisor, where the host has it.
COMPUTER_SANDBOX
Set to on for Chromium's own sandbox, where the host permits it.
EMBEDDED_POSTGRES
Set to on for a database inside the deployment container.
AGENT_COMPUTER_POLICY
JSON action policy. Malformed JSON stops server startup.
AGENT_COMPUTER_ALLOW_PRIVATE_HOSTS
Lets a Bot reach this machine's own services. Local only, and refused under NODE_ENV=production.
AGENT_ENDPOINT_ALLOWED_HOSTS
Private addresses an agent may be registered at, comma separated. A host, optionally with a port.
TENANT_PACKAGE_DIR
Directory containing tenant YAML. Defaults to ../examples/fintech.
DEPLOYMENT_ID
Names this deployment when two share one Intelligence project.
Product data, policy, audit, credentials, grants, channels, and component metadata.
CopilotKit Intelligence
external
Durable threads and memory.
The server gateway is the product/API path for Bot browser and file tool calls.
It resolves the target, evaluates policy, writes an audit row, and then calls
agent-computer. The computer also exposes lower-level token-protected service
endpoints; keep them private and do not use them to bypass the gateway.
.env.example ships OPENBOT_SINGLE_USER=true, which is one administrator and no sign-in: how a
fresh clone reaches the product without registering an OAuth client first. Delete that line and
configure any one of Google, Microsoft or Okta before anybody else can reach the deployment.
With neither, it refuses to start rather than admitting e
OpenBot (CopilotKit/OpenBot)
Choose a tag and it will appear here. With no tags selected, all catalog projects are shown.
Searching Database…
Choose a tag and it will appear here. With no tags selected, all catalog projects are shown.
What is this?OpenBot is a self-hosted platform for running AI coworkers that each get a computer of their own (a browser, files, and only the tools you grant), with a policy gateway that decides every action before it happens and logs it afterward.
Is this a finished product I can sign up for, or something I build from?It is explicitly a template meant to be cloned: there is no hosted version, nothing is published as a package, and you are expected to replace the example coworkers with your own.
How do I get it running?Clone the repo, create a .env from .env.example, get a CopilotKit Intelligence API key and an OpenAI key, then install and run the stack with Bun while Docker Compose brings up PostgreSQL and the Bot computers.
What do I need installed before trying it?You need Docker (for PostgreSQL and the shipped Bots), Bun 1.3+ (for the app and API server), a CopilotKit Intelligence project (a free plan exists and it can be self-hosted too), and a model key such as OpenAI's.
How stable is this right now?The project is explicitly alpha and under active development, so expect rough edges and bugs while things keep changing.
How are my credentials and secrets handled?Credentials are encrypted at rest, stored only through the admin credentials panel, never returned by an API, and redacted from audit events; secrets are never written into the transcript.
What coworkers come pre-configured in the example?The example tenant package ships three: General Assistant for everyday work, Knowledge for company questions, and Risk Analyst for risk and compliance, meant to be replaced with your own.
What does a Bot's own 'computer' actually consist of?Each Bot gets its own container with a dedicated /workspace volume and its own browser profile, optionally run under gVisor sandboxing via COMPUTER_RUNTIME=runsc.
Can a person take over when a Bot gets stuck, like at a login screen?Yes, a Bot facing a login wall or 2FA prompt can request help; a person takes control from the same panel, and the handoff is logged as computer.help_requested, computer.control_taken and computer.control_released.
What happens if a Bot tries to use a tool it was not granted?It reports that it has not been granted that connector instead of navigating to the vendor's site, since a Bot is only told which connectors it actually holds.


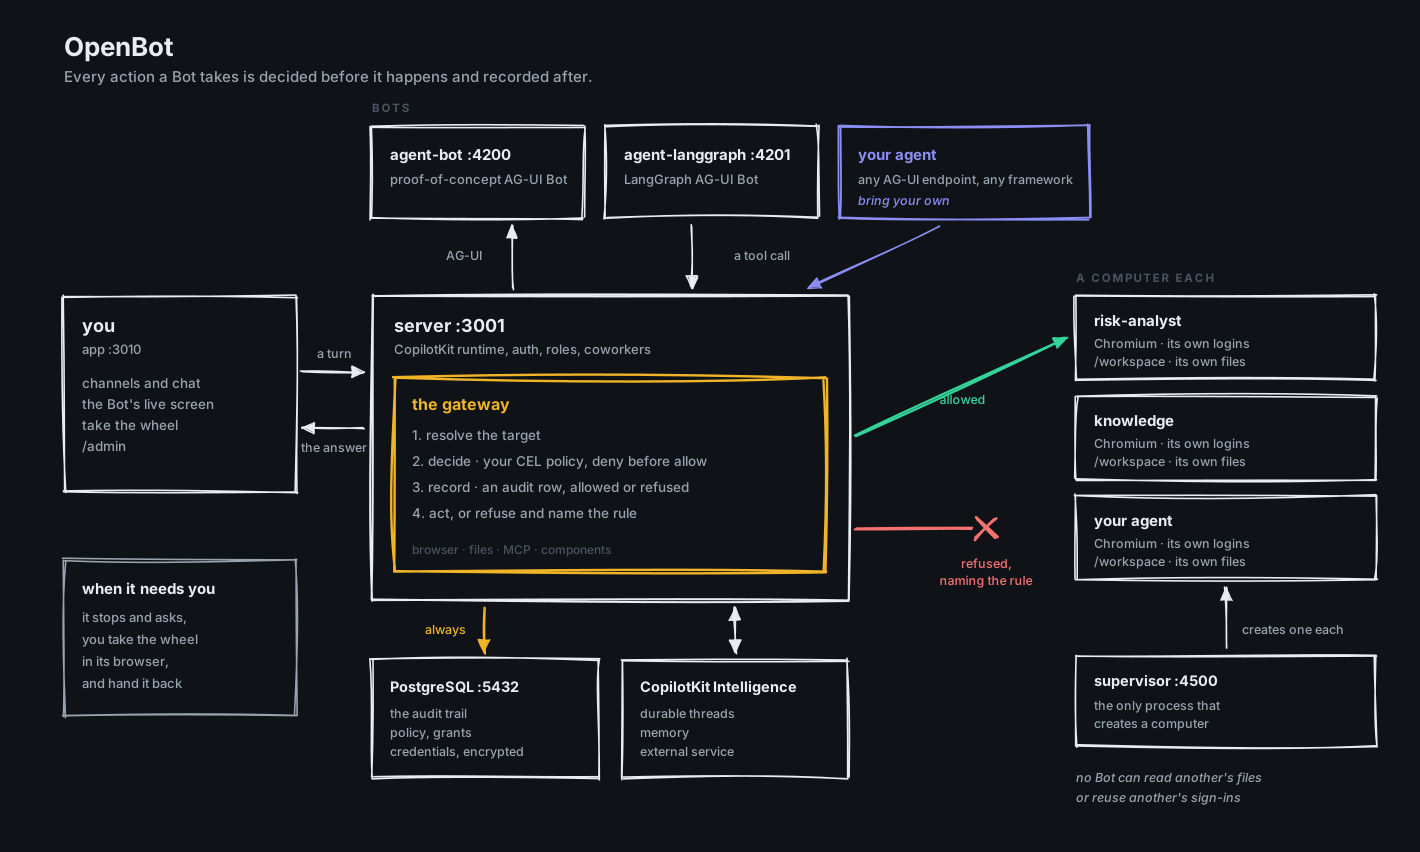

 OpenBot is a self-hosted platform for running AI coworkers that each get a computer of their own (a browser, files, and only the tools you grant), with a policy gateway that decides every action before it happens and logs it afterward.